 En.Defence-Ua
US and UK Collaborate on Underwater Drone Defense Initiative
Article Content

- •US and UK are developing a new underwater drone defense system called REEF.
- •The system aims to protect critical infrastructure from unmanned underwater threats.
- •Non-kinetic methods like bubble curtains and decoys will be prioritized in the defense strategy.
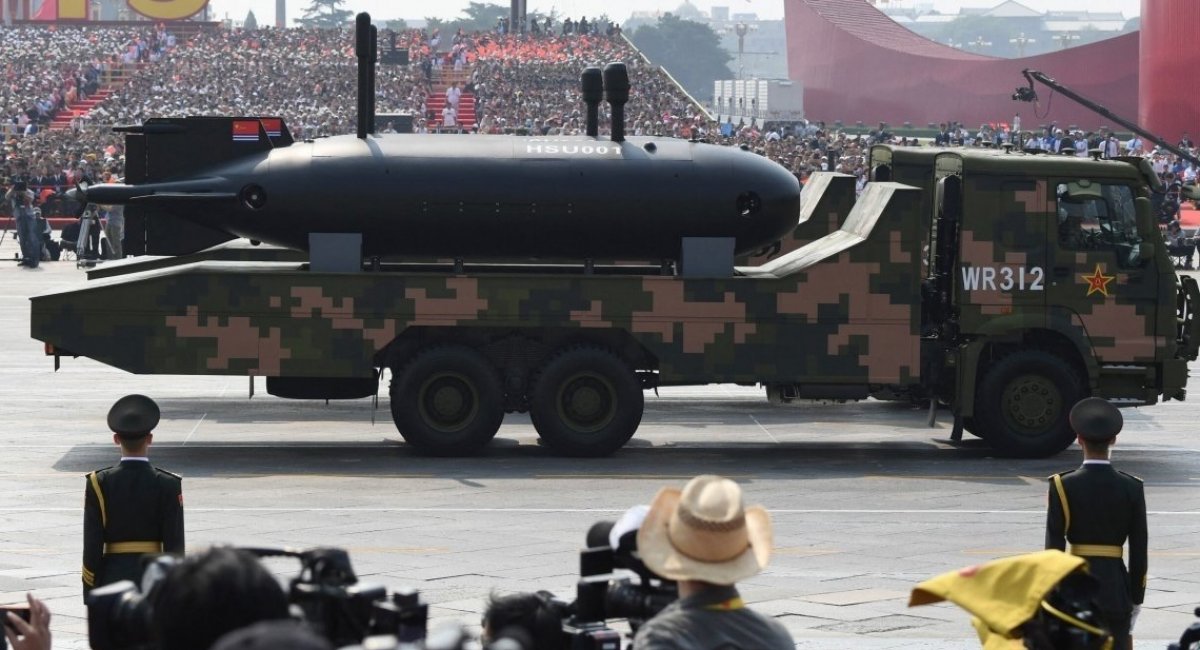
The United States and the United Kingdom are launching a joint project called the Robotic Exclusion and Engagement Framework (REEF) to counter the threat posed by underwater drones to critical infrastructure, particularly ports. This initiative, announced by the Pentagon's Defense Innovation Unit, aims to create a comprehensive defense system that can detect and neutralize unmanned underwater vehicles, remotely operated vehicles, and semisubmersibles. Current solutions are deemed inadequate, prompting the need for a new system that integrates various sensors and artificial intelligence for threat identification. The REEF project will utilize both kinetic and non-kinetic countermeasures, with a focus on non-kinetic methods such as nets and bubble curtains. The system is designed for rapid deployment and minimal operational training. The collaboration is also facilitated by recent regulatory changes allowing easier sharing of technology between the two nations. This initiative reflects a growing concern over maritime threats, particularly from state actors like Iran, which has increasingly employed maritime drones in strategic waterways.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…