 Interestingengineering
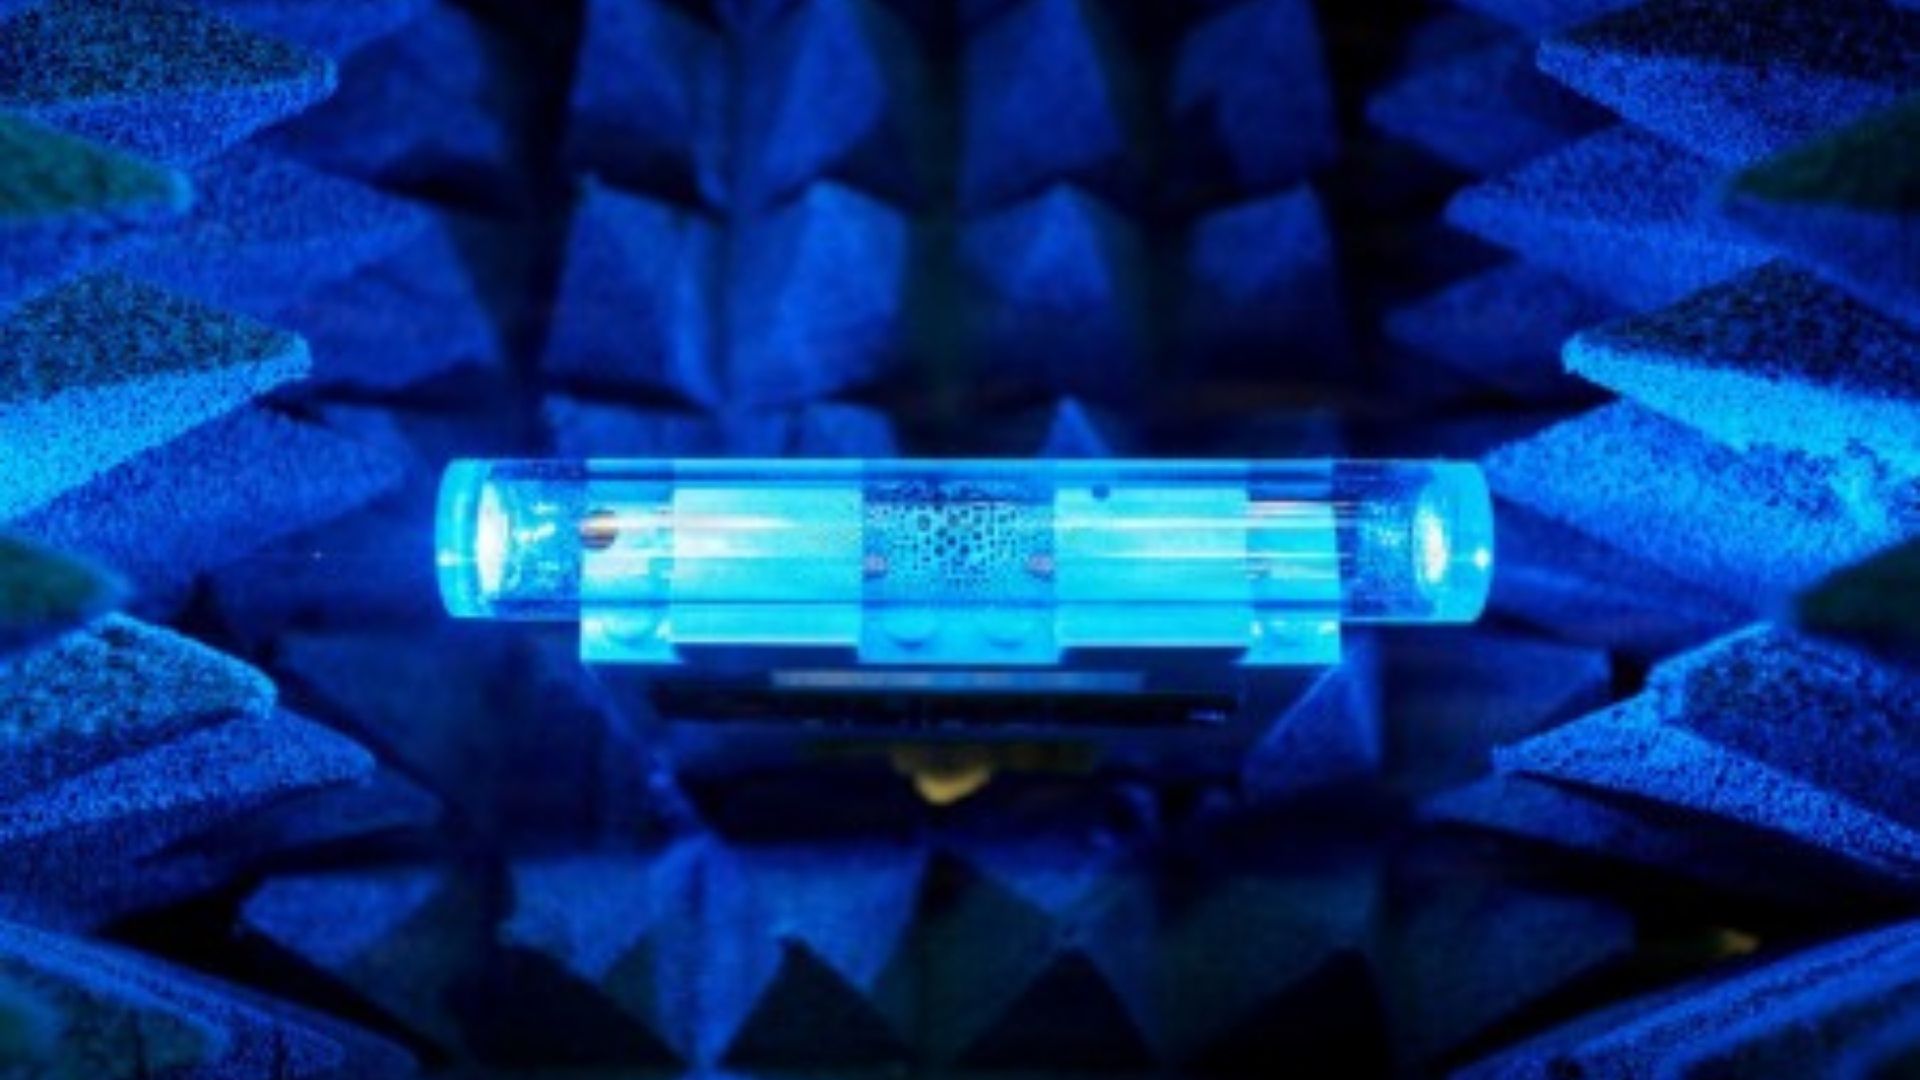
US Army Develops Quantum Sensor for Enhanced Battlefield Signal Detection
Article Content

- •The Army's new quantum sensor can measure the full 3D direction of radio-frequency signals.
- •It enhances situational awareness and decision-making capabilities for soldiers on the battlefield.
- •The sensor operates across the entire radio-frequency spectrum and is only a few centimeters in size.
Army scientists have developed a groundbreaking quantum sensor capable of measuring the full 3D direction of radio-frequency electromagnetic fields. This innovation, achieved by the U.S. Army Combat Capabilities Development Command (DEVCOM), could significantly enhance situational awareness, secure communications, and decision-making for soldiers in complex battlefield environments. The sensor utilizes Rydberg atoms to detect not only the strength of electromagnetic fields but also their 3D polarization orientation and propagation direction. Unlike traditional sensors that measure in one direction, this device provides a comprehensive 3D picture of the electromagnetic environment. Its small size and broad operational range make it adaptable for various battlefield scenarios. The sensor's accuracy in determining signal direction is within two degrees, making it a highly effective tool for locating radio-frequency signals. This development marks a significant milestone in quantum sensing technology for military applications.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…