 Therecord.Media
US Offers $10 Million Reward for Chinese Hacker Linked to COVID-19 Research Attacks
Article Content

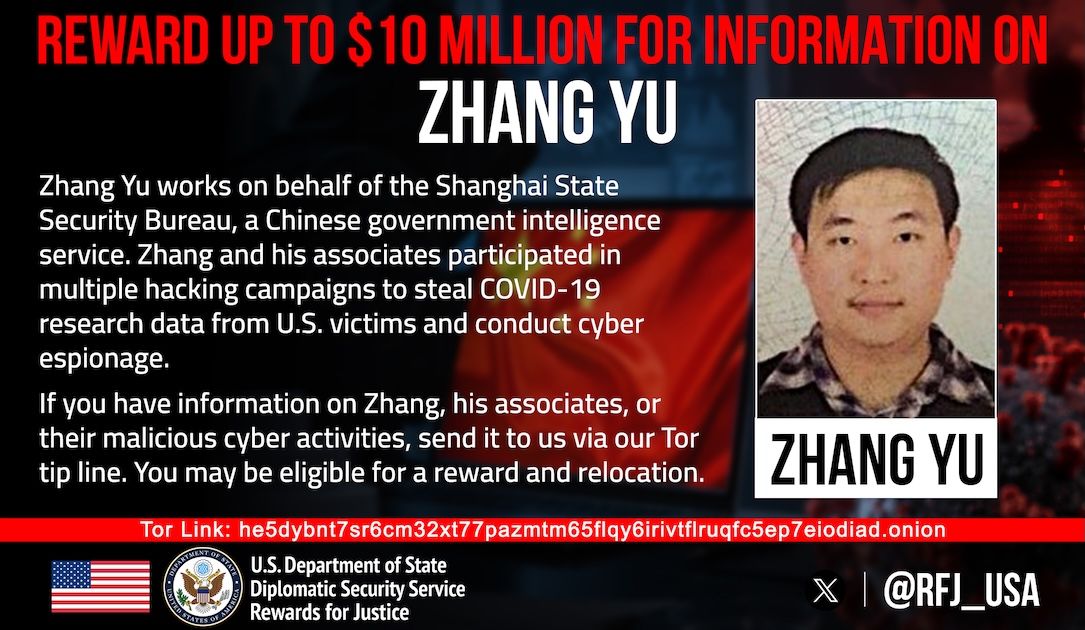
- •The U.S. offers a $10 million reward for information on Zhang Yu, a Chinese hacker.
- •Zhang is accused of targeting COVID-19 research through state-sponsored cyberattacks.
- •The HAFNIUM campaign compromised thousands of computers globally, exploiting Microsoft Exchange vulnerabilities.
The U.S. State Department has announced a reward of up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national accused of cyberattacks targeting U.S. COVID-19 researchers. Zhang is alleged to have worked with Xu Zewei and others under the direction of China's Ministry of State Security (MSS), conducting intrusions between February 2020 and June 2021. These attacks were part of the HAFNIUM campaign, which exploited vulnerabilities in Microsoft Exchange Server and compromised thousands of computers worldwide. The hackers targeted U.S.-based universities and organizations involved in COVID-19 research, stealing sensitive information. Xu was arrested in Italy in July 2025 and extradited to the U.S. in April 2026, facing multiple charges. Zhang remains at large, and the U.S. government is actively seeking information about him and his associates.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (9)
Following this threat?
Track Hafnium and CVE-2026-88771 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific activities is Zhang Yu accused of?
What should organizations do to protect themselves?
Is there a timeline for Zhang's capture?
Continue Reading
 FBI Disrupts Chinese State-Sponsored Exploitation of Microsoft Exchange Vulnerabilities On April 13, 2021, the FBI executed a novel operation to remove malicious web shells from U.S.-based computers, attributed to the Chinese state-sponsored group Hafnium. These web shells exploited zero-day vulnerabilities in Microsoft Exchange servers, allowing unauthorized access and persistent malware deployment.…
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…