 Ctvnews.Ca
US Revives Nuclear Plants to Meet Data Center Energy Demand
Article Content

- •Three U.S. nuclear plants are being revived to meet energy demands from data centers.
- •The Department of Energy is providing $4.4 billion for the restart of these facilities.
- •Safety concerns are raised regarding the aging infrastructure of the plants being revived.
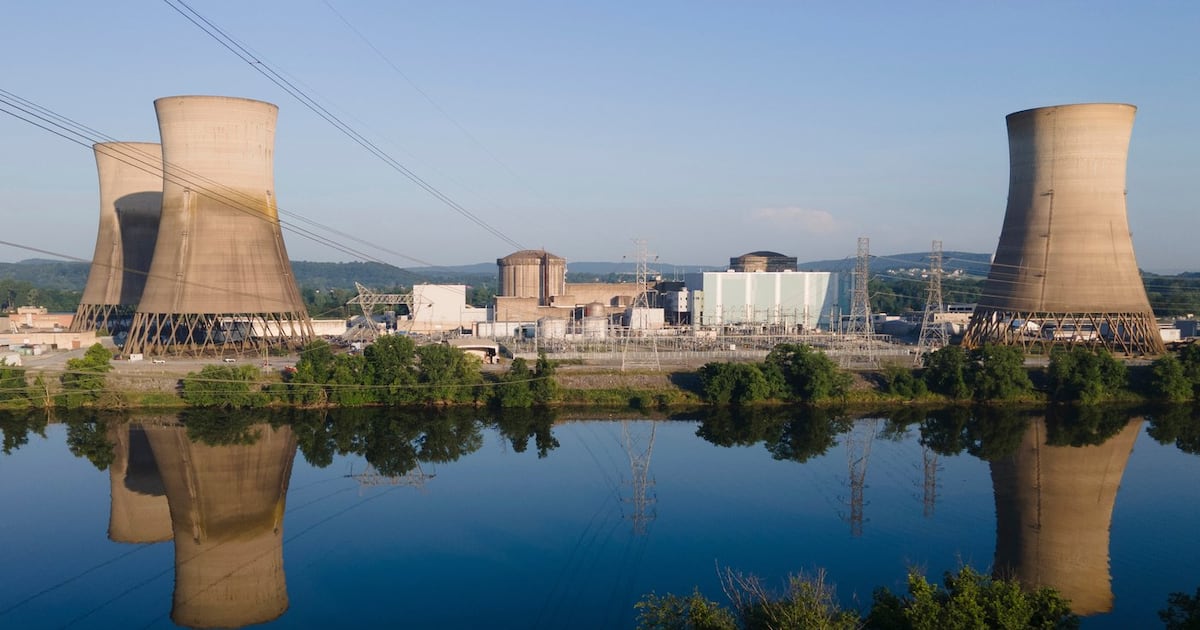
The U.S. is reviving three decommissioned nuclear plants to address rising electricity demand, particularly from data centers. The Department of Energy is providing up to $4.4 billion to restart the Palisades Power Plant in Michigan, the Crane Clean Energy Center on Pennsylvania's Three Mile Island, and the Duane Arnold Energy Center in Iowa, aiming to restore 2.25 gigawatts of power. These plants were previously closed due to high operational costs but now have contracts with major tech companies for carbon-free energy. Experts highlight that restarting these reactors is quicker and cheaper than building new ones, although safety concerns remain due to outdated infrastructure. The Trump administration is pushing for nuclear energy to support AI and manufacturing sectors. Critics argue that taxpayer funds should prioritize safety improvements over reviving older plants.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Common questions
Which plants are being revived?
What is the purpose of reviving these plants?
What are the safety concerns?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…