 Finance.Biggo
U.S. Robotics Firms Face Supply Chain Challenges Amid Chinese Tech Restrictions
Article Content

- •U.S. robotics firms are increasingly restricted from using Chinese technology.
- •Chef Robotics is struggling to find domestic suppliers for essential components.
- •The FCC has expanded its list of banned technologies impacting multiple sectors.
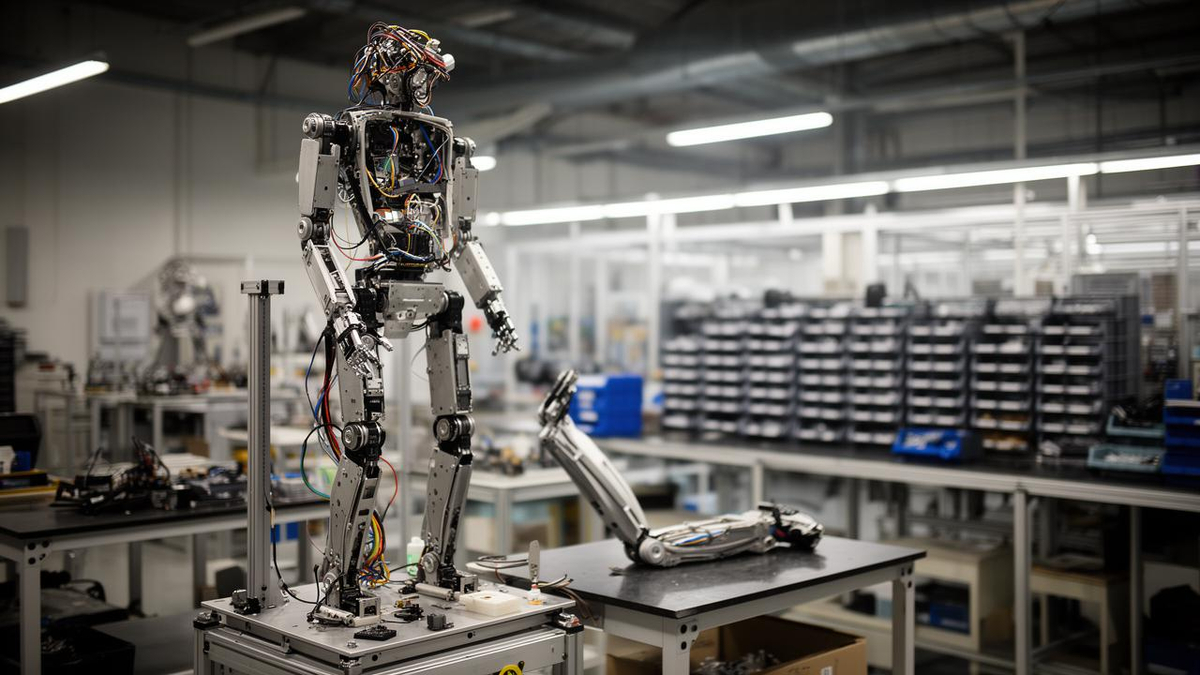
U.S. robotics companies, particularly Chef Robotics, are struggling to build robots without relying on Chinese components due to increasing restrictions imposed by the U.S. government. The shift in procurement strategy is driven by national security concerns, prompting investors and customers to question the use of foreign-made parts. The Federal Communications Commission (FCC) has expanded its list of banned technologies, affecting various sectors, including robotics and automotive. Chef Robotics, while still able to use some components, anticipates further restrictions that could impact their production. The company has faced difficulties in finding alternative suppliers domestically, as many lack the capacity to meet demand. Experts warn that the U.S. manufacturing sector may not be prepared to fill the gap left by Chinese suppliers, leading to higher costs and longer wait times for consumers and businesses. The situation reflects a broader trend of U.S. companies reevaluating their supply chains in light of geopolitical tensions with China.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Chef Robotics in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How are U.S. robotics firms affected?
What are the implications of the FCC's bans?
Are there alternative suppliers available?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…