 Voanews
US Warns of Wrongful Detention Risks for Americans in China
Article Content

- •The U.S. State Department added a 'D' risk indicator for wrongful detention in China.
- •Americans may face arbitrary detention and exit bans for routine activities in China.
- •Two U.S. citizens are currently recognized as wrongfully detained by the State Department.
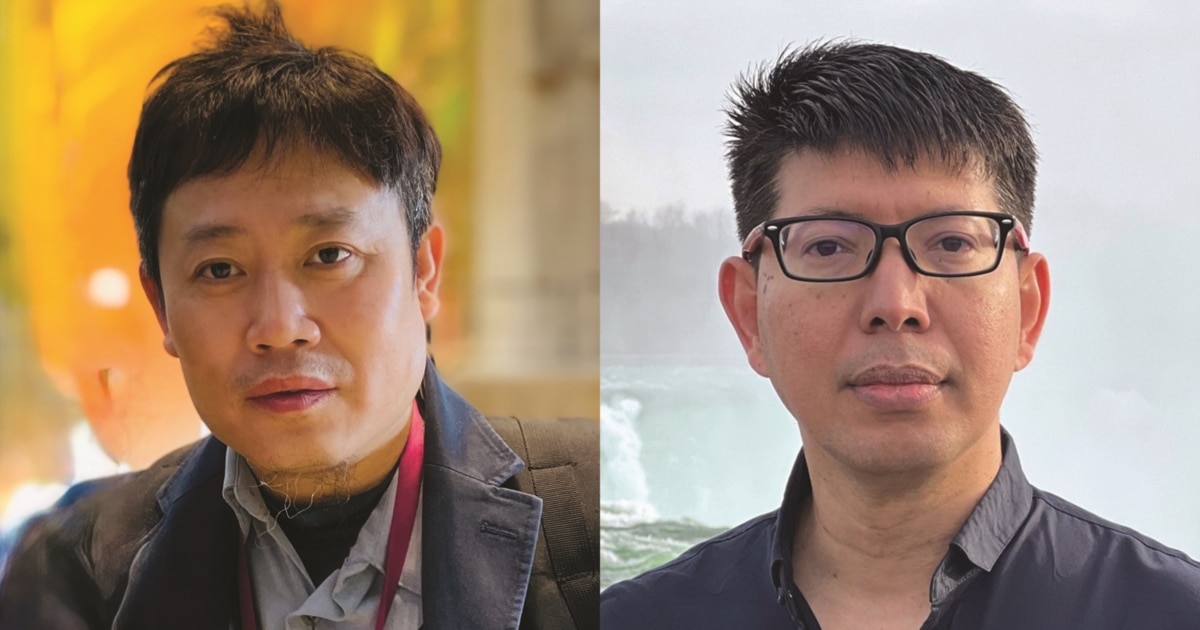
The U.S. State Department has updated its travel advisory for China, adding a 'D' risk indicator for wrongful detention. Americans face serious risks of arbitrary detention, exit bans, and invasive surveillance while in China. The advisory highlights that routine activities can be misclassified as espionage under China's broad security laws. Two U.S. citizens, Min Zin and Youlin Chen, have been designated as wrongfully detained, raising concerns about their treatment. The advisory emphasizes that Americans of Chinese descent and those involved in business disputes are particularly vulnerable. Despite a general safety rating of Level 2, the new classification warns of significant legal hazards for travelers. The advisory was issued following bipartisan congressional resolutions and ongoing diplomatic discussions regarding detained citizens.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Common questions
What does the 'D' risk indicator mean?
Who are the wrongfully detained Americans?
What should travelers do before going to China?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…