 Dvidshub
Utah National Guard Conducts Cyber Defense Exercise Amid Rising Threats
Article Content

- •Exercise Wolverine simulated a cyberattack on a water treatment facility in Utah.
- •The event involved rapid response training for cyber defense teams and local engineers.
- •The exercise underscored the importance of interagency collaboration in defending critical infrastructure.
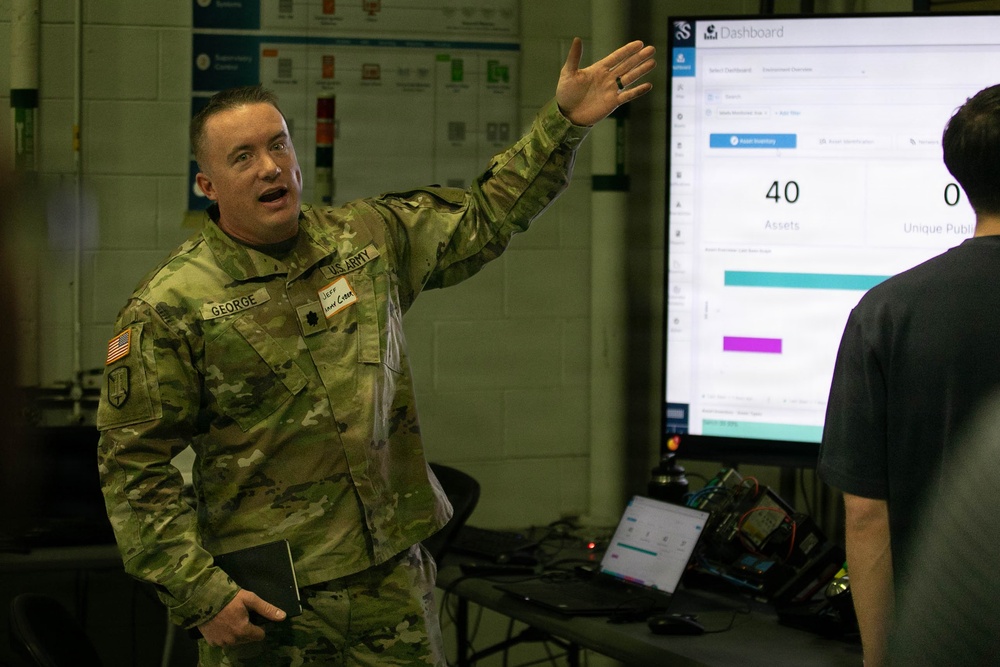
On April 30, 2026, the Utah National Guard conducted Exercise Wolverine, simulating a cyberattack on the Don A. Christiansen Regional Water Treatment Plant. The exercise aimed to test the rapid response capabilities of cyber defense teams and emergency units in the event of a real cyber threat disrupting critical infrastructure. Participants included Utah National Guard cyber specialists and local engineers, who practiced restoring water purification and distribution services under strict time constraints. The scenario was based on actual cyber threats targeting utilities globally. The exercise highlighted the importance of interagency collaboration and preparedness against evolving cyber threats. Officials noted that while the exercise was simulated, the tactics employed were reflective of real-world vulnerabilities faced by municipal services. The event emphasized the necessity for ongoing training and partnerships to safeguard essential services for the community.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…