 Crn
Veeam Launches DataAI Command Platform to Enhance AI Security Amid Rising Threats
Article Content

- •Veeam launched the DataAI Command Platform to unify AI security and data governance.
- •The platform addresses security challenges posed by autonomous AI agents in enterprises.
- •Veeam's acquisition of Securiti AI enhances its capabilities in data and AI trust.
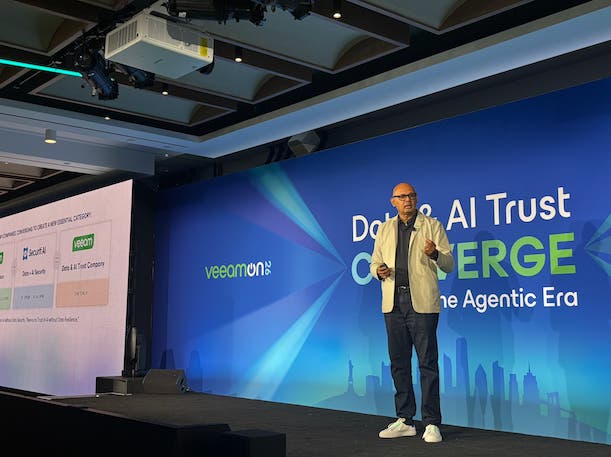
On May 13, 2026, Veeam announced the launch of its DataAI Command Platform at VeeamON 2026 in New York City. This platform integrates security features with AI capabilities, addressing critical security challenges in the Agentic Era, where autonomous AI agents outnumber human employees 82:1. The platform is built on Veeam's acquisition of Securiti AI, aiming to create a new category focused on data and AI trust. It combines data security posture management and AI security posture management with governance, compliance, and privacy features. Veeam's CEO Anand Eswaran highlighted the urgent need for a unified approach to secure data as AI becomes increasingly prevalent in enterprises. The platform is designed to protect over 550,000 customers globally, including 77% of the Global 2000, from emerging cyber threats associated with AI agents. The launch signifies a major step in addressing the security perimeter challenges posed by AI technologies.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…