 Openthemagazine
Vishnu Manchu Calls for Action on AI Deepfakes in Telugu Film Industry
Article Content

- •Vishnu Manchu calls for an industry-wide system to address AI deepfakes.
- •The controversy arose from a deepfake video involving Janhvi Kapoor and Jr NTR.
- •Manchu emphasizes the need for accountability in online criticism and campaigns.
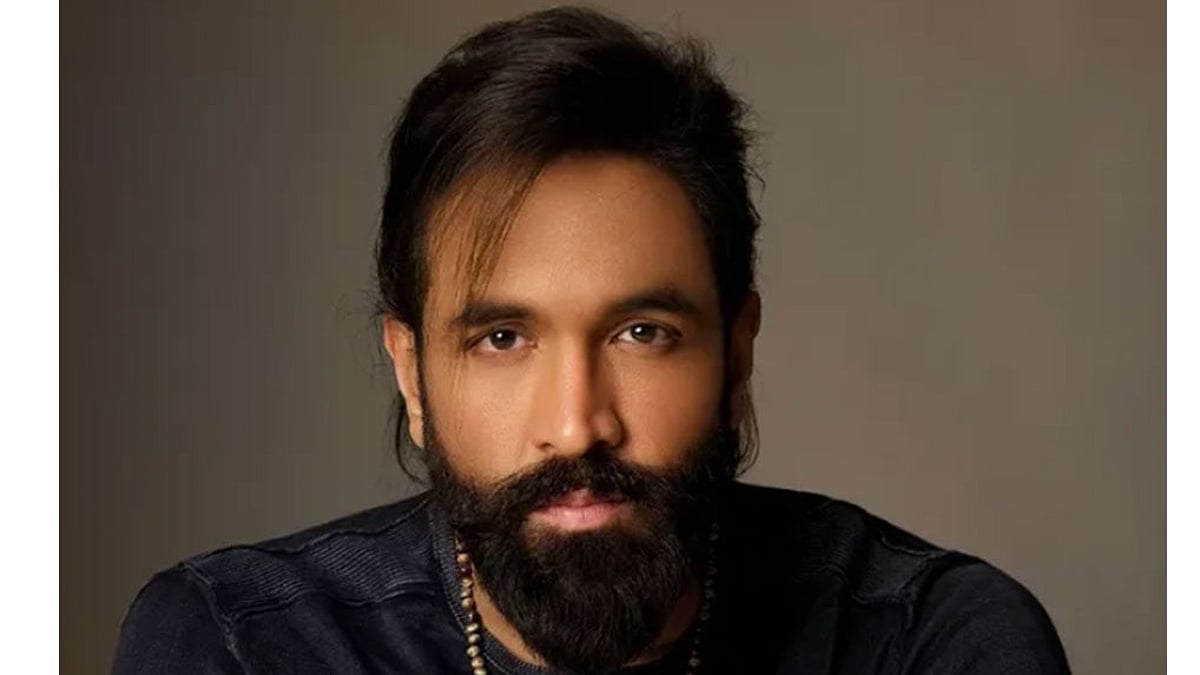
On October 5, 2026, Vishnu Manchu, president of the Movie Artists Association (MAA), urged the Telugu film industry to create a permanent system to combat AI deepfakes and online impersonation. This call to action follows a controversial deepfake video involving Janhvi Kapoor and Jr NTR, which sparked outrage. Manchu emphasized that while freedom of expression is vital, anonymity should not be used to defame or abuse individuals. He highlighted the need for accountability in online interactions, particularly regarding coordinated campaigns that aim to sabotage films before their release. Manchu also supported the idea of Aadhaar-linked accountability for online identities, stressing that technology is evolving too quickly for reactive measures to be sufficient. He noted that the MAA is compiling information on accounts involved in targeted abuse and malicious campaigns. The overall message was a plea for unity within the industry to protect its members and ensure fair competition.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What triggered Vishnu Manchu's statement?
What does Manchu propose for online accountability?
What is the MAA doing about targeted abuse?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…