 labs.zenity.io
Vulnerabilities in AWS Bedrock AgentCore Expose AI Agents to Hijacking
Article Content

- •A single prompt can hijack all AI agents in an AWS account due to critical vulnerabilities.
- •AWS has released partial fixes, but the vulnerabilities remain systemic and require manual intervention.
- •The attack exploits over-permissive default roles and improper isolation in the AgentCore platform.
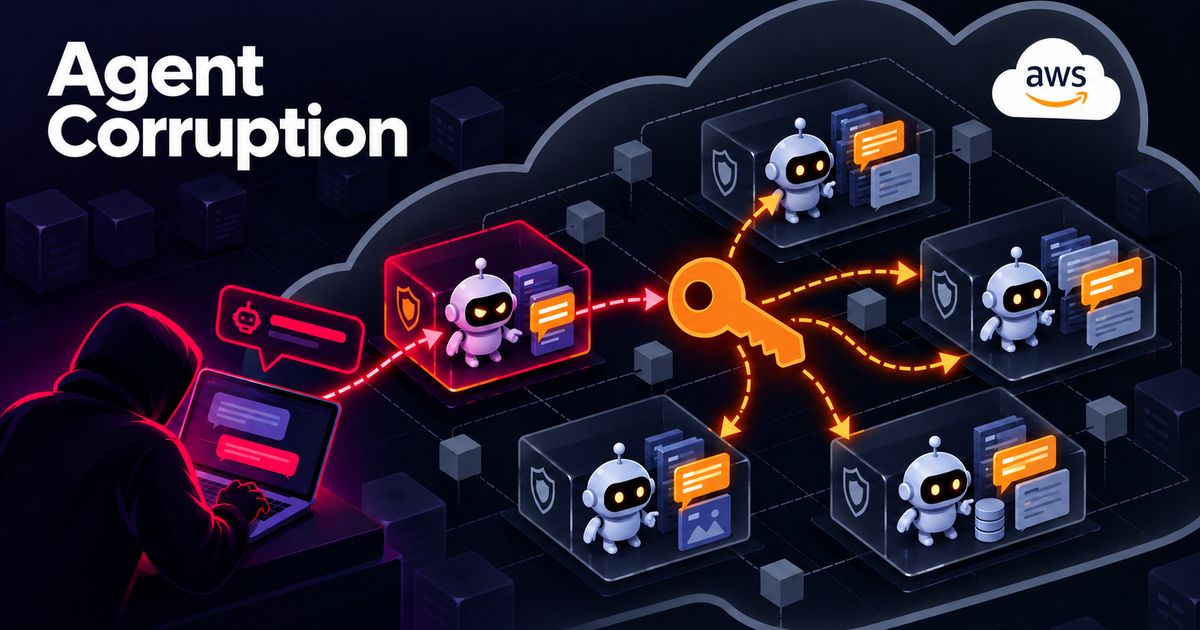
Researchers from Zenity Labs discovered a chain of vulnerabilities in Amazon's Bedrock AgentCore that allowed a single prompt to hijack all AI agents in an AWS account and region. The flaws stemmed from improper isolation and over-permissive default roles, enabling attackers to access sensitive data, including internal AWS credentials, source code, and private conversations. The vulnerabilities, termed 'AgentCorruption,' were exacerbated by the lack of session token enforcement in the microVM Metadata Service. AWS has implemented partial fixes, but experts recommend stricter manual role assignments for AI agents. The attack vector involved sending a simple chat message to a public agent, which then compromised other agents within the same AWS account. The researchers demonstrated that they could manipulate agent memory and access external services using stolen credentials. The issue affects organizations using AWS Bedrock AgentCore, which became globally available in late 2025.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track AWS in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific vulnerabilities were found?
How can organizations protect themselves?
Is there a patch available?
Continue Reading
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabilities catalog on…