 Theregister
Waymo Recalls 3,800 Robotaxis Due to Flooding Software Glitch
Article Content

- •Waymo recalls 3,791 robotaxis due to a software flaw allowing high-speed entry into floodwaters.
- •The recall follows an incident on April 20, 2026, where a vehicle drove into a flooded lane without injuries.
- •Waymo has temporarily suspended services in San Antonio and is working on software updates for safety.
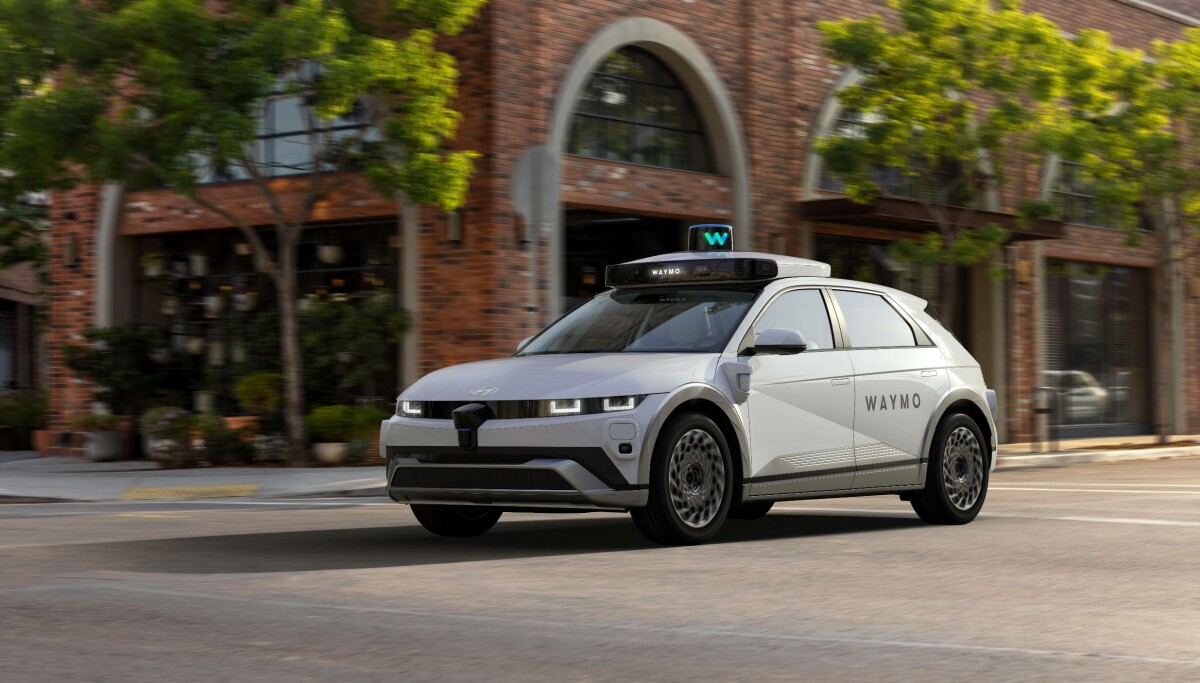
Waymo is recalling 3,791 autonomous vehicles in the U.S. following a software issue that allowed a robotaxi to drive into a flooded lane in San Antonio on April 20, 2026. The software flaw may permit vehicles to maintain high speeds when entering standing water, increasing crash risks. Although there were no injuries reported from the incident, Waymo has temporarily suspended its services in San Antonio. The company is working on a permanent solution to enhance safety during extreme weather conditions. This recall highlights ongoing concerns about the performance of autonomous vehicles in complex environments. Waymo operates over 3,000 robotaxis across approximately 10 U.S. metropolitan areas, providing over 500,000 rides weekly. The National Highway Traffic Safety Administration (NHTSA) has been informed of the recall, and Waymo is implementing additional software safeguards.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…