 Nationalsecuritynews
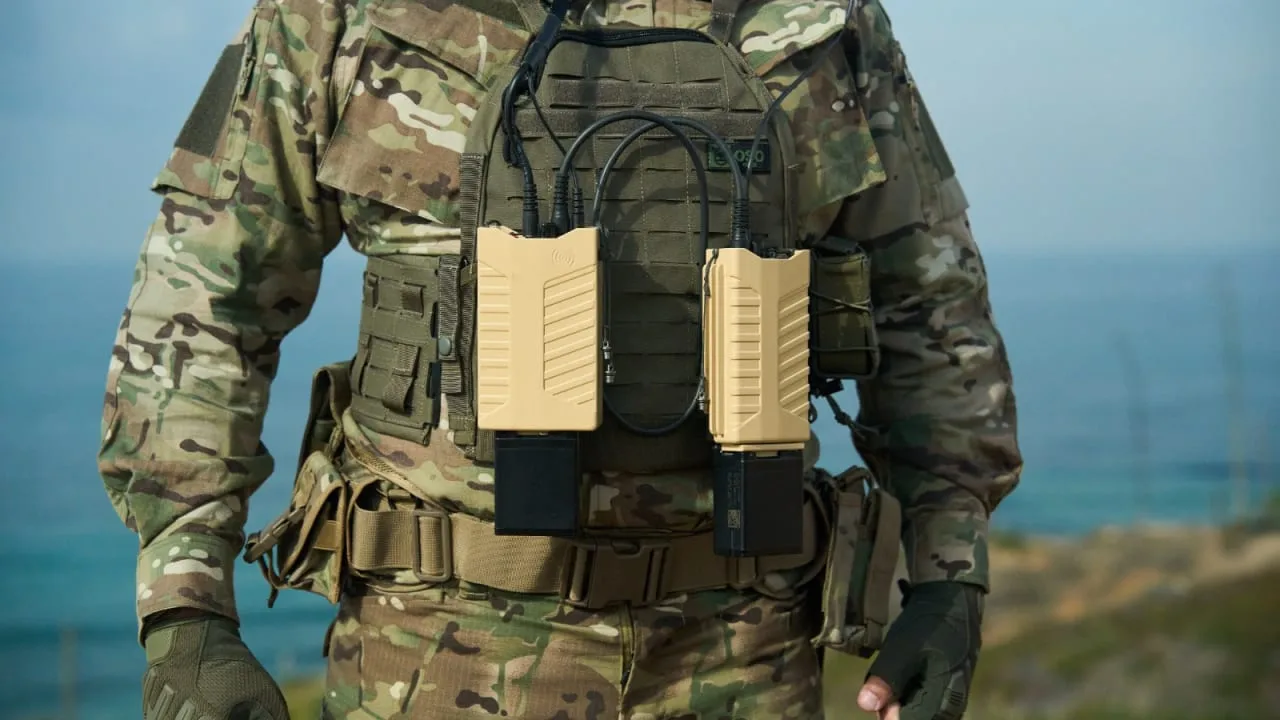
Wearable Counter-Drone Technology Deployed by US, Ukraine, and Israel
Article Content

- •Wearable counter-drone systems are now operational with US, Ukrainian, and Israeli forces.
- •Autonomous Guard's technology can detect drones up to two kilometers and jam them at three kilometers.
- •MyDefence has launched Wingman Edge, a lightweight drone detection system for individual soldiers.
Ukrainian and Israeli forces are deploying wearable counter-drone technology from Autonomous Guard, which is also being tested by the US Army. This technology includes RF detection and jamming capabilities, allowing soldiers to detect hostile drones up to two kilometers away and jam them from three kilometers. The system provides directional alerts, enabling troops to take cover or reposition. The US Army has trialed this equipment during exercises in Europe, reflecting the growing need for individual soldier protection against drone threats. The technology has been supplied to various military units, including those under US European Command and Ukraine's Armed Forces. The increasing use of drones in warfare has prompted militaries to seek portable counter-drone solutions, with the US military emphasizing the need to adapt to these evolving threats. Additionally, MyDefence has introduced a new drone detection system called Wingman Edge, which utilizes AI for real-time analysis of the electromagnetic spectrum.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track MyDefence in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the range of the counter-drone technology?
Who is using this technology?
What is the significance of the Wingman Edge system?
Continue Reading
 Critical Citrix NetScaler Vulnerabilities Actively Exploited in Finland The National Cyber Security Centre Finland (NCSC-FI) issued an alert regarding critical vulnerabilities in Citrix NetScaler ADC and Gateway products, specifically CVE-2026-88771 and CVE-2026-88772, which are being actively exploited in Finland. These vulnerabilities allow attackers to execute remote code without…
 Critical Authentication Bypass in Rejetto HFS Exploited Within 24 Hours Anthropic's Mythos model identified a critical authentication bypass in Rejetto HTTP File Server (HFS), tracked as CVE-2026-61500, allowing remote code execution. Discovered by Horizon3 researcher Zach Hanley, the flaw was revealed on September 27, 2026, and exploitation began within 24 hours, with attacks traced to…