 Techspot
Xbox One Hacked: Voltage Glitch Exploit Breaks Years of Security
Article Content

- •Markus Gaasedelen demonstrated the 'Bliss' voltage glitch exploit at RE//verse 2026.
- •The exploit allows full control over the original Xbox One, deemed unpatchable.
- •Only the original Xbox One is affected; newer models remain secure.
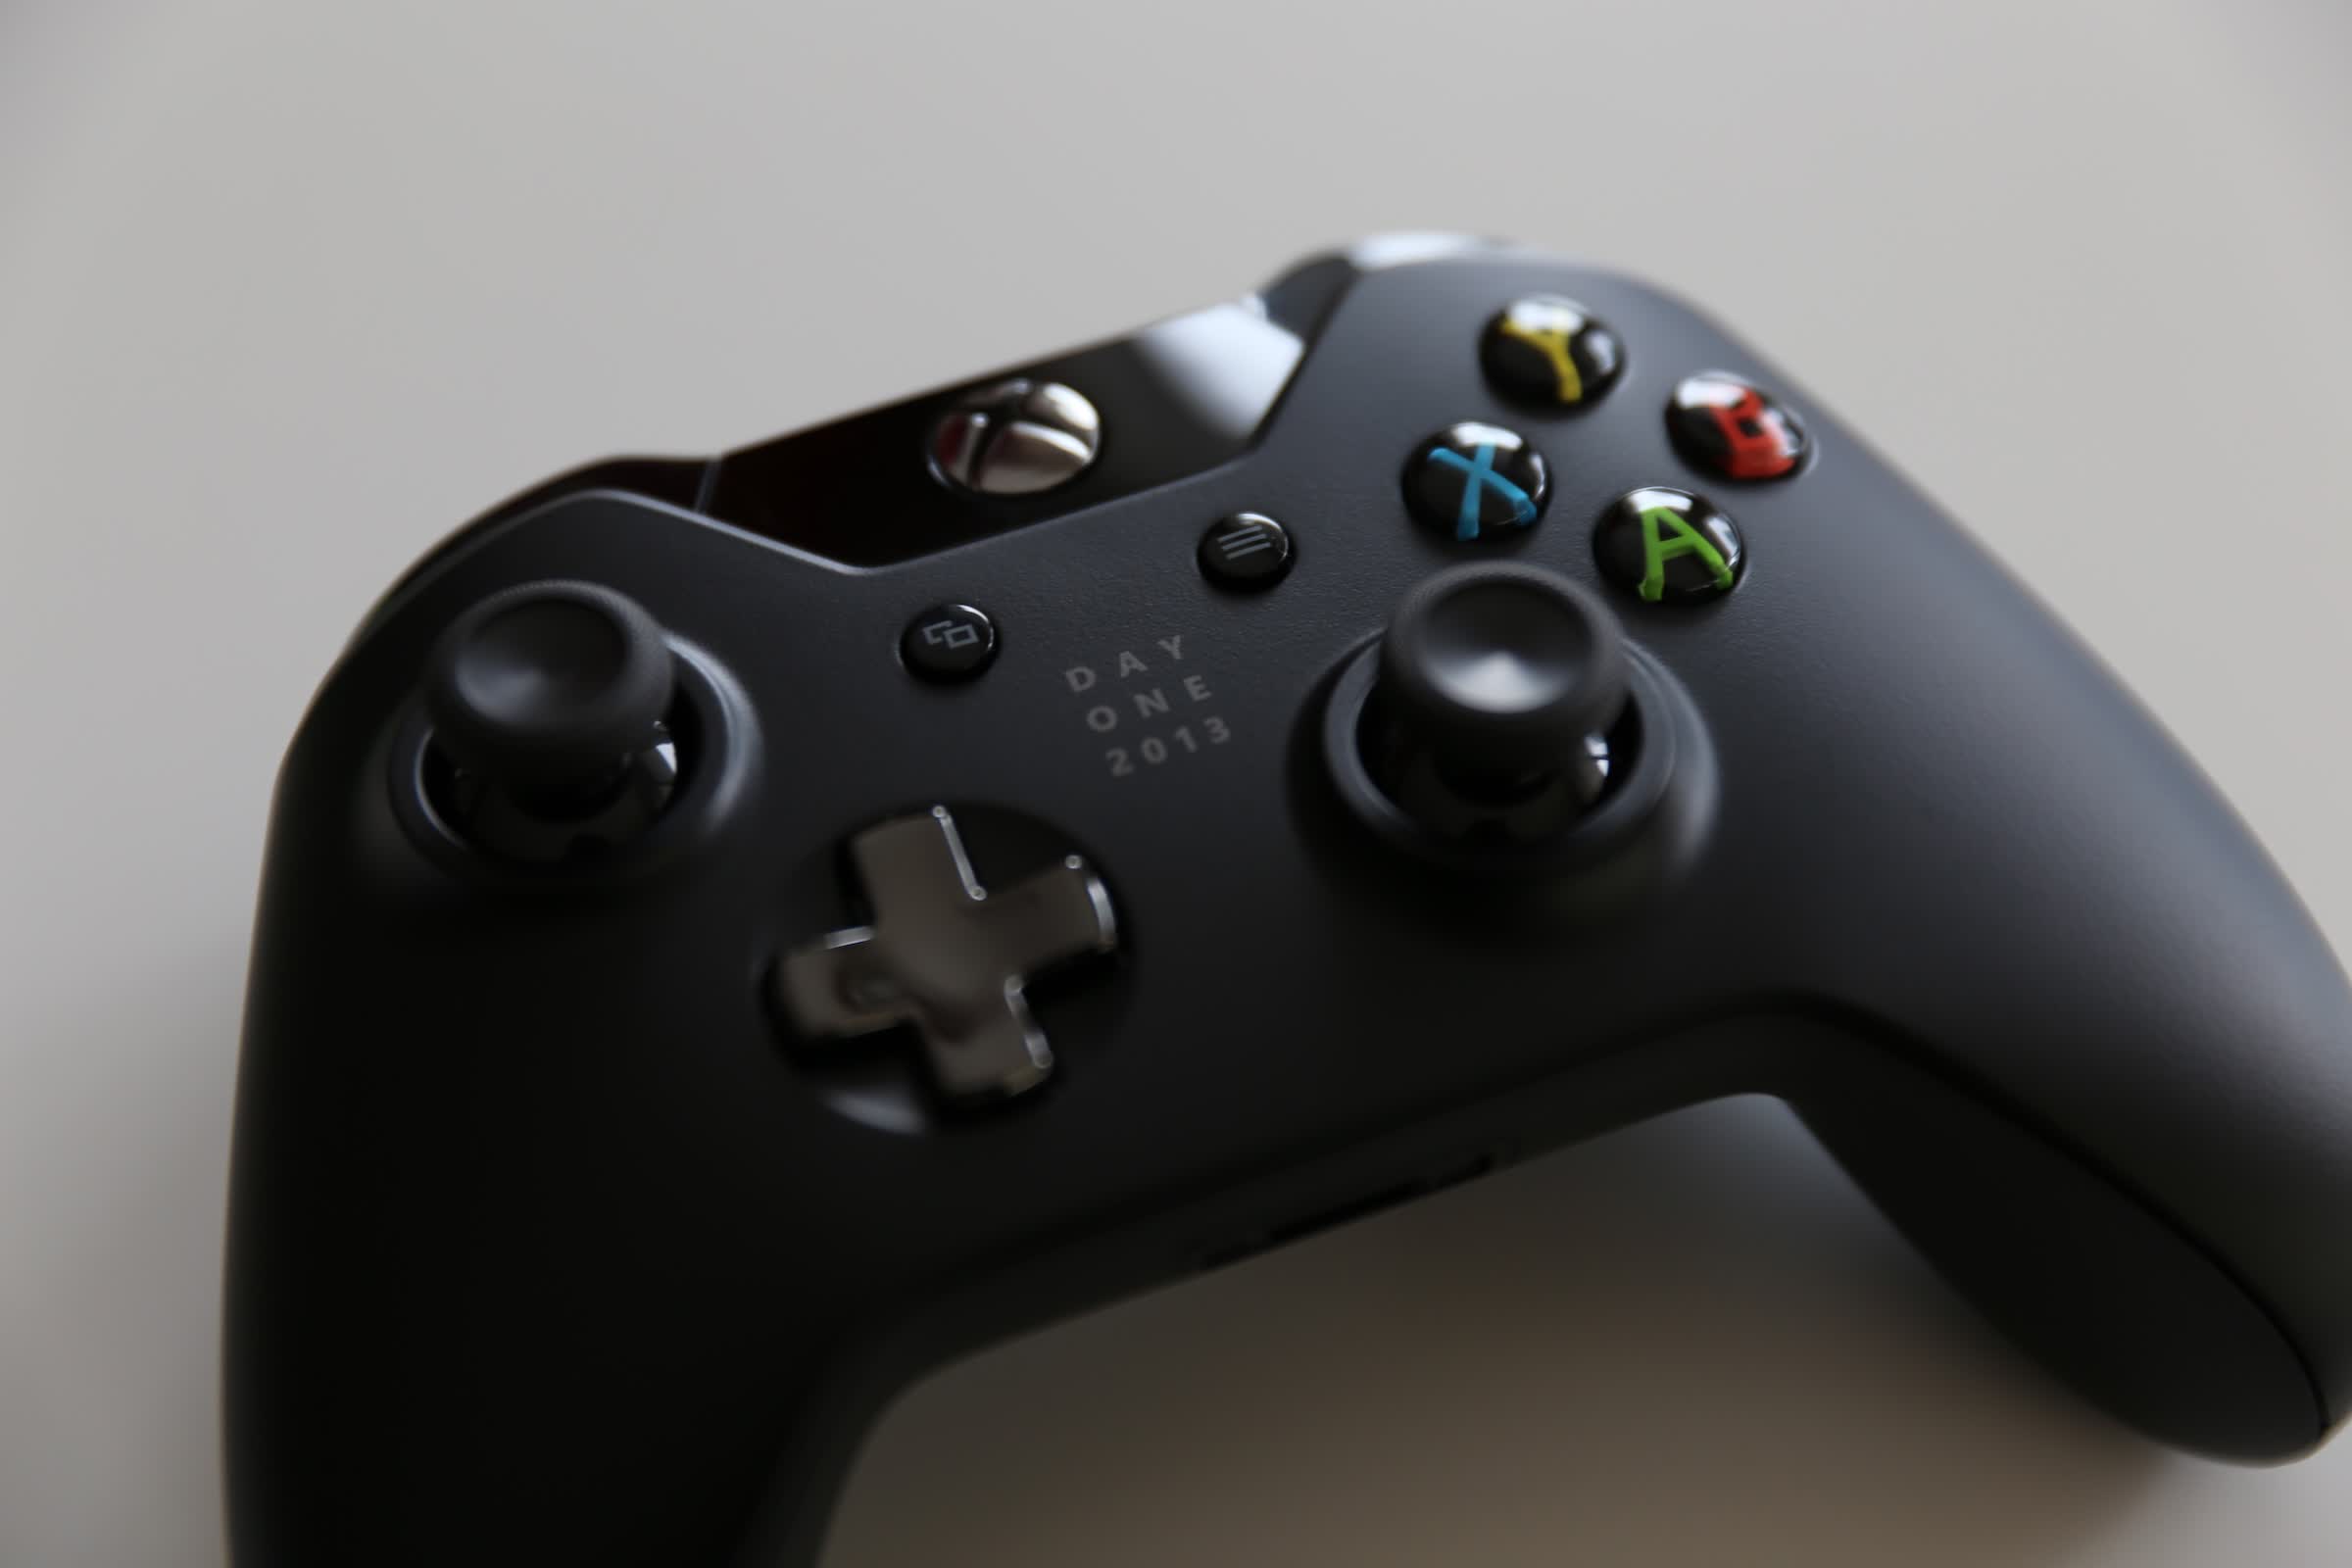
At the RE//verse 2026 conference, security researcher Markus 'Doom' Gaasedelen demonstrated a hardware exploit named 'Bliss' that successfully compromised the Xbox One console, which had been considered unhackable since its release in 2013. The exploit utilizes a voltage glitching technique that manipulates the power supply during the boot process, allowing unauthorized code execution and access to the system's security processor. This method specifically targets the original Xbox One model, leaving subsequent models like the Xbox One S and Xbox Series unaffected. Gaasedelen's approach marks a significant breakthrough in console security, as it undermines the hardware-level defenses that Microsoft had established. The hack is deemed unpatchable, providing attackers with full control over the console, including the ability to run unsigned code and access encrypted data. Gaasedelen has a history of research in Xbox security, emphasizing that his work aims to preserve console functionality rather than promote piracy.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…