 Securityaffairs.Co
Takedown of XSS.is Forum Disrupts Ransomware Supply Chain
Article Content

- •XSS.is, a major ransomware forum, was shut down by law enforcement in July 2025.
- •The forum facilitated escrow services for cybercriminal transactions, impacting the ransomware economy.
- •Despite the takedown, the ransomware market remains active and resilient.
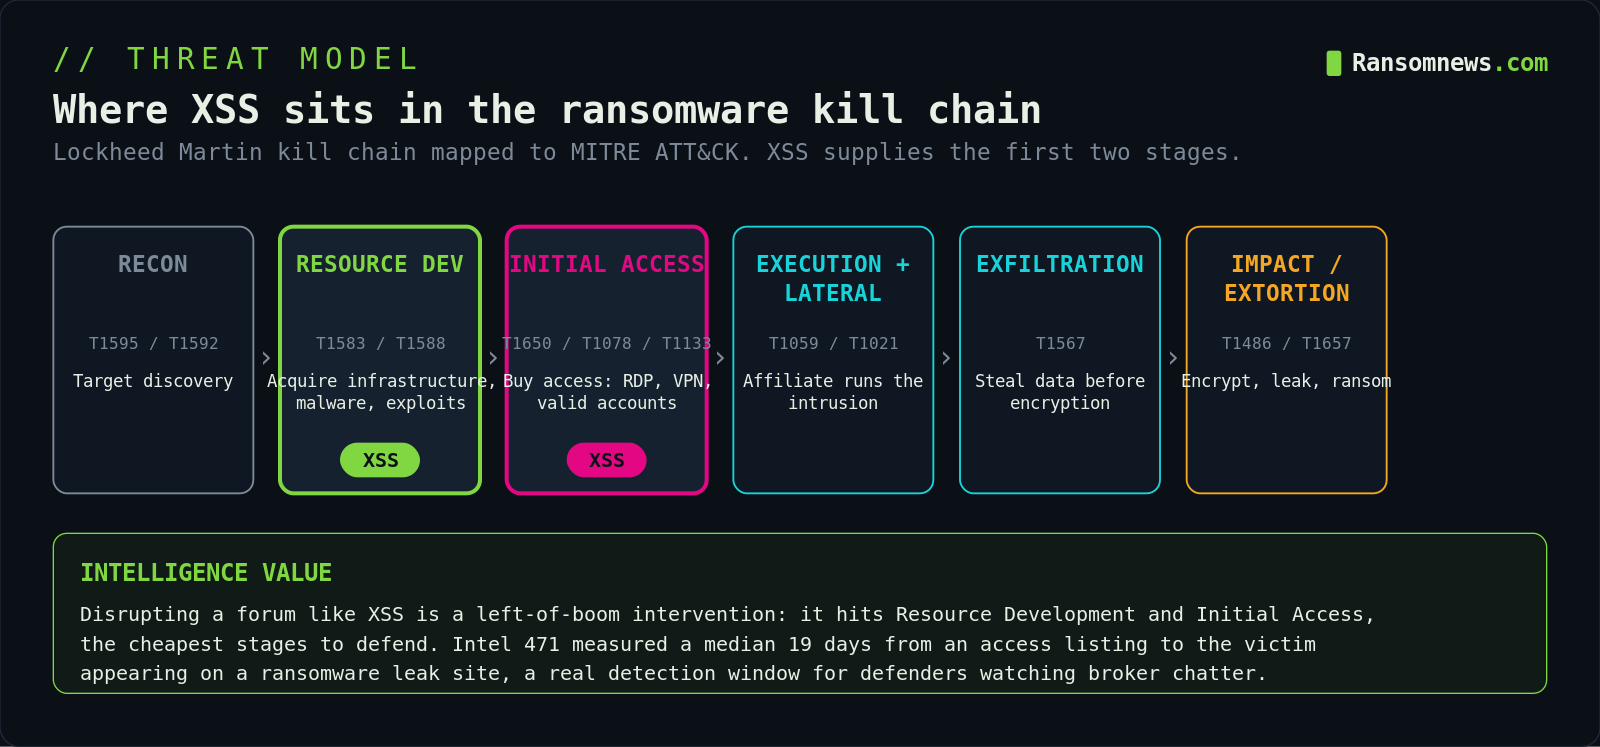
On July 22, 2025, French and Ukrainian police arrested the alleged admin of XSS.is, a prominent Russian-language cybercrime forum, effectively shutting it down. This forum was crucial for ransomware operations, facilitating transactions and escrow services within the underground economy. The arrest of the 38-year-old man in Kyiv marks a significant blow to cybercriminal activities, although the broader ransomware market remains active. The XSS.is forum had been a key player in the distribution of ransomware tools and services, impacting numerous organizations globally. Despite this takedown, experts warn that the ransomware market continues to thrive, indicating a resilient underground ecosystem. The operation was coordinated by Europol, highlighting international collaboration in combating cybercrime. The full scope of the impact on ransomware operations is still being assessed as new forums may emerge to fill the void left by XSS.is.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track DaMaGeLaB in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…