 Bbc
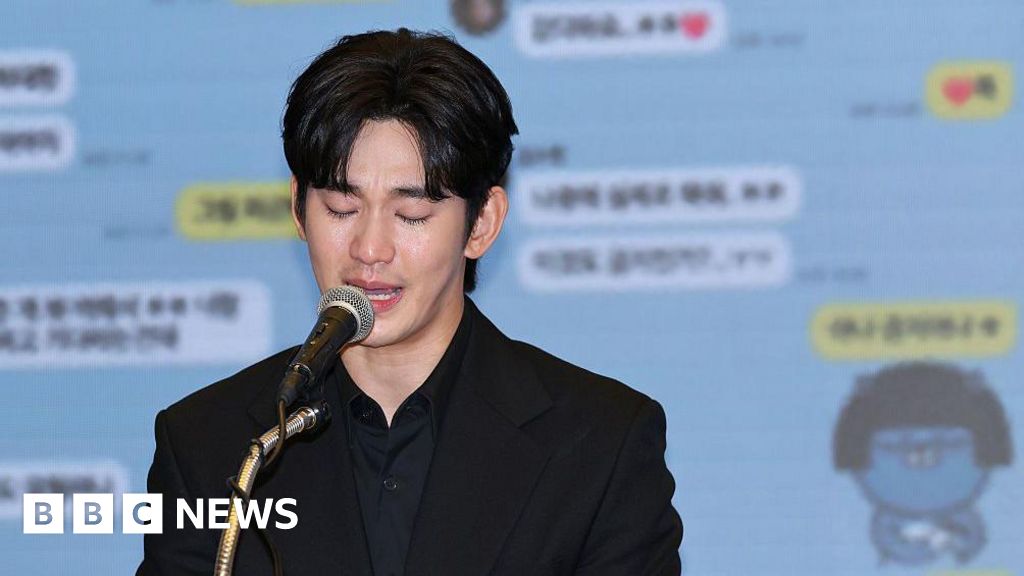
YouTuber Arrest Warrant Issued for Faking Evidence Against Korean Actor
Article Content

- •YouTuber Kim Se Eui faces arrest for fabricating evidence against actor Kim Soo Hyun.
- •Manipulated text messages and AI-generated audio were used to falsely claim a minor relationship.
- •The scandal has severely impacted Kim Soo Hyun's career and mental health.
South Korean police are pursuing an arrest warrant for YouTuber Kim Se Eui, accused of fabricating evidence that defamed actor Kim Soo Hyun. The allegations stem from claims that Kim Soo Hyun dated actress Kim Sae Ron when she was a minor, which surfaced after her tragic death in February 2025. Investigators found that manipulated text message screenshots and an AI-generated audio file were used to support these false claims. The police concluded that the YouTuber knowingly spread misinformation for financial gain, severely damaging Kim Soo Hyun's career and mental health. The investigation revealed that the audio clip was created using advanced generative AI technology, and the text messages were altered to mislead the public. Kim Soo Hyun has consistently denied the allegations and is currently undergoing psychiatric treatment. The scandal has highlighted the severe impact of online defamation in South Korea's celebrity culture.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…