 Odt.Co.Nz
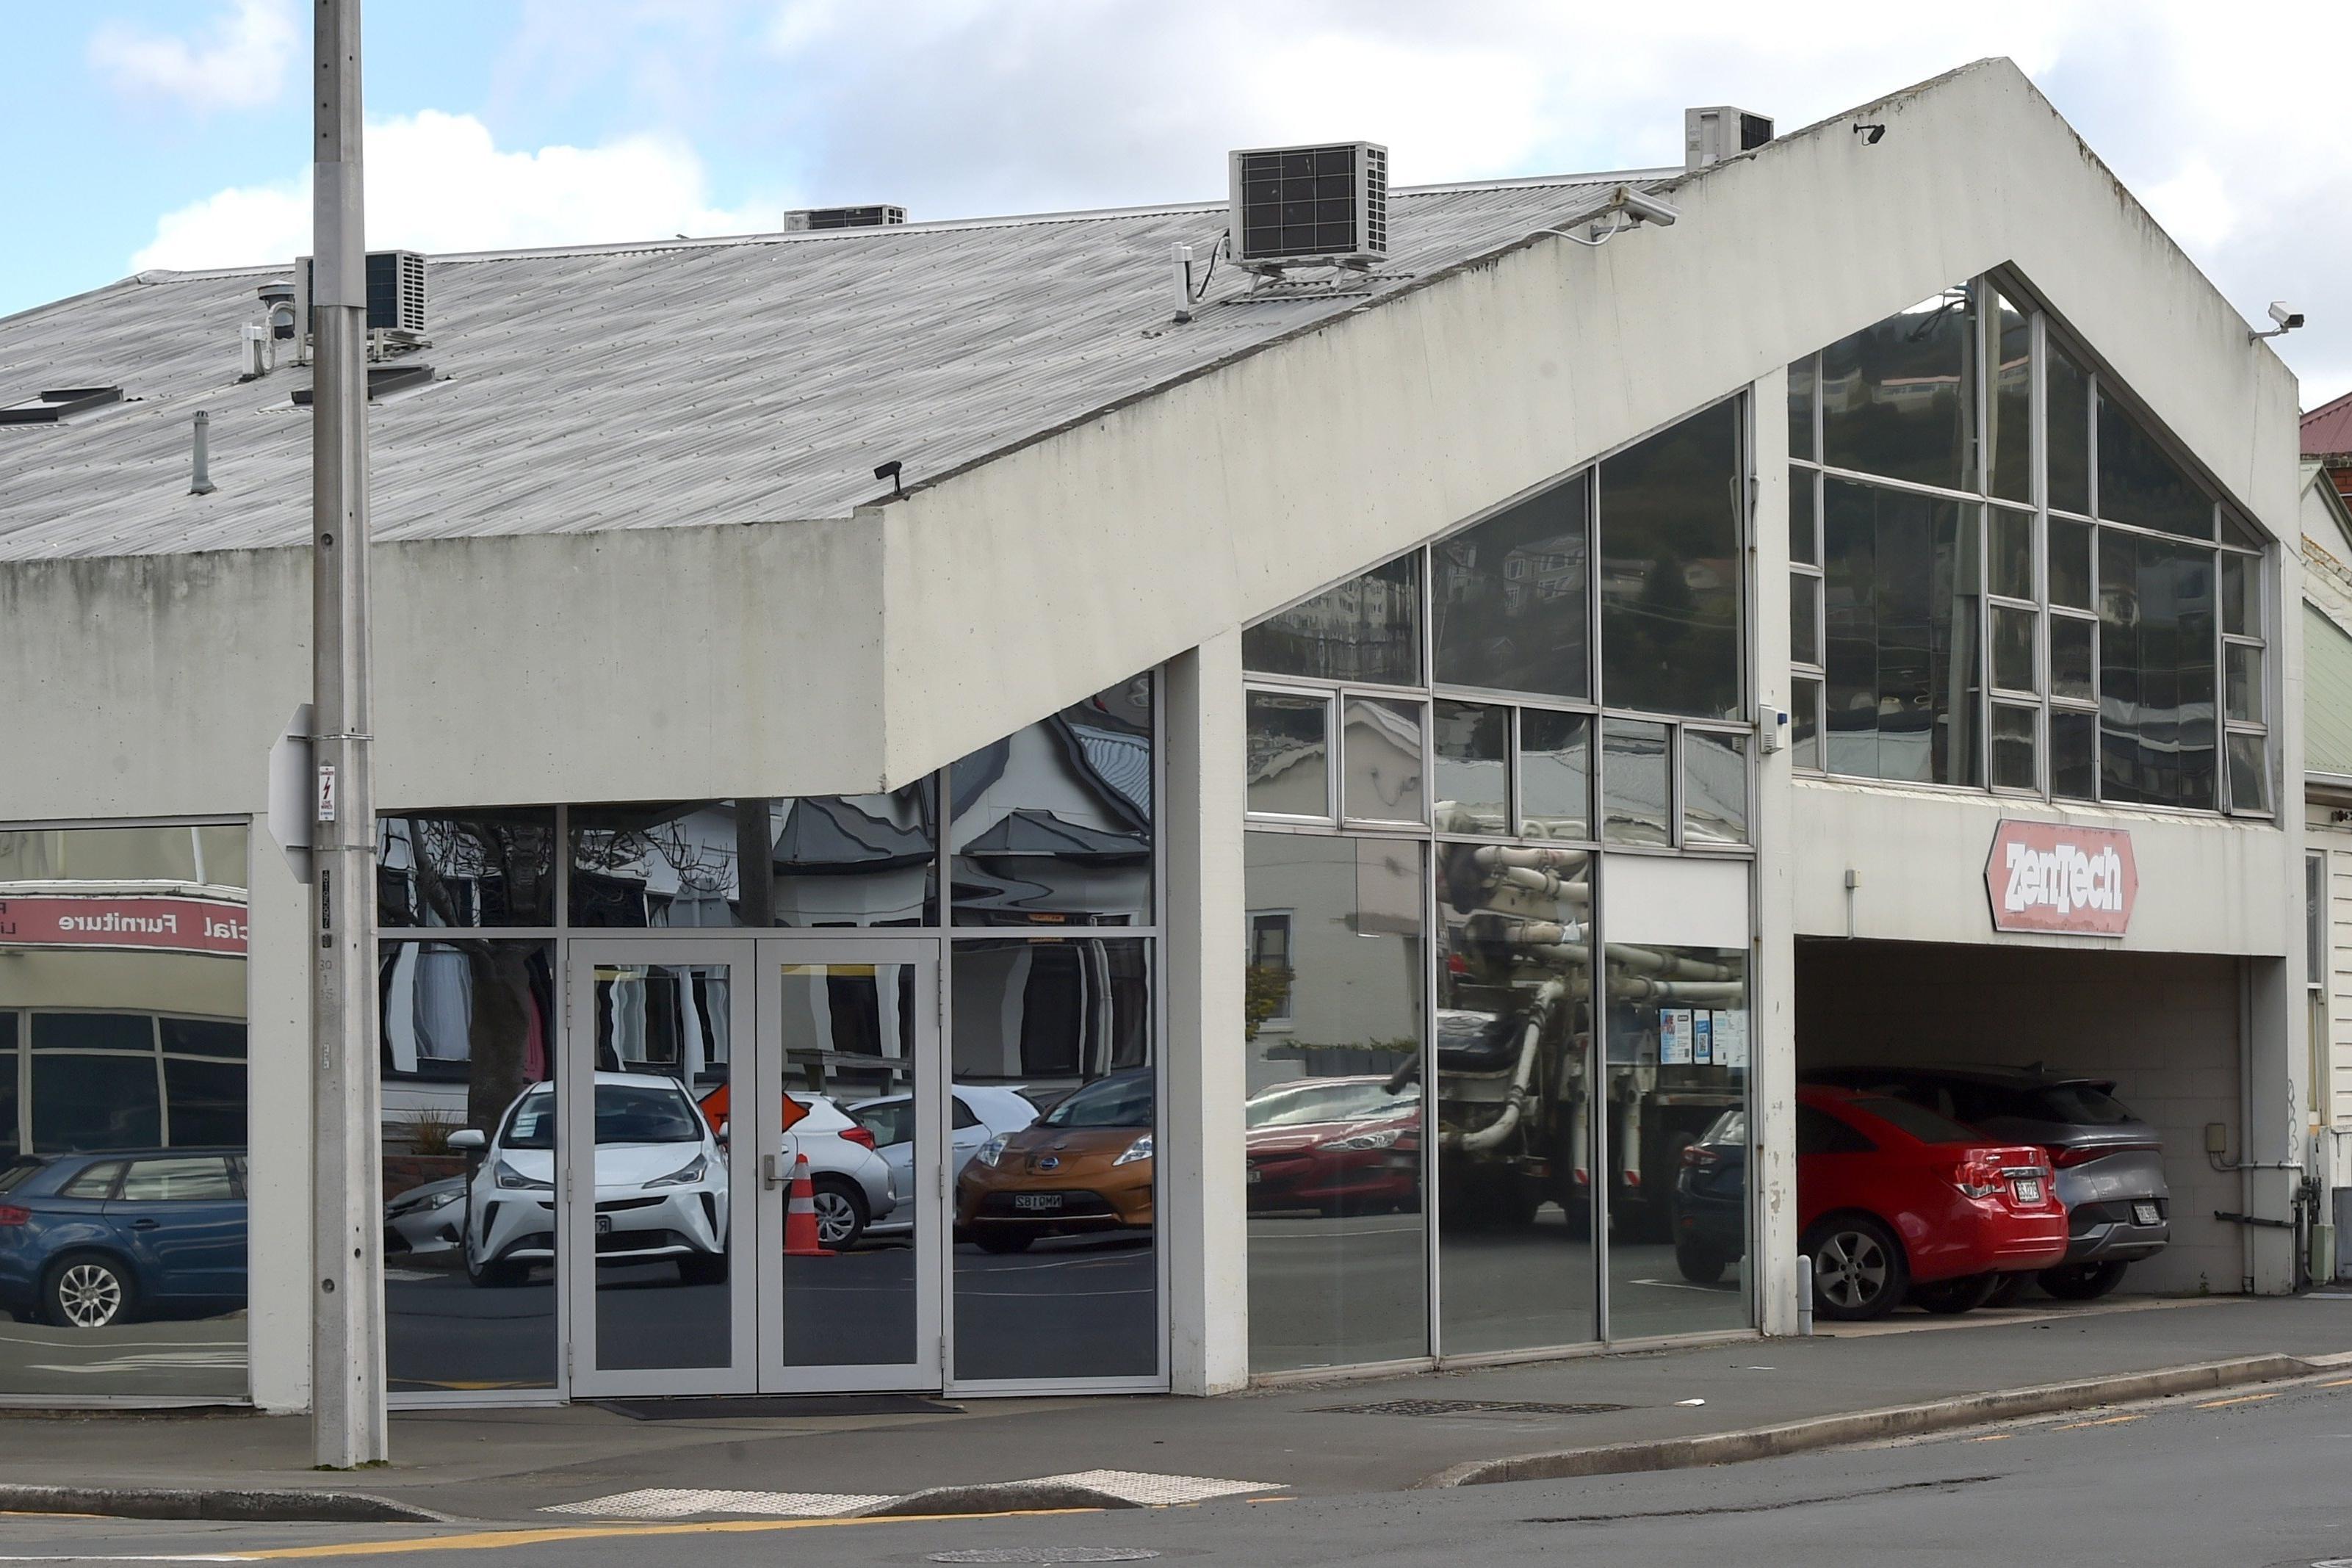
ZenTech Ransomware Attack Disrupts Coronial Investigations in NZ
Article Content

- •ZenTech's ransomware attack has stalled coronial investigations in New Zealand.
- •The ZaWoo group claimed responsibility and leaked sensitive data on the dark web.
- •Families are facing significant delays in receiving coronial findings due to the breach.
A ransomware attack on ZenTech, a Dunedin laboratory company, has delayed coronial investigations in New Zealand. The Ministry of Justice confirmed that sensitive coronial information was compromised, affecting cases primarily from 2016 to 2022. Families are experiencing significant delays, with one family waiting nine months for findings related to their loved one's death. The ZaWoo group claimed responsibility for the attack, demanding a bitcoin ransom and releasing personal data on the dark web. The Ministry is investigating how ZenTech came to hold this sensitive data, as there was no contract between ZenTech and the Ministry. ZenTech stated that it took immediate steps to secure its systems following the incident. The High Court has issued an injunction to prevent the misuse of the compromised data. This incident follows a similar ransomware attack in December 2022 that affected other coronial files in New Zealand.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track ZaWoo Group and Zenith Technology in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data was compromised?
How are families affected?
What actions is ZenTech taking?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…