Summary
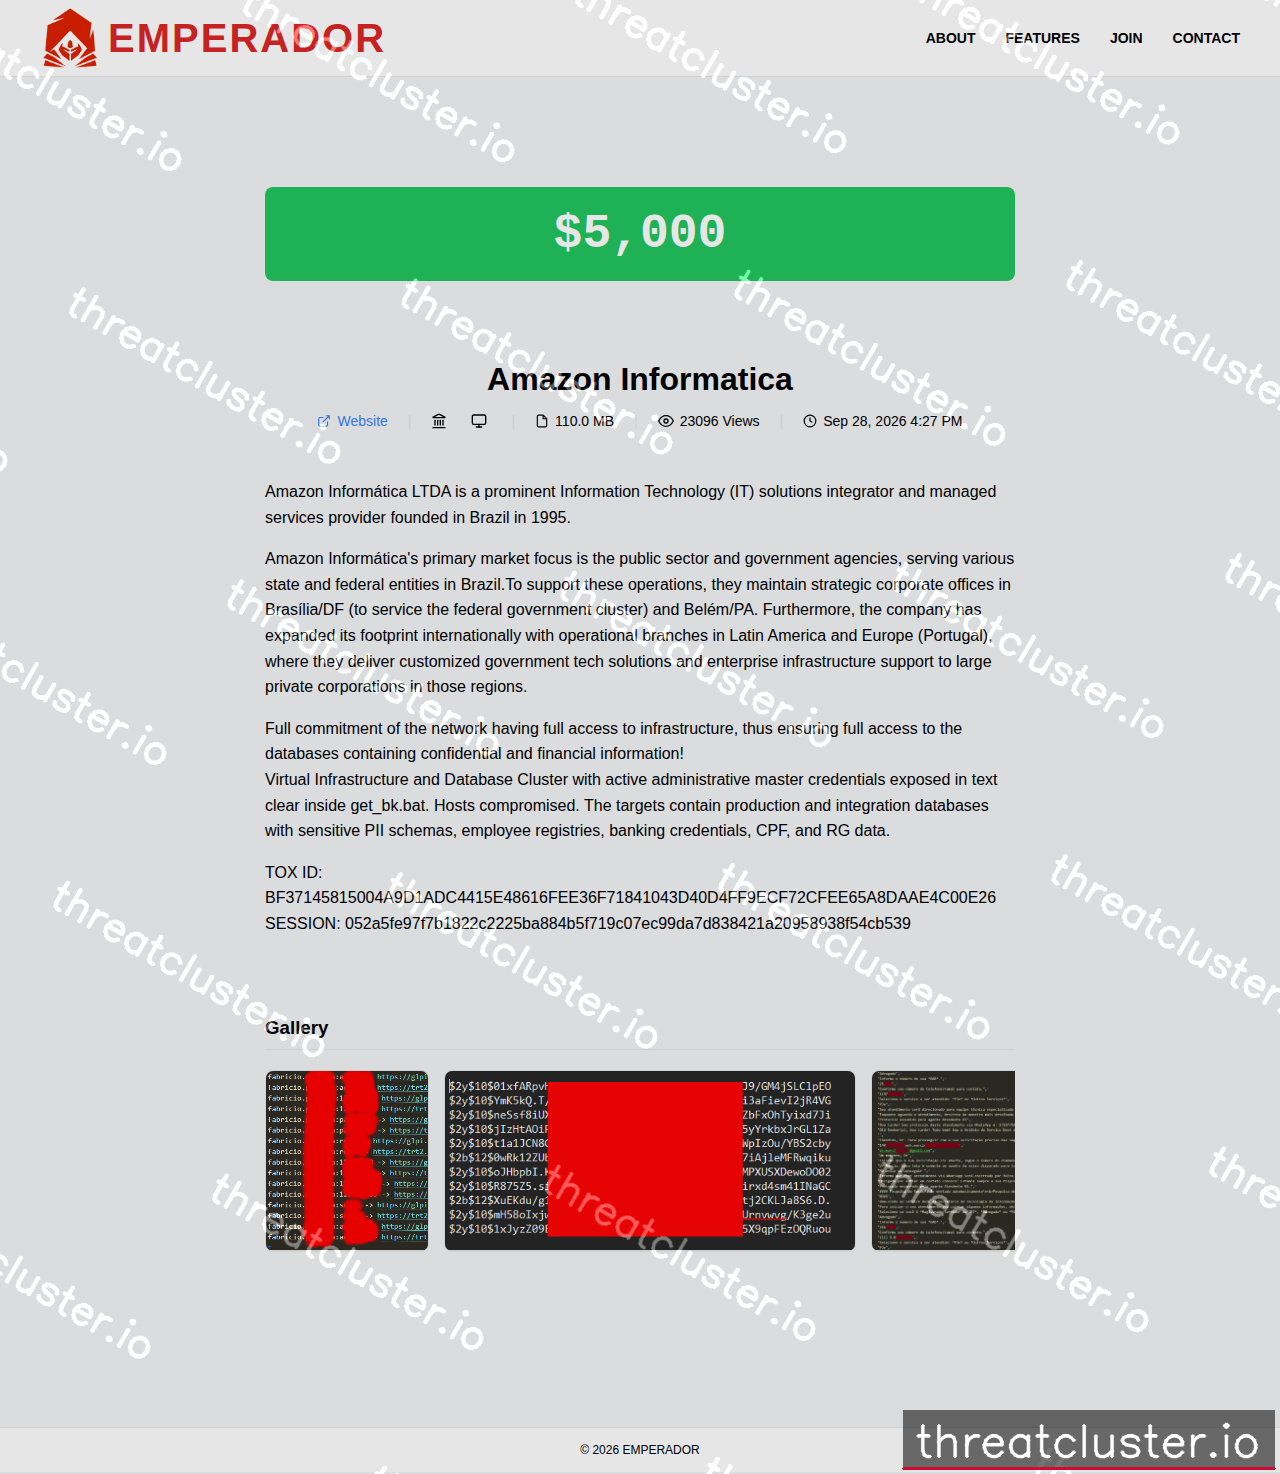
Written by ThreatClusterfrom site fields, file listing, victim profile, leak post, screenshot, ransom noteThe group emperador claims to have exfiltrated 110.0 MB of data from Amazon Informática LTDA, a Brazil-based IT solutions integrator and MSP. They state the data includes sensitive PII schemas, employee registries, banking credentials, and CPF and RG data. The leak post is published on the group’s site.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
Victim profile
- Founded
- 1995
- Domains
- https://amazoninformatica.com.br/
What was taken
Amazon Informática LTDA, a Brazilian IT solutions integrator and managed services provider, with a primary focus on the public sector and government agencies; corporate offices in Brasília/DF and Belém/PA, with international branches in Latin America and Portugal; claims full access to the network and databases containing confidential and financial information; virtual infrastructure and database cluster with active administrative master credentials exposed in text clear inside get_bk.bat; hosts compromised; targets contain production and integration databases with sensitive PII schemas, employee registries, banking credentials, CPF, and RG data.
Ransom note
Published by the group on their leak site, reproduced verbatim.
Full commitment of the network having full access to infrastructure, thus ensuring full access to the databases containing confidential and financial information!
Also stated on the leak page
Fields this group publishes that do not map to a standard column. Labels are the site's own.
- TOX ID
- BF37145815004A9D1ADC4415E48616FEE36F71841043D40D4FF9ECF72CFEE65A8DAAE4C00E26
- TOX_ID
- 3D6EF83C3C4517FE42B212A934D4B08579A5F20522828C4E4818EA117F53063377C4D769640B
- Gallery
- Proof Image
- SESSION
- 052a5fe97f7b1822c2225ba884b5f719c07ec99da7d838421a20958938f54cb539
Leak-site images (4)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.