Data size
30.46 GB
Files
5,140
Posted
Dec 1, 2025
Country
BE
Industry
Telecommunication
Summary
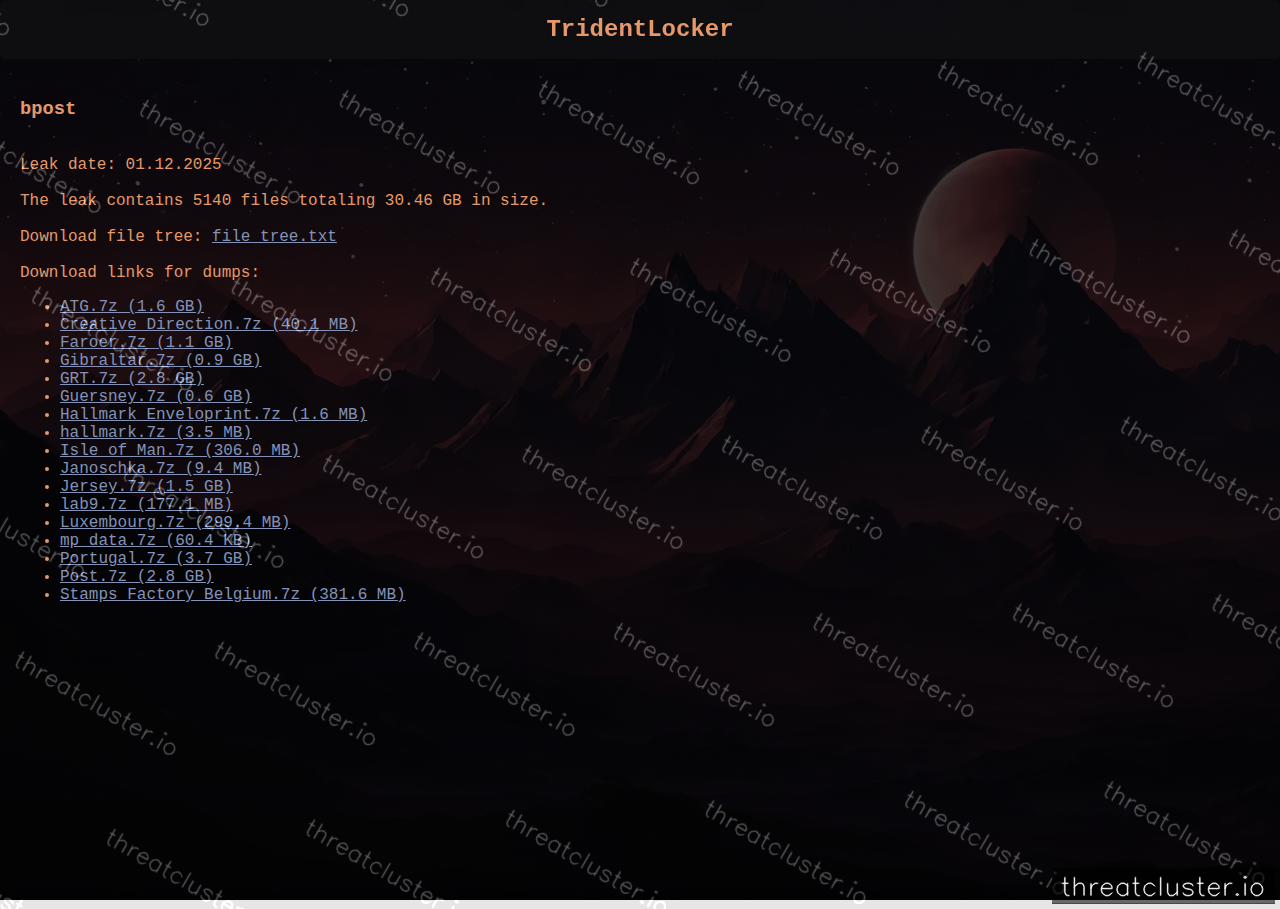
Written by ThreatClusterfrom file listing, leak post, screenshotTridentLocker states they exfiltrated 30.46 GB from the Belgian postal operator bpost, comprising 5,140 files. The leak post provides sample filenames including ATG.7z, Creative Direction.7z, Faroer.7z, Gibraltar.7z, and others, and indicates the data are in 7z archives. The leak post is published, with the group claiming the data originate from bpost.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
What was taken
bpost
File types seen
7z × 17
Sample files (17)
ATG.7z
Creative Direction.7z
Faroer.7z
Gibraltar.7z
GRT.7z
Guersney.7z
Hallmark Enveloprint.7z
hallmark.7z
Isle of Man.7z
Janoschka.7z
Jersey.7z
lab9.7z
Luxembourg.7z
mp_data.7z
Portugal.7z
Post.7z
Stamps Factory Belgium.7z
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.
ThreatCluster capture