Summary
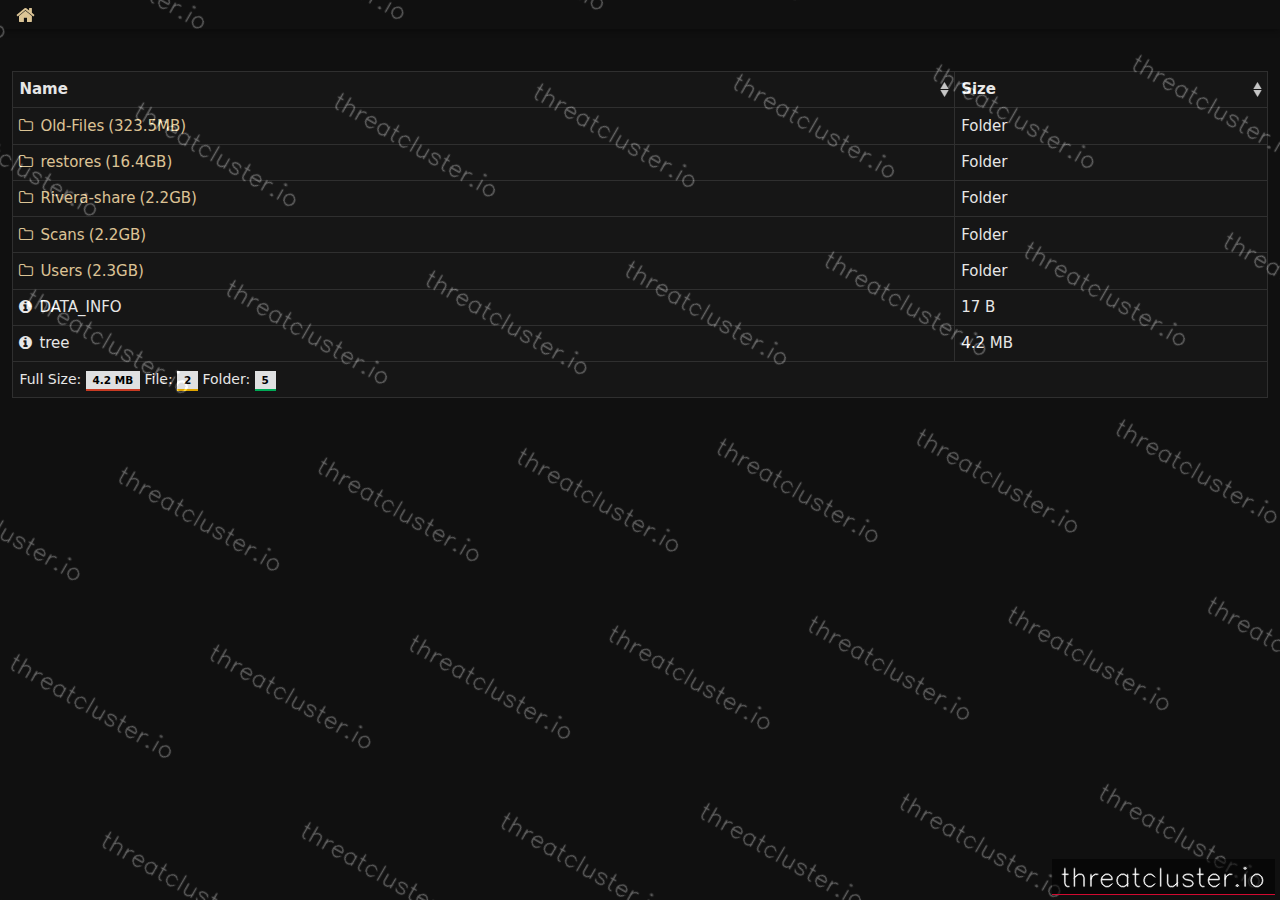
Written by ThreatClusterfrom victim profile, leak post, screenshotInterlock states that Riviera Healthcare Center’s data—about 30 GB in size—has been exposed. They claim the leaked data include patient health information (PHI) such as names, diagnoses, medical histories, and treatment details, as well as employee/HR data and payment records. The leak post identifies Riviera Healthcare Center as the victim and references the domain rivierahealthcare.com; the post is listed on the group’s leak site. The group states the incident violates HIPAA and the California CMIA (potentially CCPA/CPRA) and warns of mandatory breach notification, fines, civil actions, and reputational damage.
Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.
What was taken
Riviera Healthcare Center is a for-profit skilled nursing facility in operation for over 50 years. It provides 24-hour nursing and rehabilitation services. Due to negligence and poor security practices, confidential data was exposed, including patient protected health information (PHI)names, diagnoses, medical histories, fall/fracture and treatment information, payment records, and employee/HR data. This breach violates HIPAA and the California CMIA (and potentially the CCPA/CPRA) and will result in mandatory breach notification, federal and state fines, civil lawsuits, corrective action plans, and significant reputational and financial damage.
Leak-site images (1)
Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.