Skip to content
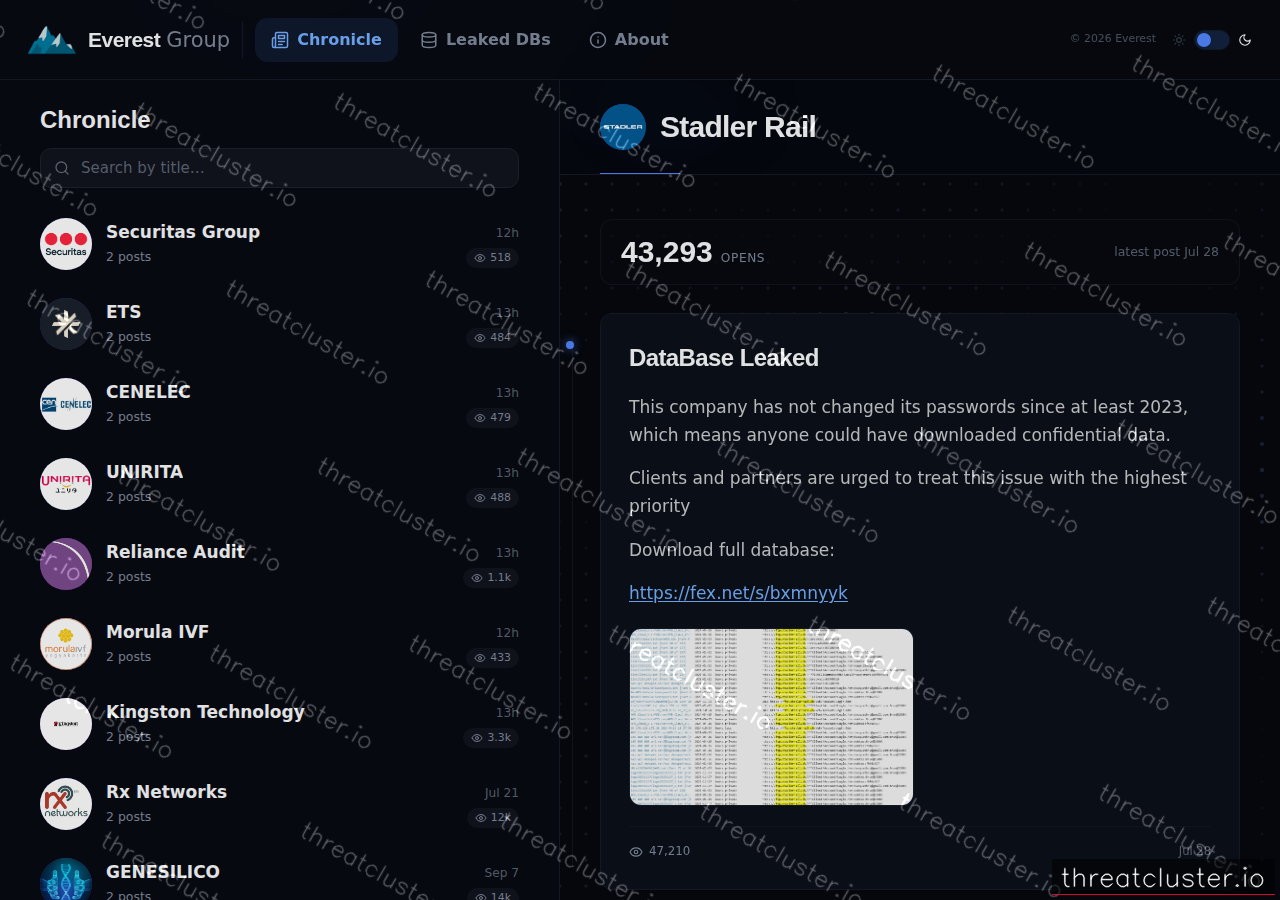
Leak-site post naming Stadler Rail, captured by ThreatCluster

Stadler Rail

everest

Ransomware leak-site victim intelligence · EN

Data size
201 GB
Files
271,868
Views
58,000
Posted
Jul 28, 2026
Country
CH
Industry
Railway

Summary

Written by ThreatClusterfrom file listing, victim profile, leak post, screenshot, our reporting

Everest ransomware group claims Stadler Rail’s database was leaked, exposing about 201 GB of data and roughly 271,868 files. The leaked material is described as including passenger-information system materials, train-system components, and related onboard runtime components and train-system configuration files. The leak post identifies stadlerrail.com as the victim domain and lists Java, Python and PowerShell as platforms. ThreatCluster’s news reporting notes Stadler Rail reportedly rejected a ransom demand of CHF 10 million (about $12.3 million) after a breach of a supplier data-exchange platform, with the incident described as occurring in mid-July 2026.

Describes what the group claims on its leak site. A listing is not confirmation that a breach occurred.

Victim profile

Platforms
FTP Java Python

What was taken

Stadler Rail Database Leaked

Data categories
passenger-information system materialstrain display system materialsTCU, TFT, TUI, HMI and DCU component packagesDTP, INOI Client, INOI Upstart, IPEP, LED and RemoteLogger packagesPAN, IPAMP and VSU release packagesInformation Middleware packagesonboard Java and Python runtime componentstrain-system configuration filesswitch configuration foldersASAN configuration foldersSNMP and MIB filesvehicle-number and IP mapping filesPIS logs and diagnostic logsCCTV filesDOO camera recordingsAPC / passenger-counting support filessimulator tools and test utilitiesSQL database creation scriptsPowerShell, shell, batch and Python scriptsEN45545 fire/smoke documentationrelease notes, manuals, drawings, datasheets and training records

Also stated on the leak page

Fields this group publishes that do not map to a standard column. Labels are the site's own.

download_link
https://fex.net/s/bxmnyyk
Download full database
https://fex.net/s/bxmnyyk

Leak-site images (11)

Images from the victim's leak listing. Thumbnails scraped from the onion page are blurred by default — click a thumbnail to view.

ThreatCluster capture
onion leak page11 KB
Logo of Keysight Technologies featuring a red waveform graphic and the company name in white text.
onion leak page128 KB
onion leak page11 KB
Logo featuring the text "mansfield" in a stylized font, with "FAMILY DENTISTRY" below it.
onion leak page1.4 KB
Logo featuring a stylized letter "P" in orange with a black play button icon integrated into the design.
onion leak page7.5 KB
onion leak page5.8 KB
Logo featuring the text "Al-Futtaim" in blue, with "automotive" in a smaller font below it, accompanied by a geometric symbol.
onion leak page5.6 KB
The image features a logo with stylized figures in orange and blue, representing people, alongside the text "ALZONE" in blue.
onion leak page7.0 KB
Logo of Emirates Flight Catering, featuring stylized text and a decorative emblem.
onion leak page6.8 KB
Logo of Dharma Group featuring a stylized design with blue and green colors, accompanied by the text "DHARMA GROUP" below it.
onion leak page7.7 KB