Frequency
10
occurrences
First Seen
November 5, 2026
Last Seen
November 6, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
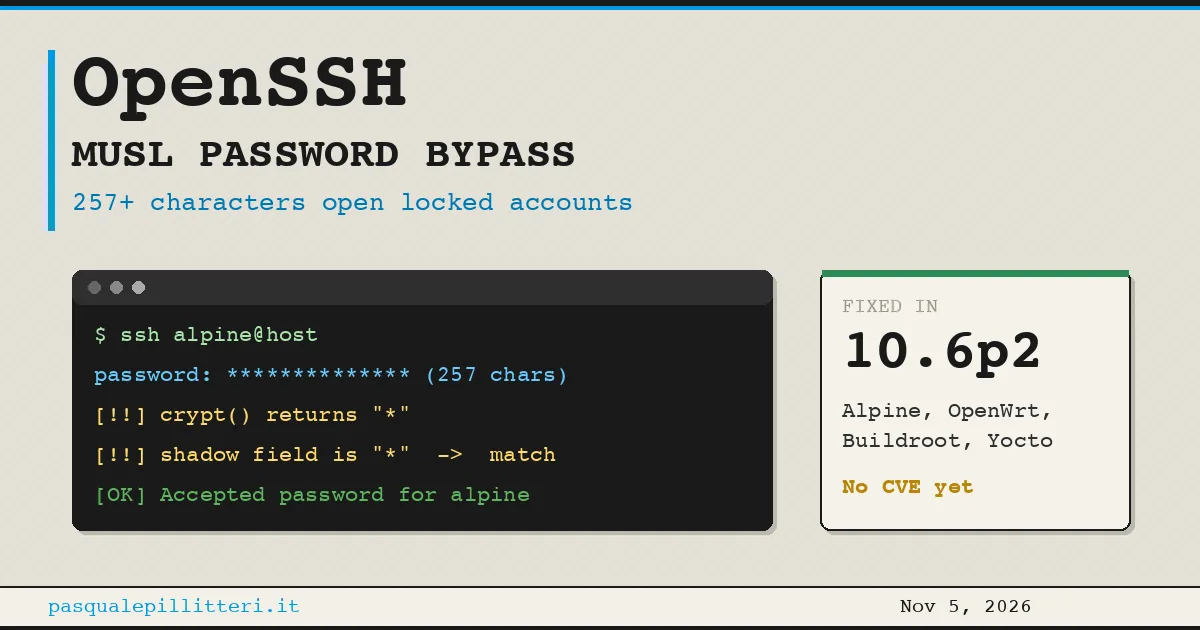
A critical vulnerability, tracked as CVE-2026-123158, has been discovered in OpenSSH affecting Alpine Linux and other musl-based systems. The flaw allows attackers to bypass password authentication for accounts configured with no password by entering a long password (between 257 and 1,024 characters...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (1)
Related Articles (10)





1 / 2