Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
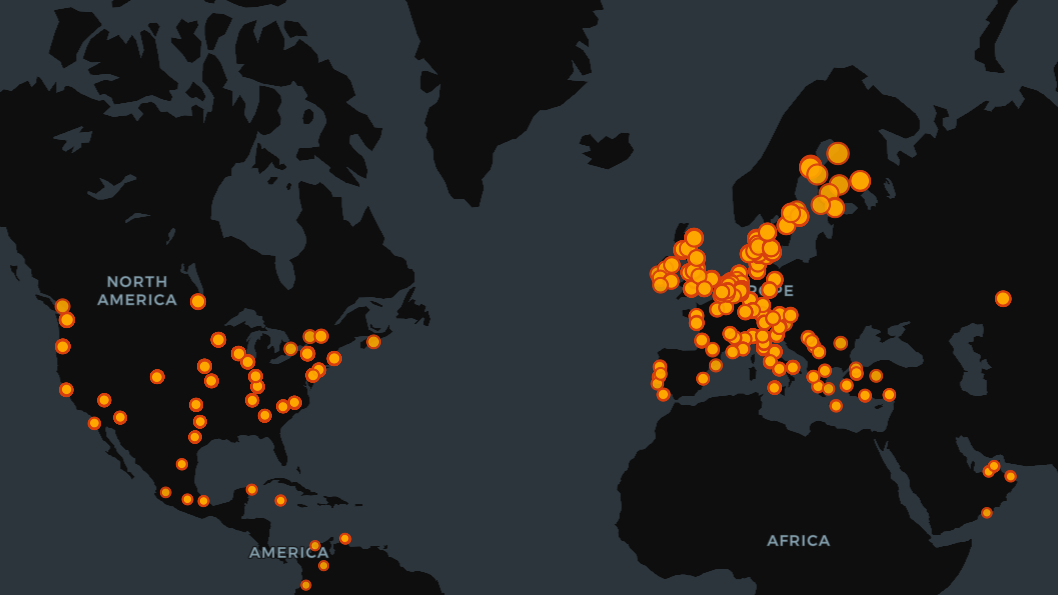
On September 26, 2026, security firm watchTowr reported two unpatched zero-day vulnerabilities in Citrix NetScaler ADC and Gateway appliances, allowing remote code execution (RCE) and actively exploited in the wild. Citrix has confirmed the existence of these vulnerabilities, tracked as CVE-2026-887...
In late September 2026, two critical zero-day vulnerabilities (CVE-2026-88771 and CVE-2026-88772) in Citrix NetScaler ADC and Gateway were actively exploited, allowing remote code execution. The Cybersecurity and Infrastructure Security Agency (CISA) added these CVEs to its Known Exploited Vulnerabi...
The Global Cybersecurity Vulnerability Enumeration (GCVE) database has been launched in Europe to track IT security vulnerabilities and reduce reliance on U.S. systems. This initiative, accessible at db.gcve.eu, aims to enhance digital sovereignty and was prompted by concerns over the potential disc...