Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
CVE-2025-8088 is a path traversal vulnerability in WinRAR versions up to 7.12, allowing attackers to exploit alternate data streams (ADSes) in RAR files to extract malicious payloads to sensitive system locations. Exploitation began in the wild on July 18, 2025, with attackers linked to the Russia-a...
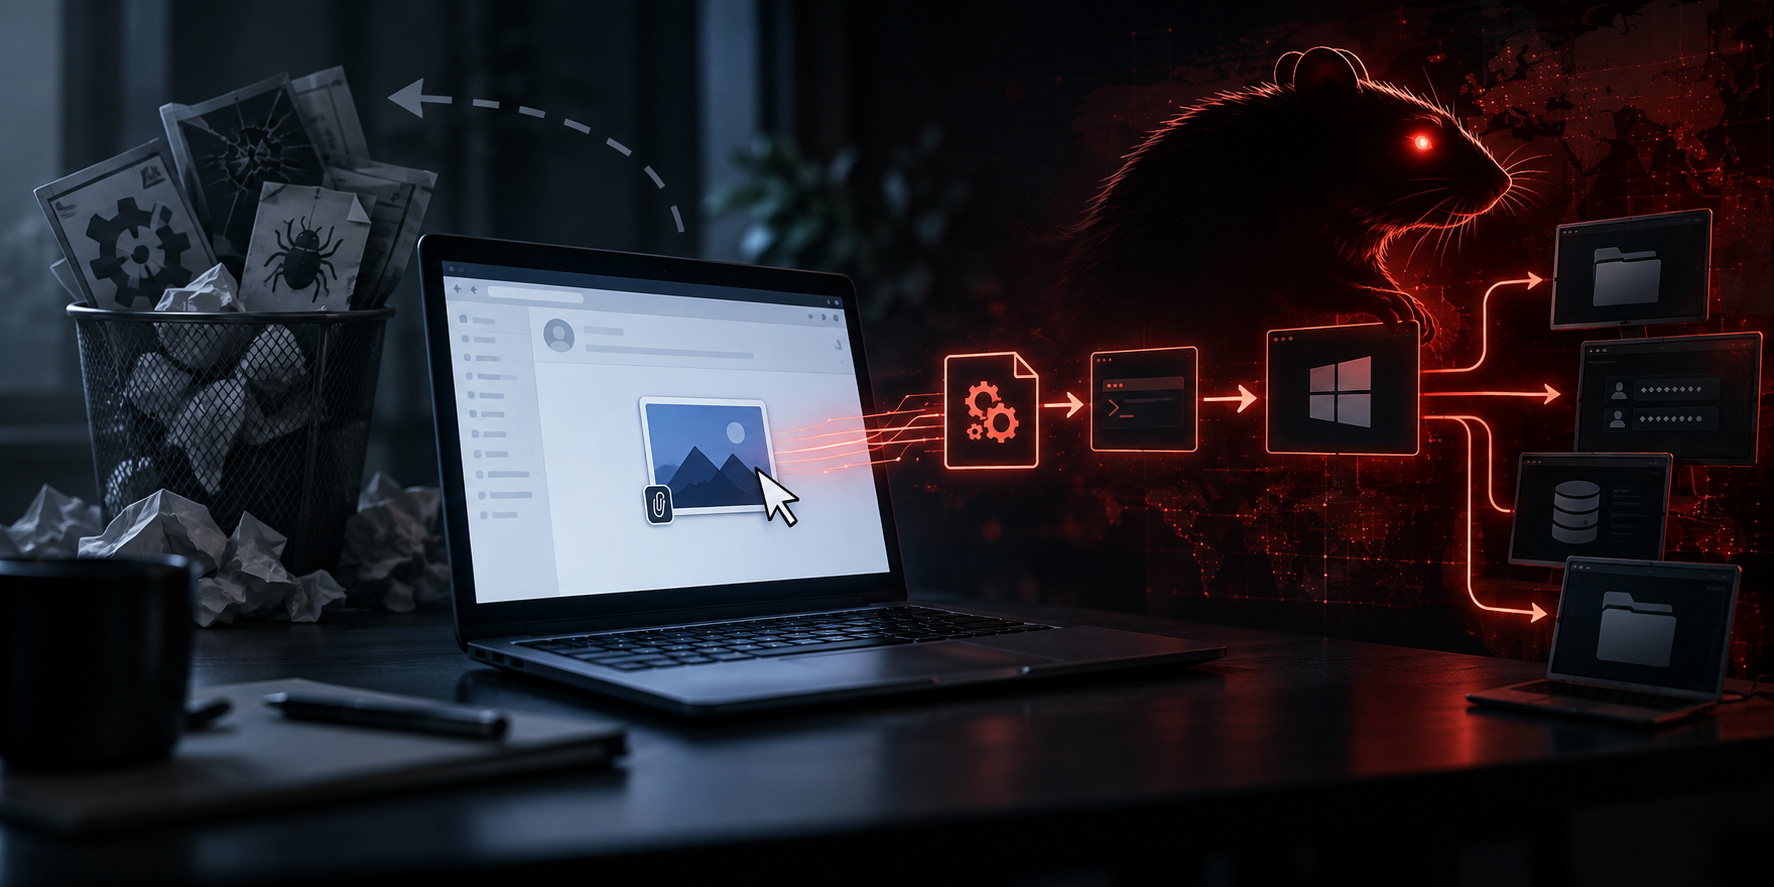
The DarkMe remote access trojan (RAT), previously associated with the Water Hydra threat group, has shifted its distribution method from exploiting zero-day vulnerabilities to using phishing emails. Victims receive emails containing links that appear to lead to image files but instead download a mal...
The Russia-aligned threat actor UAC-0099 has been linked to a new .NET infostealer and RAT named ASHVEIN, targeting Ukrainian government personnel. This malware, also referred to as 'TelemetryBrowser,' features capabilities such as credential theft from Chrome and Firefox, screenshot capture, and re...
The DarkMe malware, a Visual Basic 6 (VB6) remote access trojan (RAT), was identified in two incidents affecting different organizations on August 31, 2026. Previously attributed to the APT group Evilnum, DarkMe has transitioned from using zero-day exploits (CVE-2023-38831 and CVE-2024-21412) to rel...