Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
Fortinet has identified multiple critical vulnerabilities in its FortiSandbox and FortiAuthenticator products, which could allow unauthenticated attackers to execute arbitrary code remotely. The vulnerabilities are tracked as CVE-2026-44277 and CVE-2026-26083, both published on May 12, 2026. FortiAu...
CrowdStrike's recent analysis reveals that hackers are exploiting vulnerabilities almost immediately after public proof-of-concept (PoC) code is released. Between January and July 2026, 91% of vulnerabilities with public PoCs were exploited within 48 hours, with the fastest at just 35 minutes. Notab...
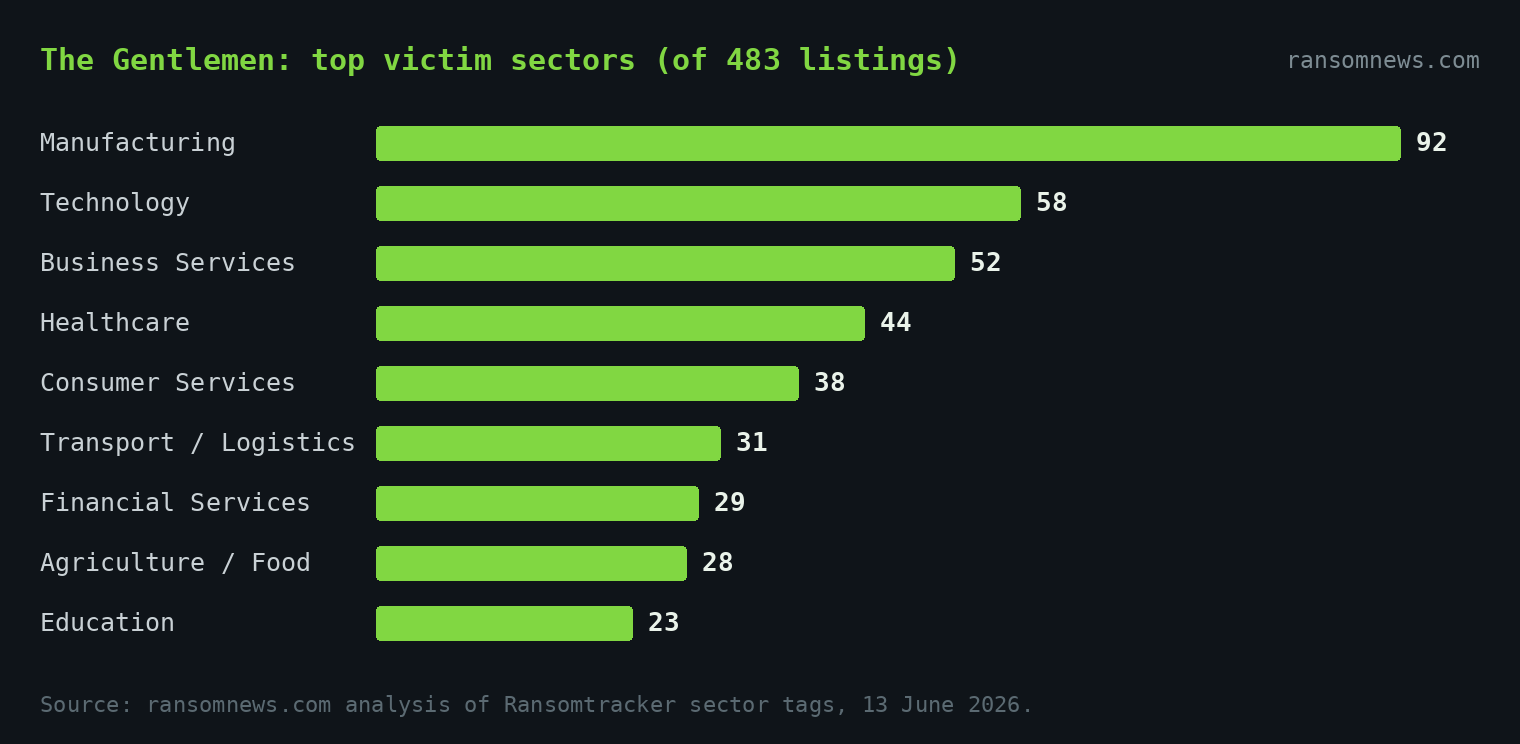
The Gentlemen ransomware group has emerged as a significant threat in 2026, exploiting vulnerabilities in Fortinet systems, particularly CVE-2024-55591, an authentication bypass flaw. They have been observed using brute-force attacks on approximately 1,000 Fortinet VPN instances, often leveraging we...
As of February 12, 2026, organizations worldwide are experiencing an average of 2,090 cyber-attacks per week, largely driven by ransomware incidents. This increase highlights the ongoing challenges faced by businesses in securing their networks against evolving cyber threats.