Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
SonicWall has released a patch for the actively exploited zero-day vulnerability CVE-2025-40602, which affects the Appliance Management Console (AMC) of their devices. This vulnerability allows for deserialization of untrusted data, posing risks to users of SonicWall products. Organizations are advi...
Google's Threat Intelligence Group tracked 90 zero-day vulnerabilities exploited in 2025, a rise from 78 in 2024. Less than half of these vulnerabilities were attributed to specific threat actors, with spyware vendors and China being the most prominent. This increase highlights ongoing cybersecurity...
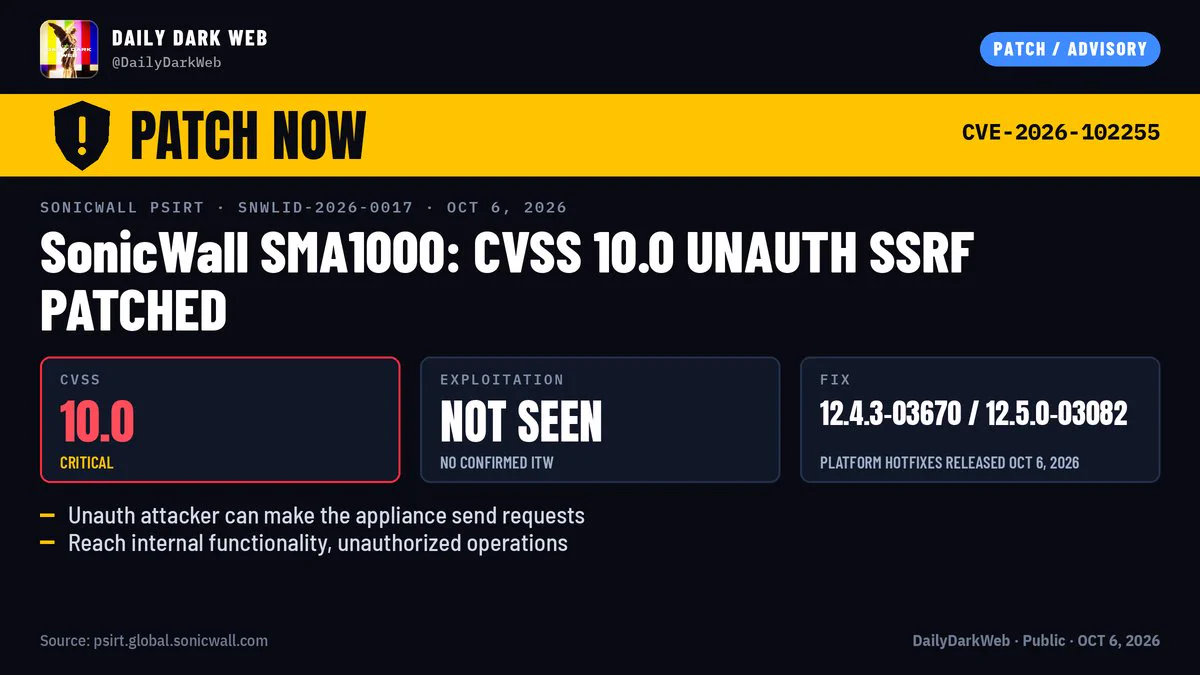
On October 6, 2026, SonicWall released hotfixes for four vulnerabilities in its SMA1000 series appliances, including CVE-2026-102255, a critical server-side request forgery (SSRF) flaw rated 10.0 on the CVSS scale. This vulnerability allows unauthenticated attackers to exploit an unintended access p...
Cisco disclosed a state-espionage campaign targeting its Adaptive Security Appliances (ASA), which are used for firewall and VPN functions. Attackers exploited two zero-day vulnerabilities to infiltrate government entities globally, deploying custom malware backdoors named 'Line Runner' and 'Line Da...