Frequency
2
occurrences
First Seen
February 2, 2026
Last Seen
September 8, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A series of vulnerabilities, including CVE-2025-49144, CVE-2025-31702, and CVE-2026-46333, have been identified, affecting systems like Notepad++ and FortiWeb devices. These vulnerabilities allow for local privilege escalation, SQL injection, and remote code execution. Attackers exploit these flaws...
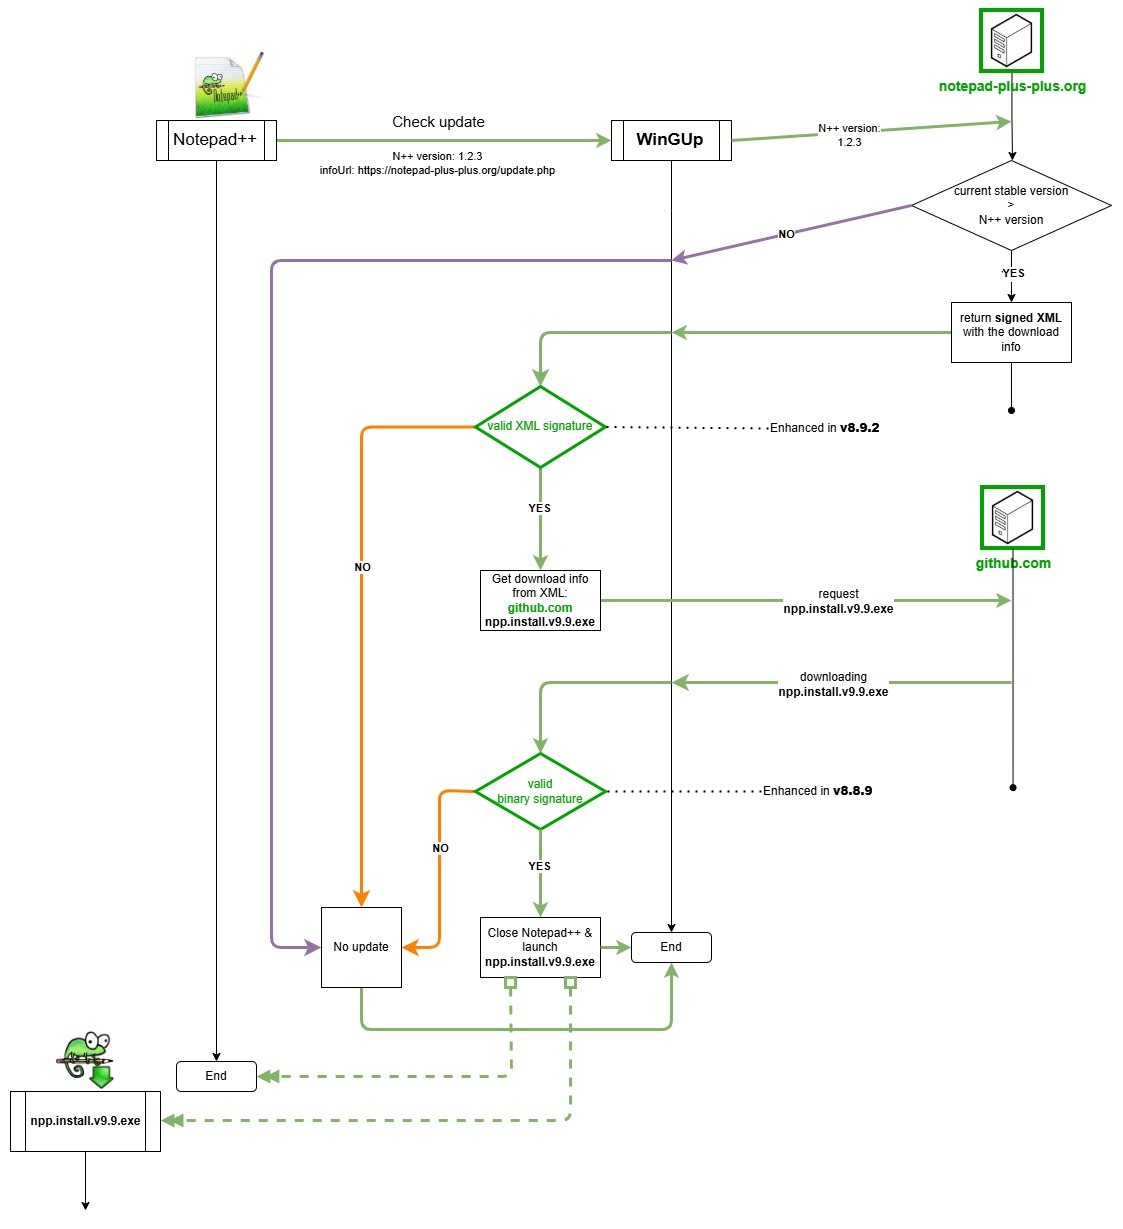
Notepad++ has been hijacked by state-sponsored hackers, specifically a likely Chinese threat actor. The attackers compromised the software's update mechanism between June and December 2025, allowing them to redirect users to malicious servers by exploiting a flaw in update package validation.
Public Exploits
Checking GitHub for proof-of-concept code…