Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control...
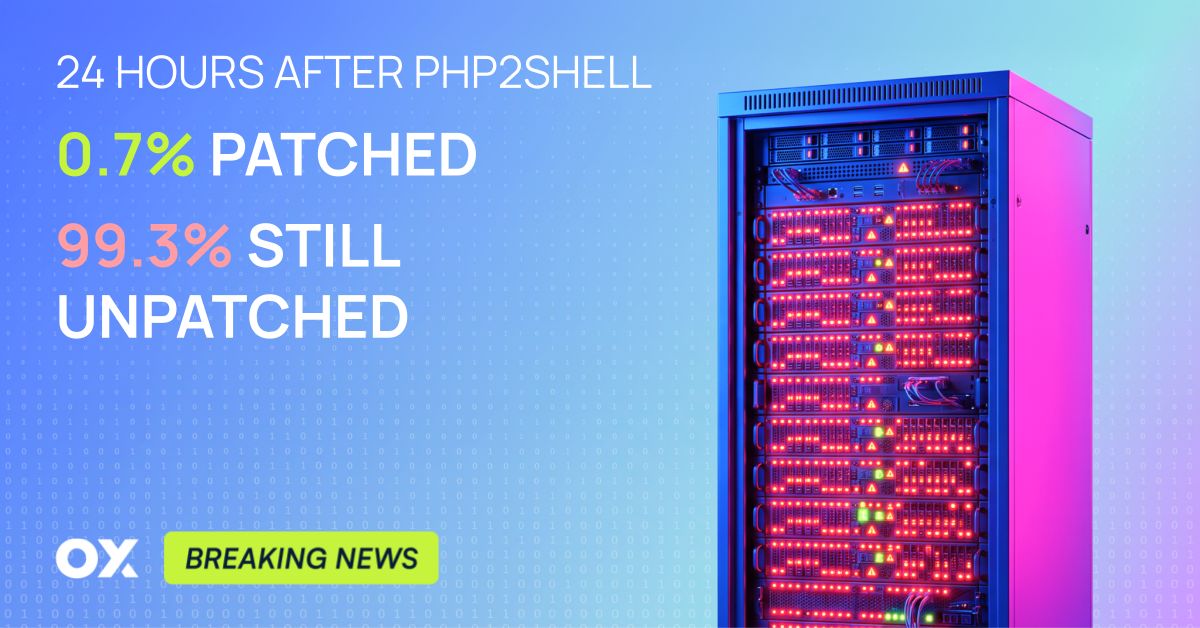
Two critical vulnerabilities in PHP, tracked as CVE-2026-109618 and CVE-2026-109619, were disclosed on October 21, 2026, allowing unauthenticated remote code execution (RCE). The vulnerabilities, collectively known as PHP2Shell, affect all PHP installations serving web requests, including popular pl...
A critical remote code execution vulnerability (CVE-2026-1731) in Bomgar's remote monitoring and management (RMM) tool has led to a significant increase in cyberattacks, particularly involving LockBit ransomware. The flaw, which allows unauthenticated attackers to execute arbitrary commands, was pub...
Google's Threat Intelligence Group (GTIG) reports that software vulnerability disclosures doubled from 5,045 in January 2026 to 10,740 in August 2026, largely influenced by AI-assisted discovery. Notably, 50% of AI-discovered vulnerabilities enable remote code execution (RCE), compared to 26% of non...