Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
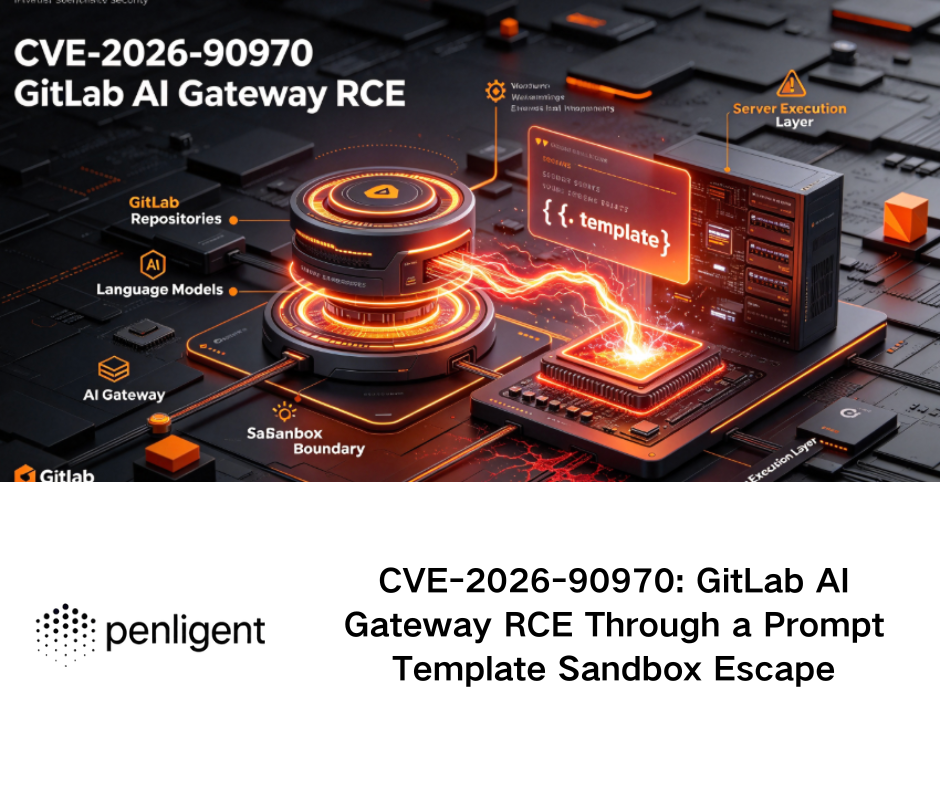
GitLab has disclosed a critical remote code execution vulnerability, CVE-2026-90970, affecting self-hosted AI Gateways. The flaw allows authenticated users with Duo Agent Platform access to escape a prompt template sandbox and execute arbitrary commands on the gateway. GitLab released patches in ver...
GitLab has patched a critical vulnerability identified as CVE-2026-1868, which has a CVSS score of 9.9. This flaw affects the self-hosted AI Gateway, allowing remote code execution (RCE) through insecure templates. Users of GitLab's self-hosted solutions are advised to apply the patch immediately.
On October 17, 2026, OpenCode disclosed a breach affecting 1.4% of its Console users, where unauthorized access to a legacy system potentially exposed API keys for third-party AI providers, including OpenAI and Anthropic. The breach, described as a 'large scale distillation attack', impacted users w...