Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
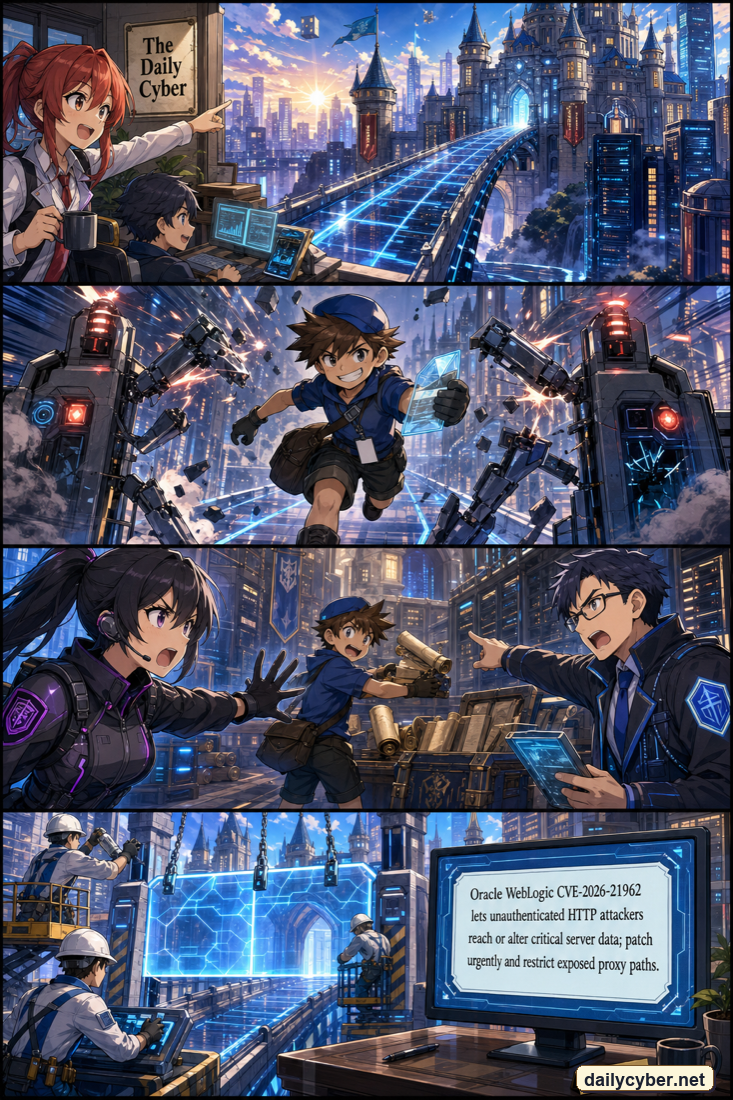
Hackers are actively exploiting a critical Remote Code Execution (RCE) vulnerability in Oracle WebLogic Server, tracked as CVE-2026-21962, which has a maximum CVSS score of 10.0. This unauthenticated flaw allows attackers to execute arbitrary code on affected systems. The vulnerability was published...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-21962, a critical vulnerability affecting Oracle HTTP Server and WebLogic Server Proxy Plug-in, to its Known Exploited Vulnerabilities catalog. This flaw, with a CVSS score of 10.0, allows unauthenticated attackers t...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning regarding the active exploitation of a two-year-old vulnerability in Oracle WebLogic Server, tracked as CVE-2024-21182. This flaw, which affects versions 12.2.1.4.0 and 14.1.1.0.0, allows unauthenticated attackers...
On September 23, 2026, the FBI disclosed an investigation into a data breach by the hacking group ShinyHunters, which claims to have stolen sensitive personal information of approximately 38,000 FBI employees and job applicants. The stolen data reportedly includes names, addresses, phone numbers, So...