Frequency
7
occurrences
First Seen
February 20, 2026
Last Seen
August 8, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
On March 12, 2026, SUSE issued a critical security update for Tomcat 11.0.18 to address several vulnerabilities, including CVE-2025-66614, CVE-2026-24733, and CVE-2026-24734. The vulnerabilities include a client certificate verification bypass, improper input validation on HTTP/0.9 requests, and a c...
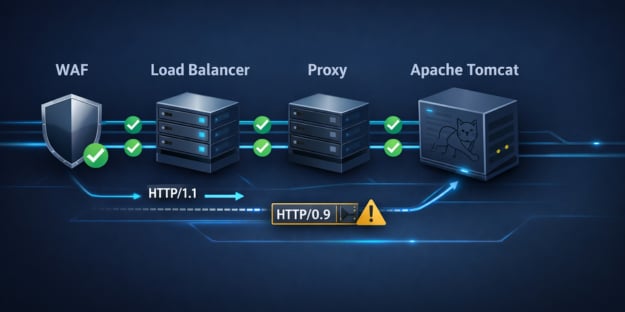
Apache disclosed a vulnerability in Tomcat (CVE-2026-24733) that allows attackers to bypass access controls through legacy HTTP/0.9 requests under specific configurations. This low-severity issue was identified by the Apache Tomcat security team and affects systems using certain access-control rules...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (2)

Related Articles (7)

1 / 2