Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
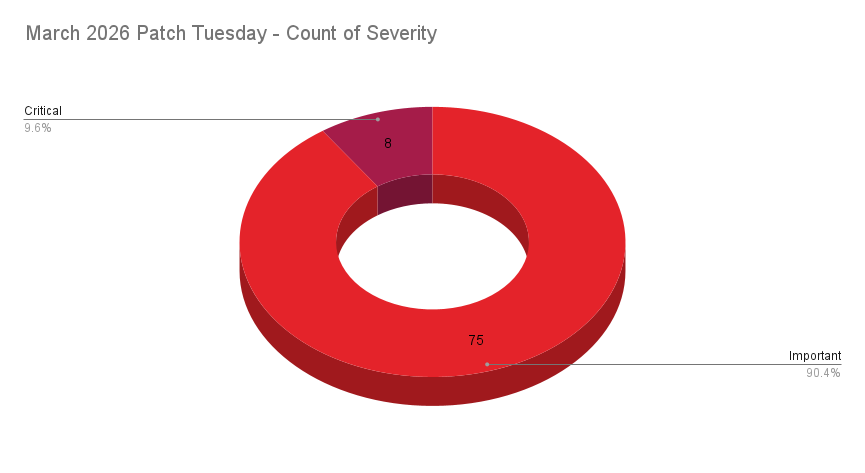
On March 10, 2026, Microsoft released its Patch Tuesday updates, fixing 79 vulnerabilities, including two zero-day flaws. The updates address critical vulnerabilities across various products, with one zero-day actively exploited in the wild, necessitating immediate attention from security teams.
Microsoft Office Excel has multiple vulnerabilities that allow unauthorized attackers to execute code locally. These include an out-of-bounds read, use after free, untrusted pointer dereference, heap-based buffer overflow, and type confusion. A cross-site scripting vulnerability also allows informat...
Microsoft has disclosed a critical zero-day vulnerability in SQL Server, tracked as CVE-2026-21262, which allows authenticated attackers to escalate their privileges to the highest administrative level on affected systems. The flaw was published on March 10, 2026, and poses a significant risk to org...
A newly disclosed vulnerability in the Microsoft .NET Framework, tracked as CVE-2026-26127, allows unauthenticated remote attackers to cause a Denial-of-Service (DoS) condition on affected systems. Microsoft has classified this vulnerability as 'Important' with a CVSS score of 7.5, affecting multipl...