Frequency
13
occurrences
First Seen
April 28, 2026
Last Seen
October 7, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
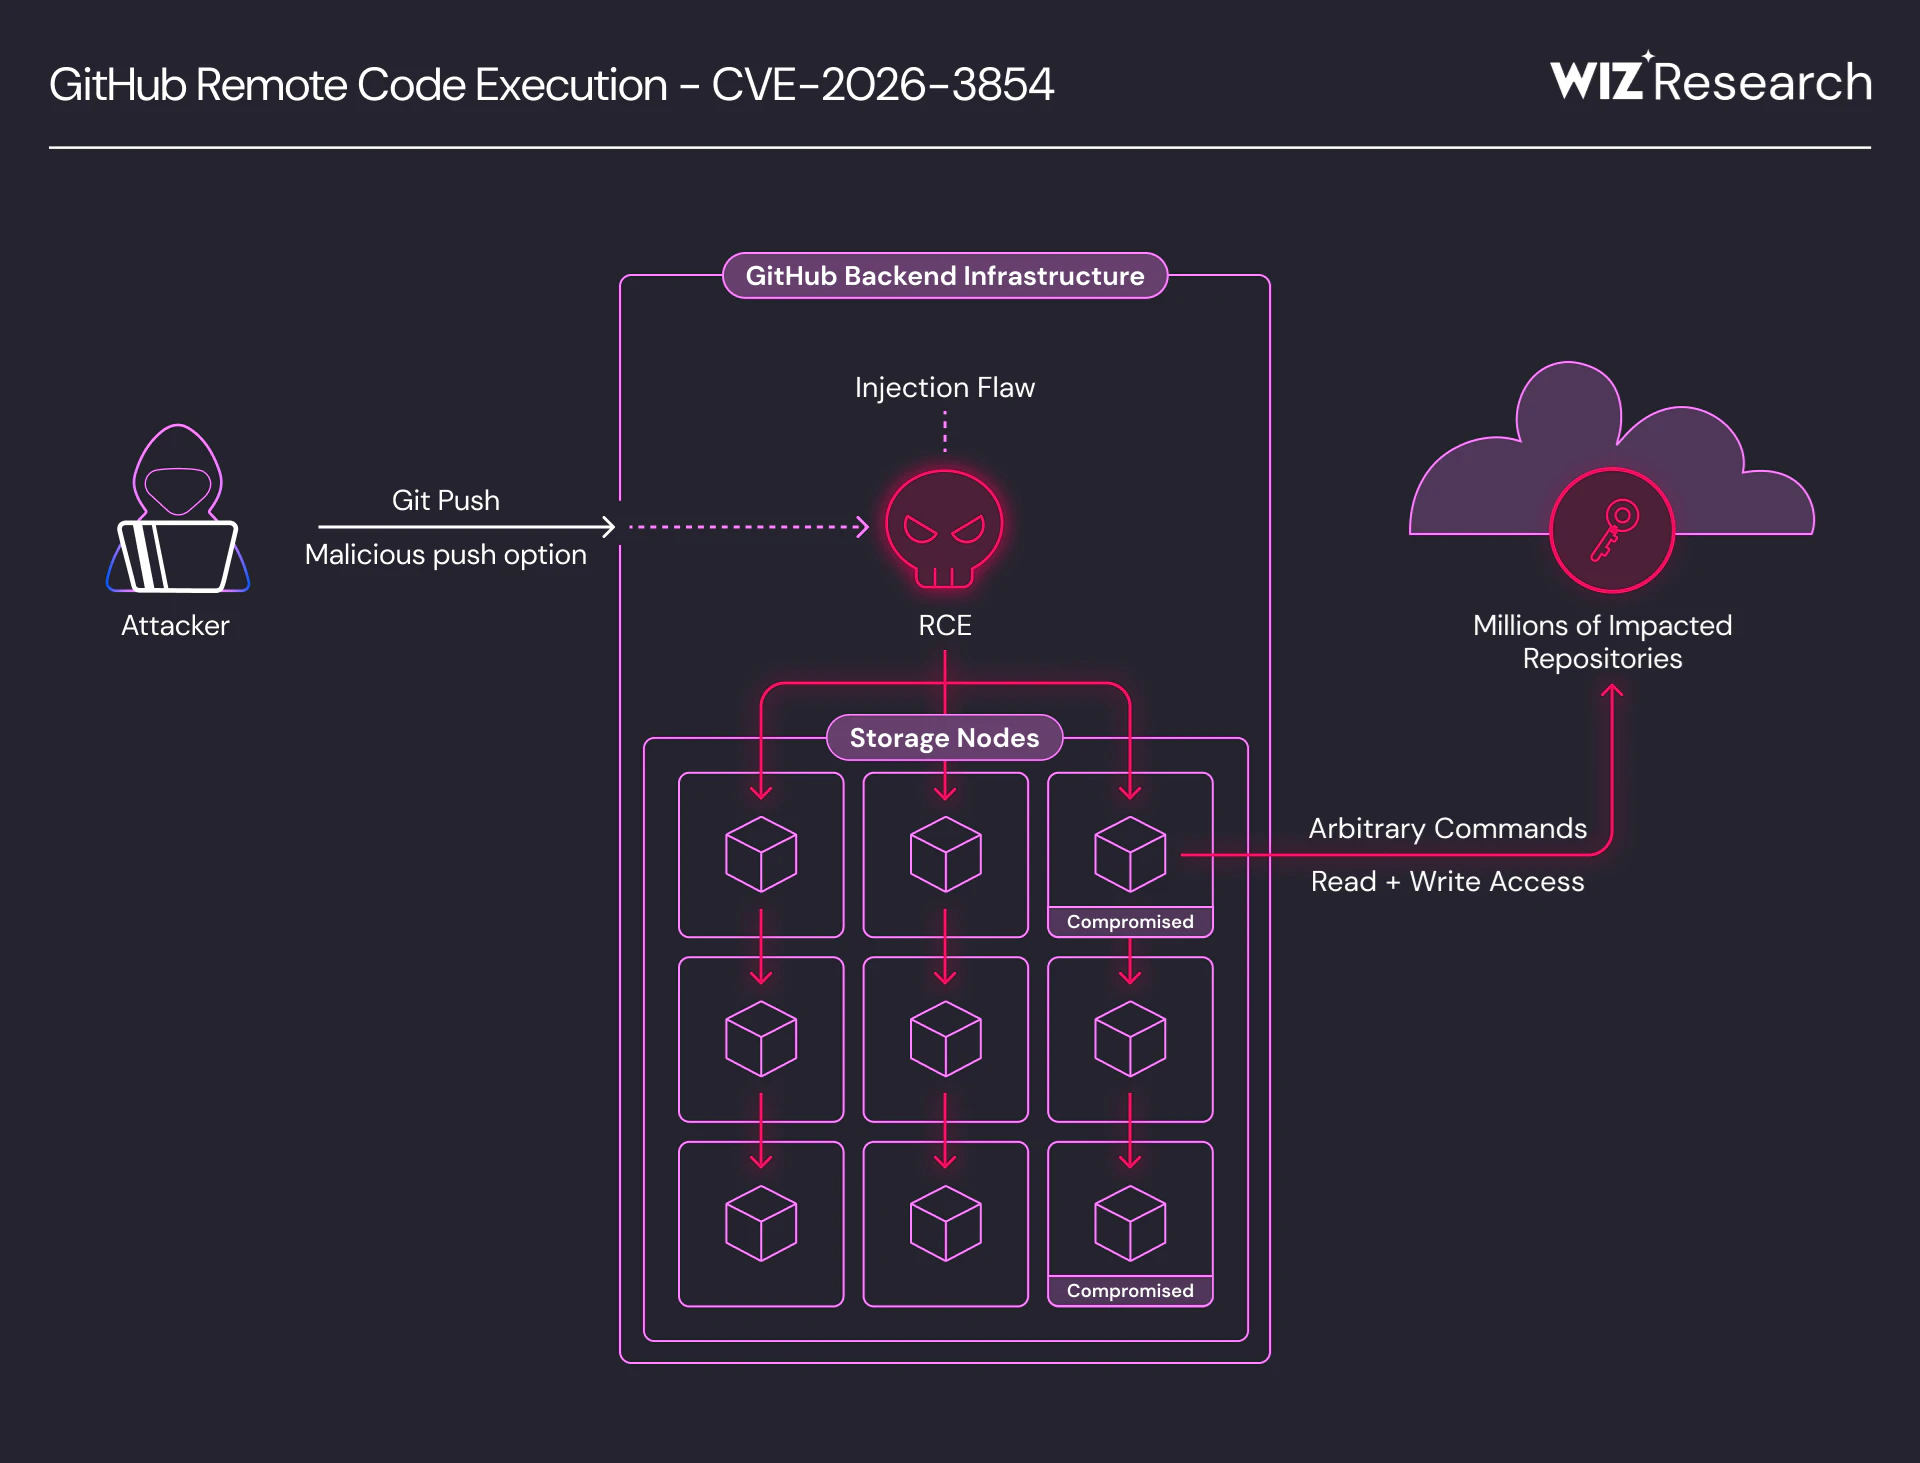
A critical remote code execution vulnerability, tracked as CVE-2026-3854, was discovered in GitHub's internal git infrastructure, allowing authenticated users to execute arbitrary commands via a crafted git push command. The flaw, identified by Wiz researchers using AI, affects both GitHub.com and G...
CVE-2026-3854 is a high-severity vulnerability in GitHub Enterprise Server's push pipeline, allowing authenticated users with push access to execute commands as the git service user. Attackers can inject semicolon-delimited fields into internal metadata through push options, overriding trusted confi...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (2)

Related Articles (13)


1 / 3
Related Entities
Zero-day ExploitData BreachRemote Code ExecutionWizCWE-78 - OS Command InjectionCWE-94 - Code InjectionCWE-77 - Command InjectionCWE-22 - Path TraversalCWE-200 - Exposure of Sensitive InformationT1059 - Command and Scripting InterpreterT1190 - Exploit Public-Facing ApplicationGitHub Enterprise Server