Frequency
4
occurrences
First Seen
May 14, 2026
Last Seen
July 20, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
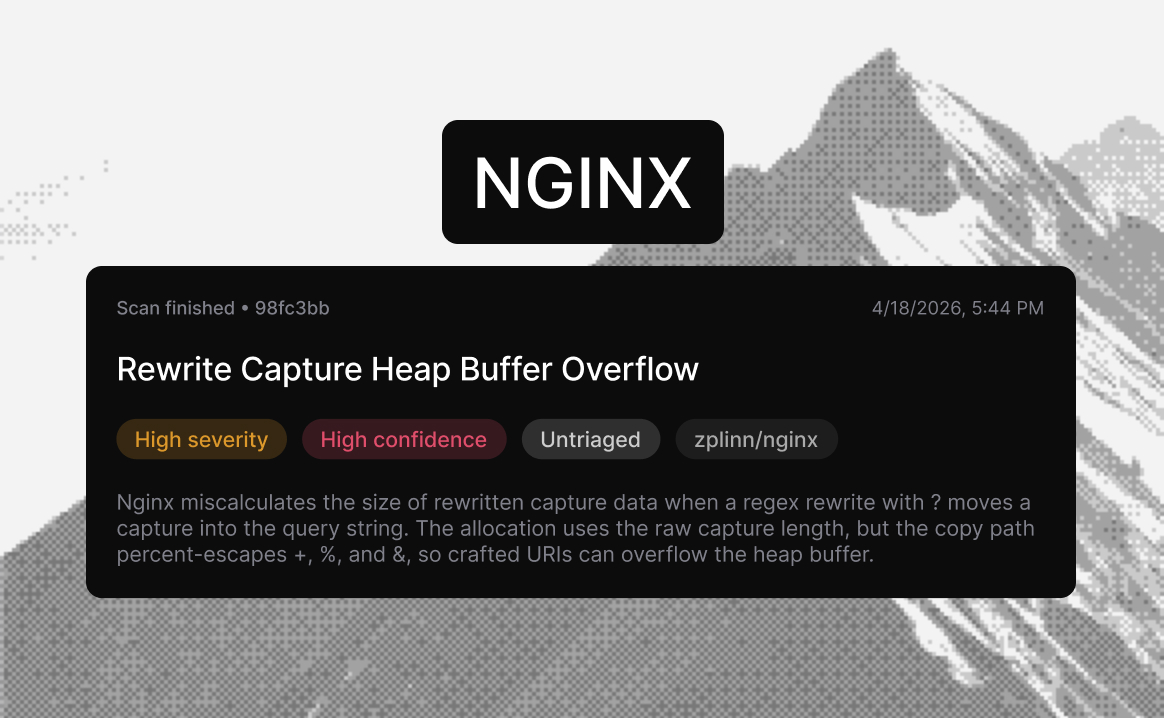
A critical vulnerability, CVE-2026-42945, has been discovered in the NGINX web server's ngx_http_rewrite_module, allowing unauthenticated attackers to execute remote code or crash servers. This heap-based buffer overflow has existed for 18 years, affecting all versions from 0.6.27 to 1.30.0. Attacke...
On June 3, 2026, Ubuntu published a security advisory detailing multiple vulnerabilities in nginx affecting various Ubuntu LTS versions. Key issues include improper handling of memory operations in the ngx_mail_smtp_module (CVE-2025-53859), which could leak sensitive information, and flaws in the ng...
Public Exploits
Checking GitHub for proof-of-concept code…