Frequency
7
occurrences
First Seen
June 17, 2026
Last Seen
August 4, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
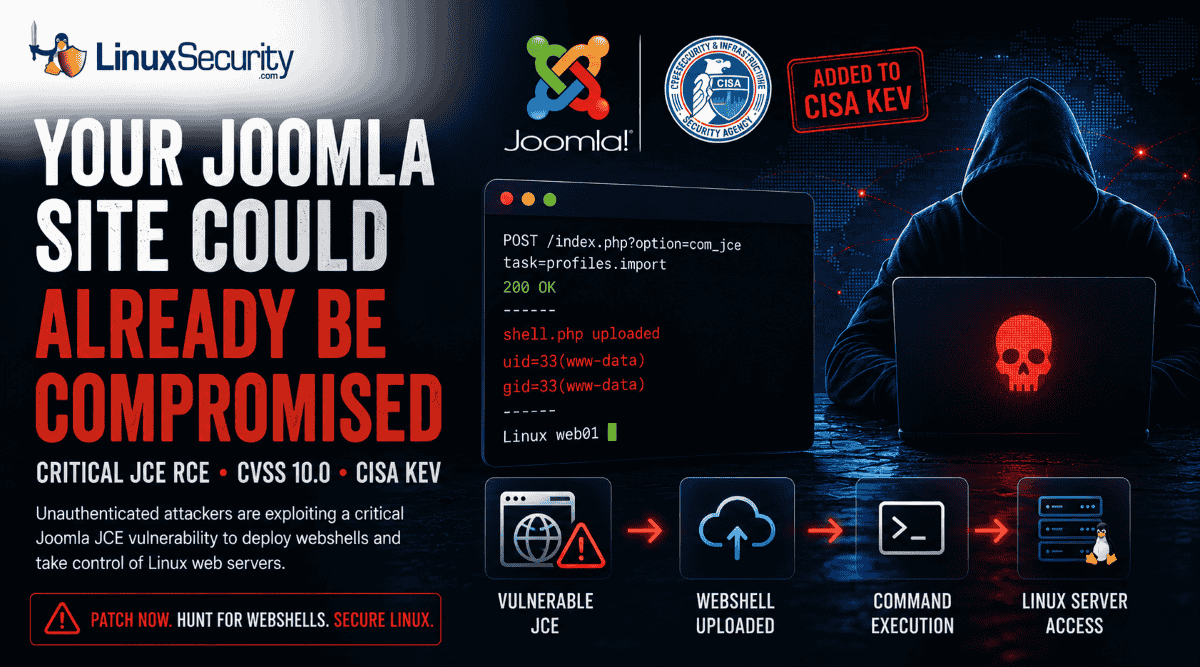
Two critical vulnerabilities affecting Joomla extensions have been reported: CVE-2026-48907 in the Joomla Content Editor (JCE) and CVE-2026-48908 in the SP Page Builder. Both vulnerabilities allow unauthenticated remote attackers to execute arbitrary PHP code on affected servers, leading to potentia...
A critical vulnerability in the Joomla Content Editor (JCE), tracked as CVE-2026-48907, allows unauthenticated attackers to execute remote code on affected Joomla sites. This flaw affects JCE versions below 2.9.99.6 and has a CVSS score of 10.0. Attackers exploit this vulnerability by importing rogu...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (2)
Related Articles (7)


1 / 2