Frequency
2
occurrences
First Seen
October 14, 2026
Last Seen
October 15, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
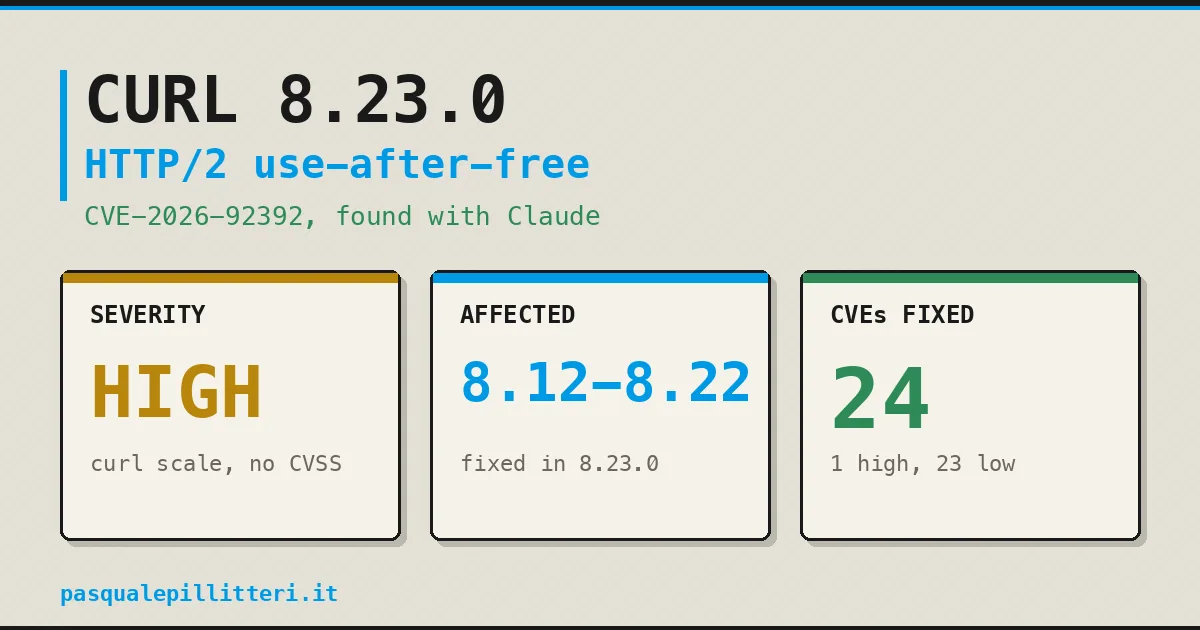
On October 14, 2026, curl released version 8.23.0 to address a critical use-after-free vulnerability (CVE-2026-92392) affecting versions 8.12.0 to 8.22.0. This flaw allows a malicious HTTP/2 server to execute code on the client's machine during file uploads, requiring specific conditions to be met....
Public Exploits
Checking GitHub for proof-of-concept code…