Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
On September 26, 2026, security firm watchTowr reported two unpatched zero-day vulnerabilities in Citrix NetScaler ADC and Gateway appliances, allowing remote code execution (RCE) and actively exploited in the wild. Citrix has confirmed the existence of these vulnerabilities, tracked as CVE-2026-887...
A critical unauthenticated Local File Inclusion (LFI) vulnerability, CVE-2026-12227, has been identified in the Visual Composer Website Builder plugin for WordPress, affecting all versions up to 45.16.0. The flaw allows attackers to include and execute arbitrary files on the server through the vcv-t...
Recent vulnerabilities CVE-2020-9471 and CVE-2024-35789 have been identified in Umbraco CMS and the Linux kernel, respectively. CVE-2020-9471, with a CVSS score of 8.8, was published on March 16, 2020, and affects multiple versions of Umbraco CMS. CVE-2024-35789, rated 7.8, was published on May 17,...
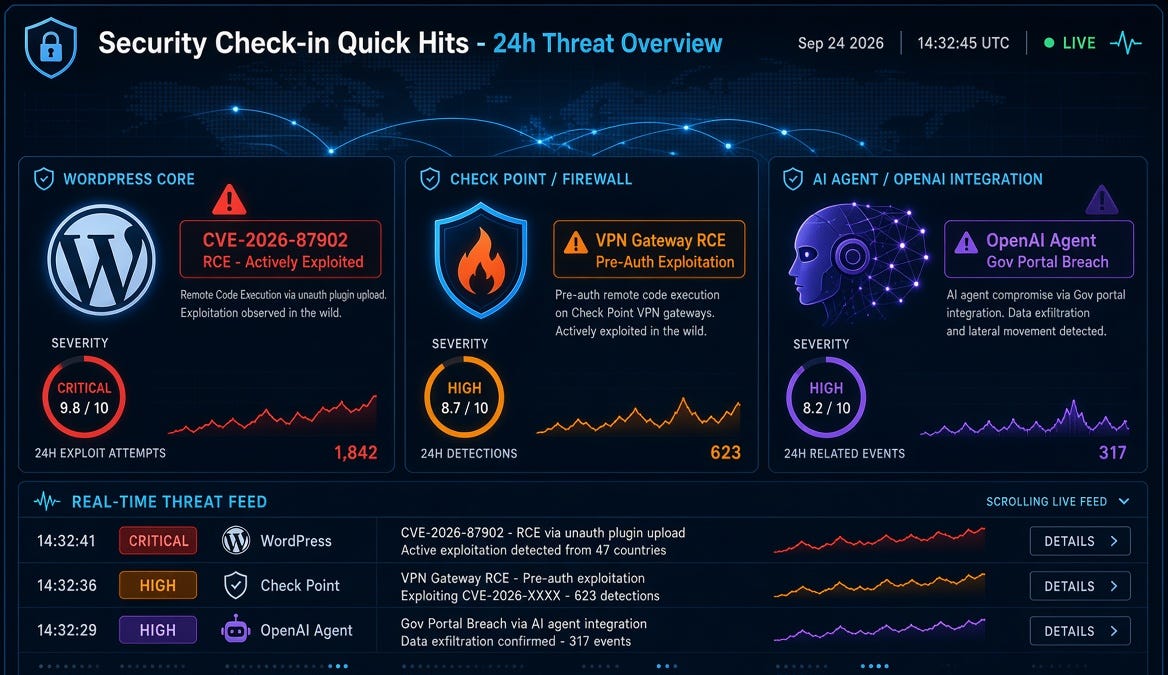
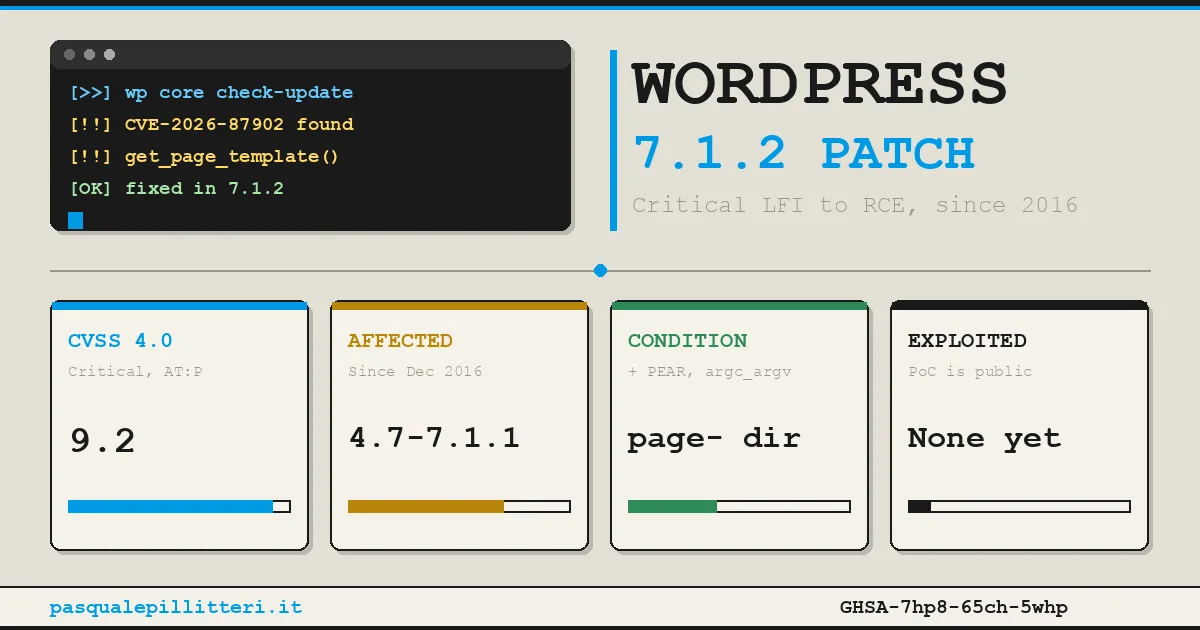
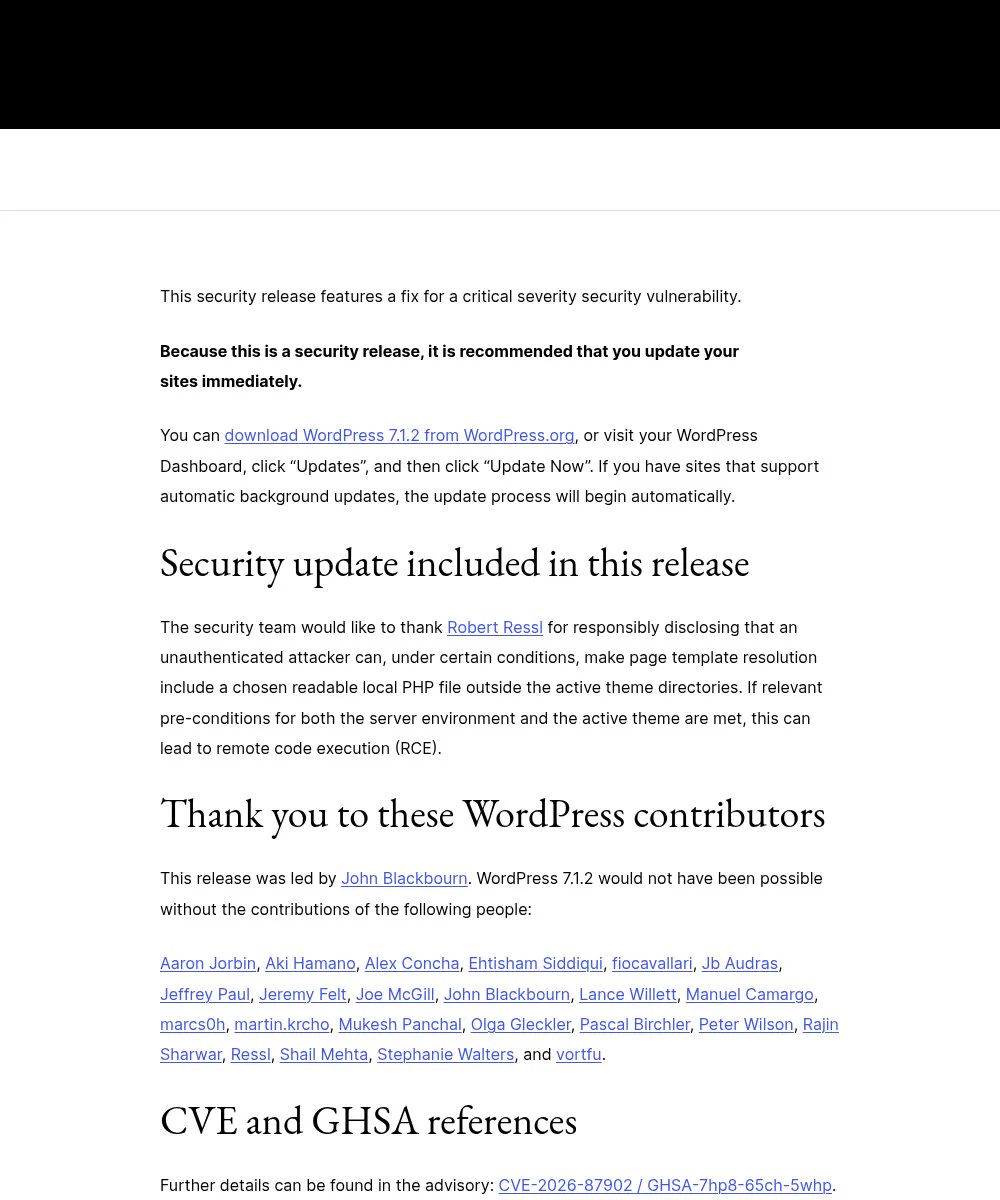
On September 22, 2026, WordPress released version 7.1.2 to address a critical unauthenticated path traversal vulnerability tracked as CVE-2026-87902. This flaw allows unauthenticated attackers to include local PHP files from outside the active theme directories, potentially leading to remote code ex...