Threat intelligence API / integrations
n8n
A community node for n8n that puts ThreatCluster in your workflows: incident clusters, CVEs with exploitation signals, validated indicators, entity profiles and ransomware leak-site activity, plus a polling trigger that fires on new incidents, new leak-site victims and newly exploited CVEs. Works on n8n Cloud and self-hosted.
Packagenpm: n8n-nodes-threatclusterSource on GitHubMIT
Prerequisites
- A ThreatCluster API key. Every plan, including Free, has one: sign in, open Settings → API & Feeds and select Generate API Key. Free keys get 100 credits a day and read the last seven days.
- n8n Cloud, or a self-hosted n8n where community nodes are enabled (they are by default; the owner account installs them under Settings → Community Nodes).
Setup
- Install the node. In the n8n UI: Settings → Community Nodes → Install, enter
n8n-nodes-threatclusterand confirm. Self-hosted without the UI:cd ~/.n8n/nodes npm install n8n-nodes-threatcluster
Restart n8n after a manual install. - Add the credential. Credentials → New → ThreatCluster API, paste the key, select Test. The test calls
GET /me, which costs zero credits, so testing never spends your budget. - Drop a ThreatCluster node or a ThreatCluster Trigger into a workflow and pick the credential.
The action node
Seven resources, fifteen operations. List responses come back as one item per row, which is what the nodes downstream expect, and every item carries a _meta object with what the call cost and how many credits remain today.
- Threat Incident: Get Many, Get, Get IOCs, Get STIX, Search.
- Vulnerability: Get Many with KEV, public-exploit and severity filters, Get.
- Dark Web: Get Victims, Get Groups.
- Entity: Search, Get.
- IOC: Get Feed.
- Ask AI: Ask the Corpus, Ask About an Incident. Paid plans only.
- Account: Get Credits. Free to call.
A first workflow
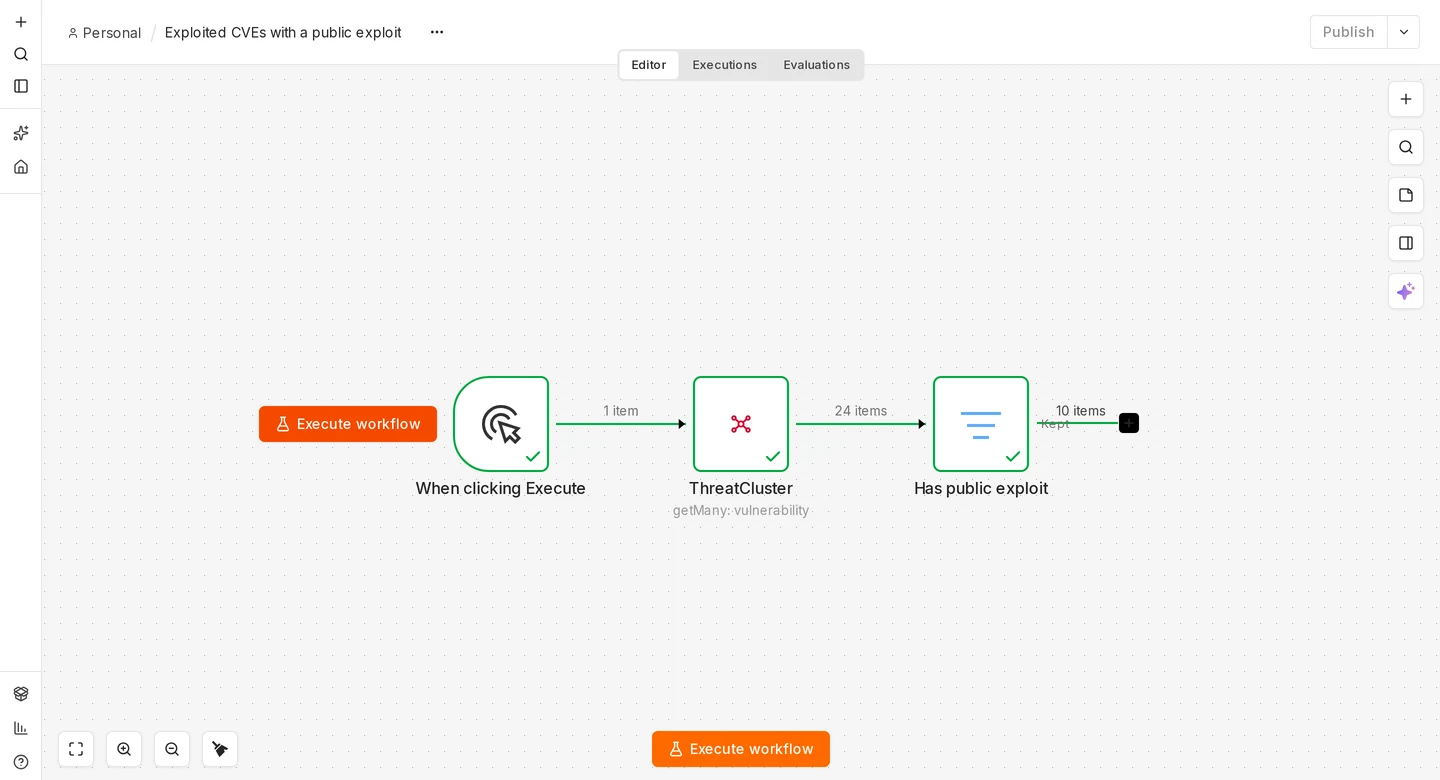
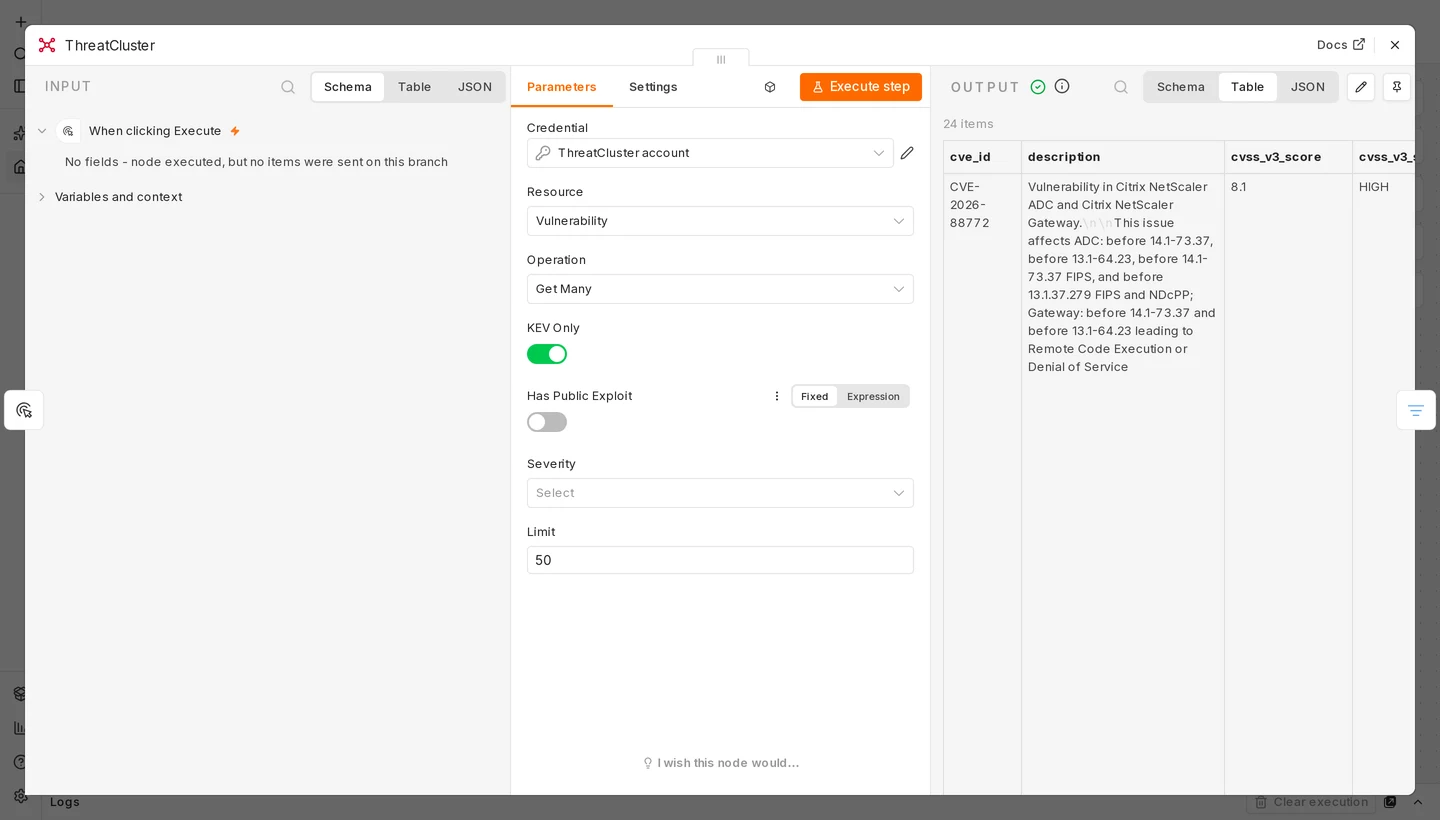
Three nodes: a manual trigger, a ThreatCluster node set to Vulnerability → Get Many with KEV Only on, and a Filter that keeps rows where has_exploit is true.
Open the node to see its settings beside the rows it returned:
Five workflows, run end to end
Each workflow was built and run on 29 September 2026 in n8n 2.41.3 against the live API; the demo posts to a local stand-in, so point the last node at your own tool.
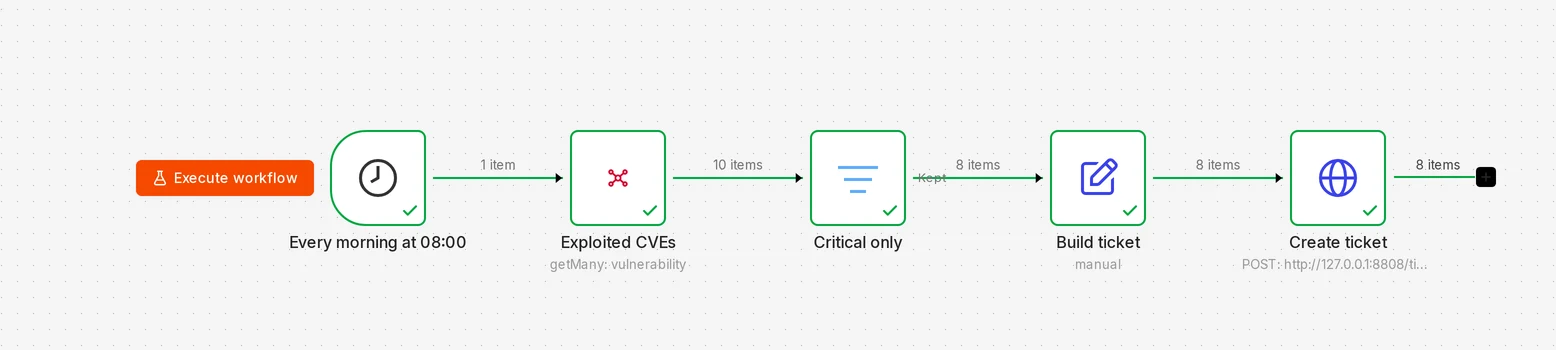
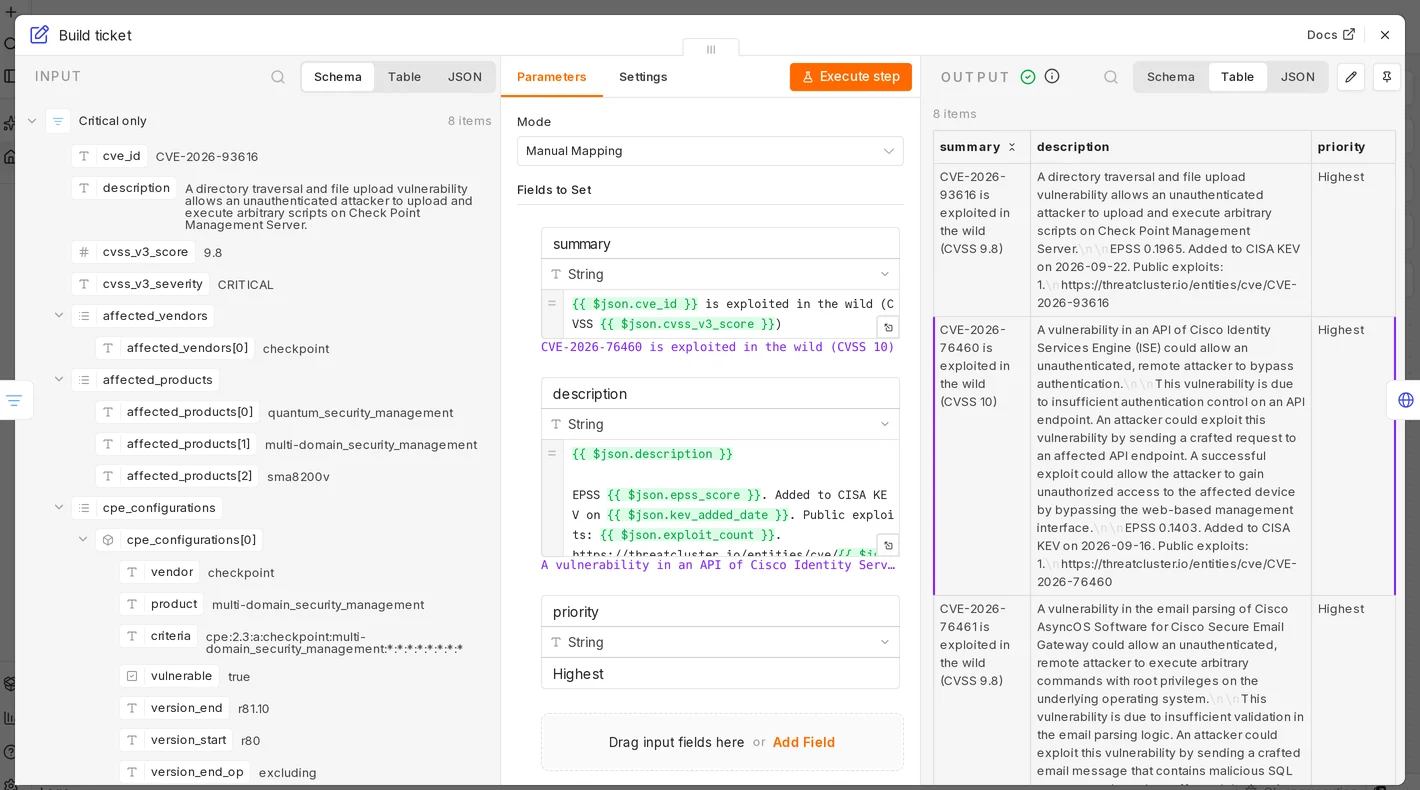
Exploited CVE triage to a ticket 5 nodes, 1 credit a run
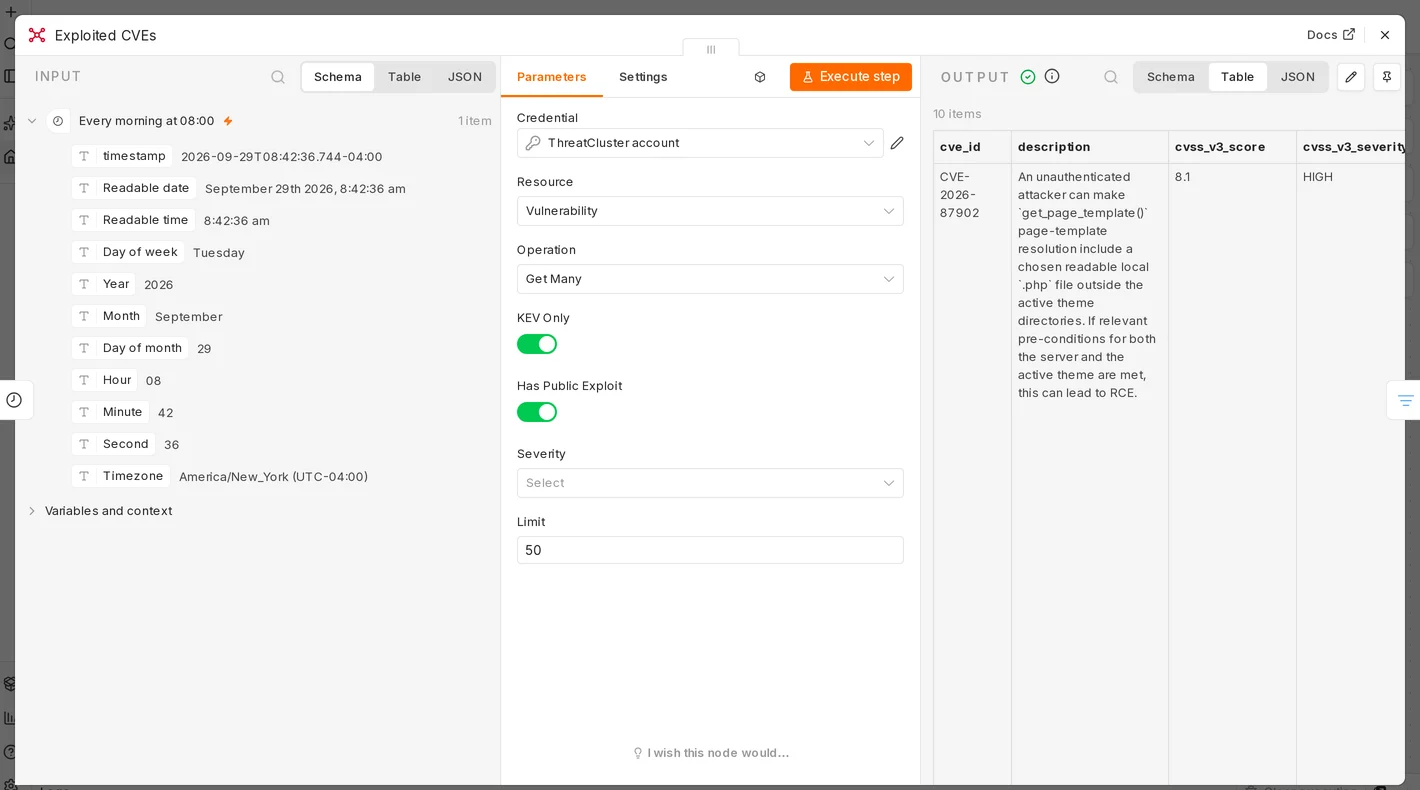
Every morning the ThreatCluster node lists CVEs that are in CISA KEV and have a public exploit. A Filter keeps the criticals, an Edit Fields node writes a ticket for each, and the last node creates it.
Import it: cve-triage.json
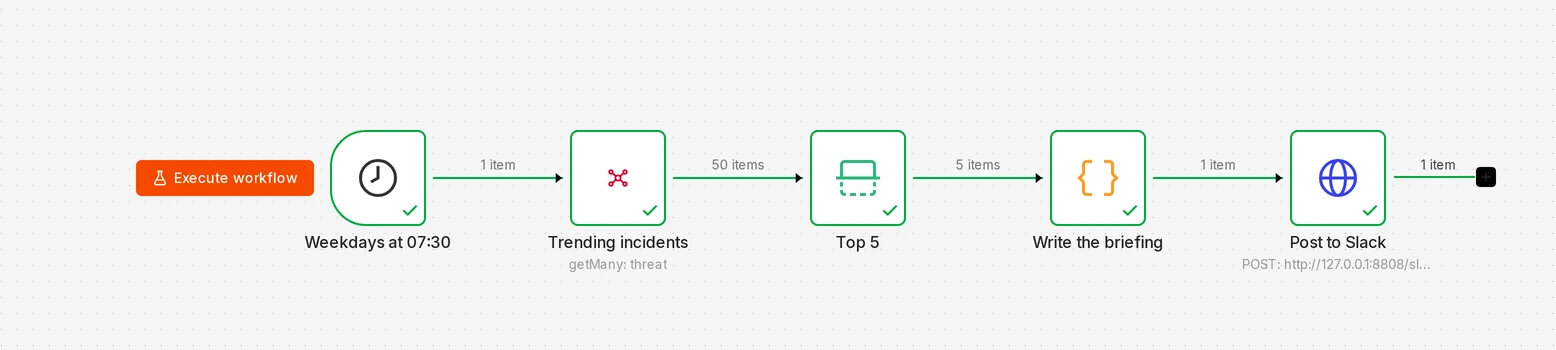
Morning threat briefing 5 nodes, 1 credit a run
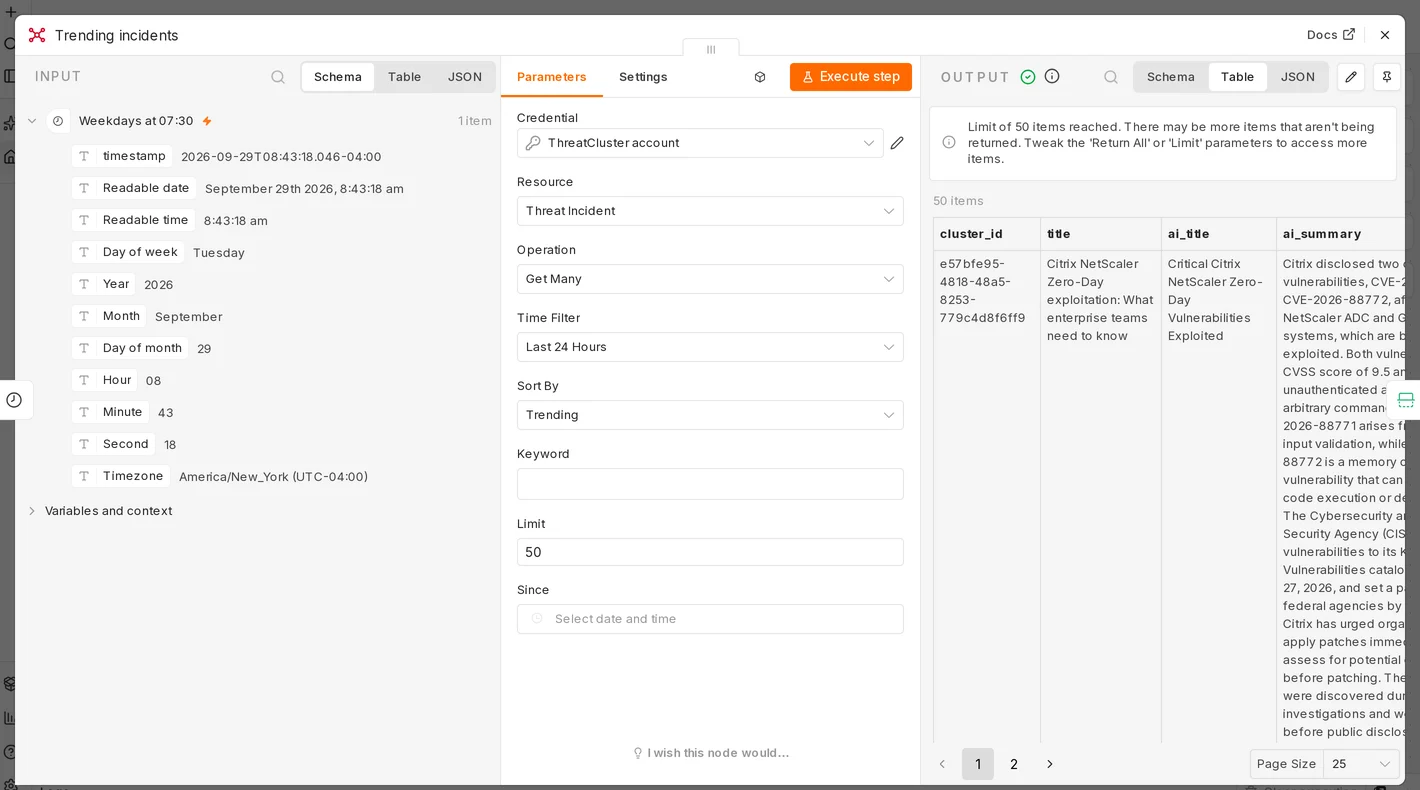
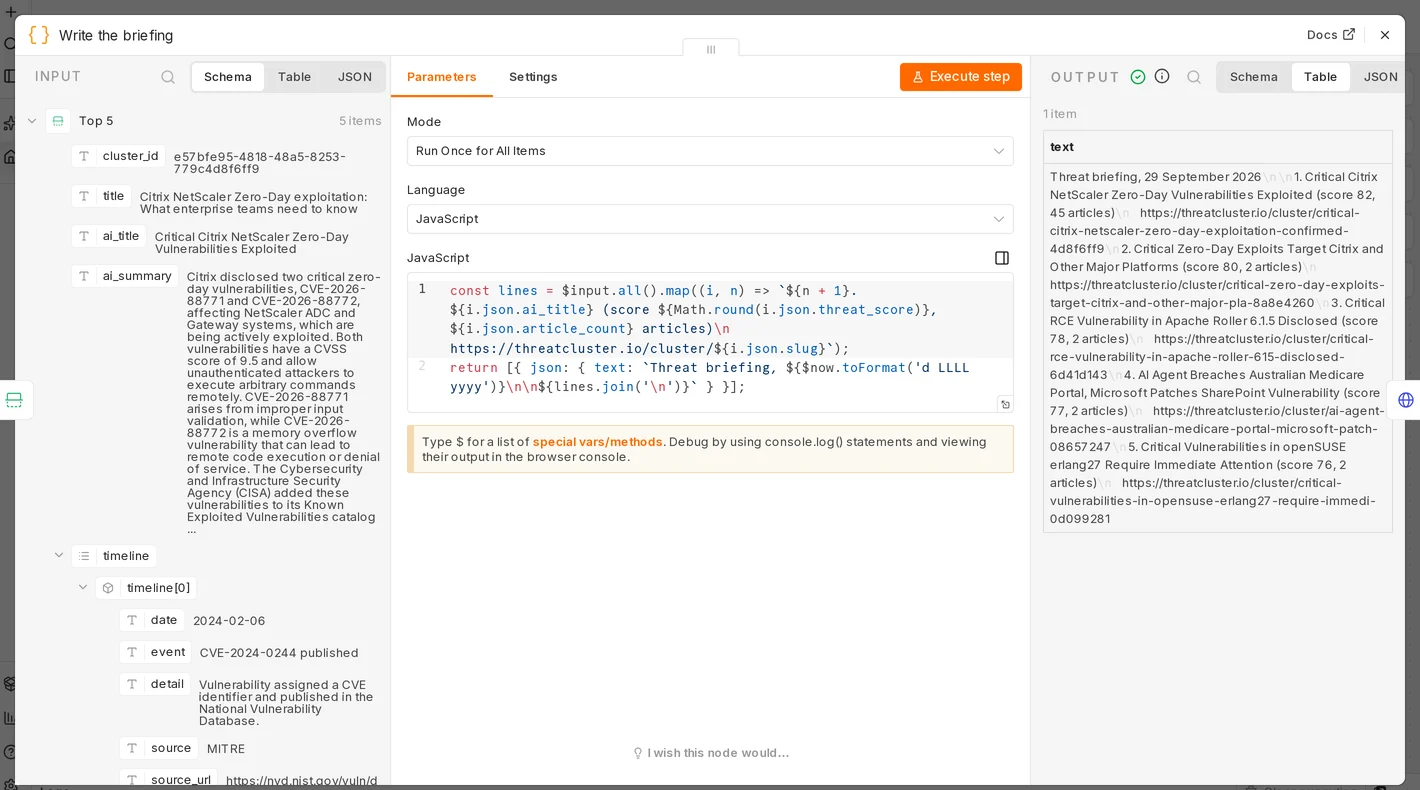
On weekdays at 07:30 the node fetches the incidents trending over the last 24 hours. A Limit node keeps the top 5 and a Code node turns them into one message.
Import it: morning-briefing.json
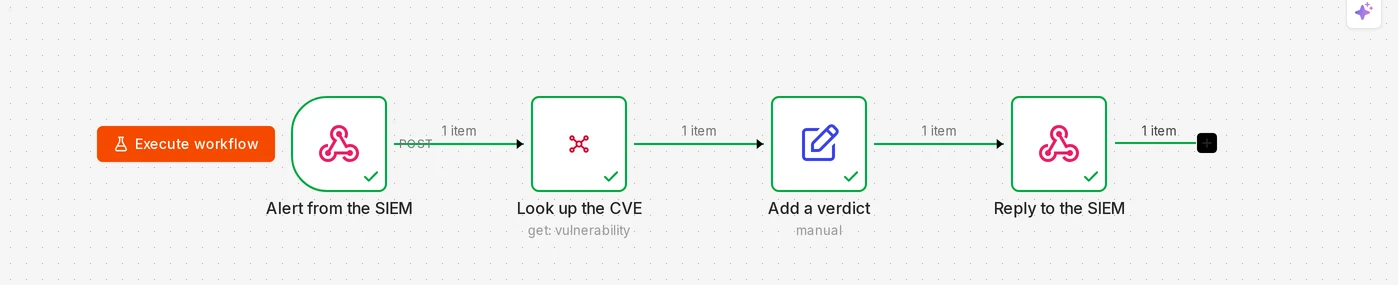
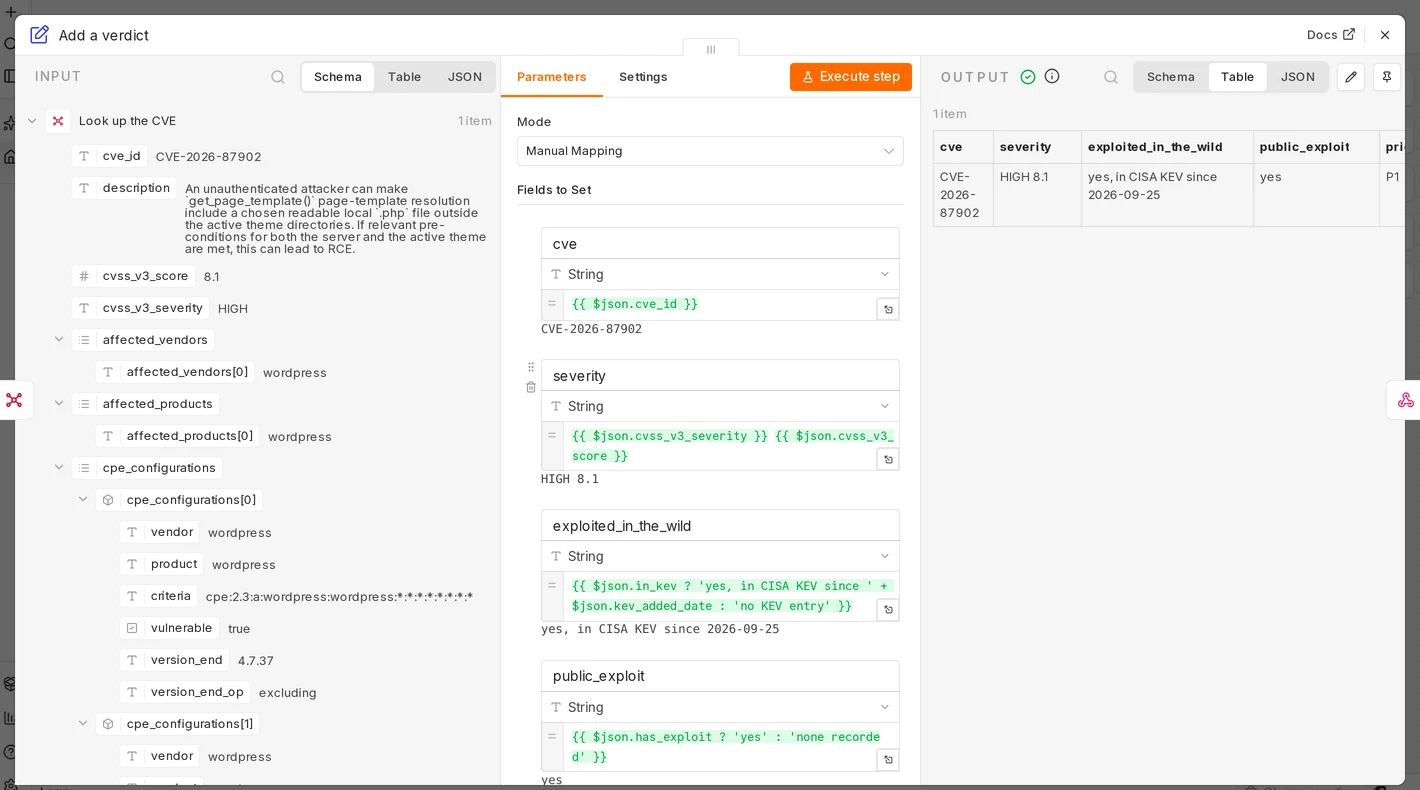
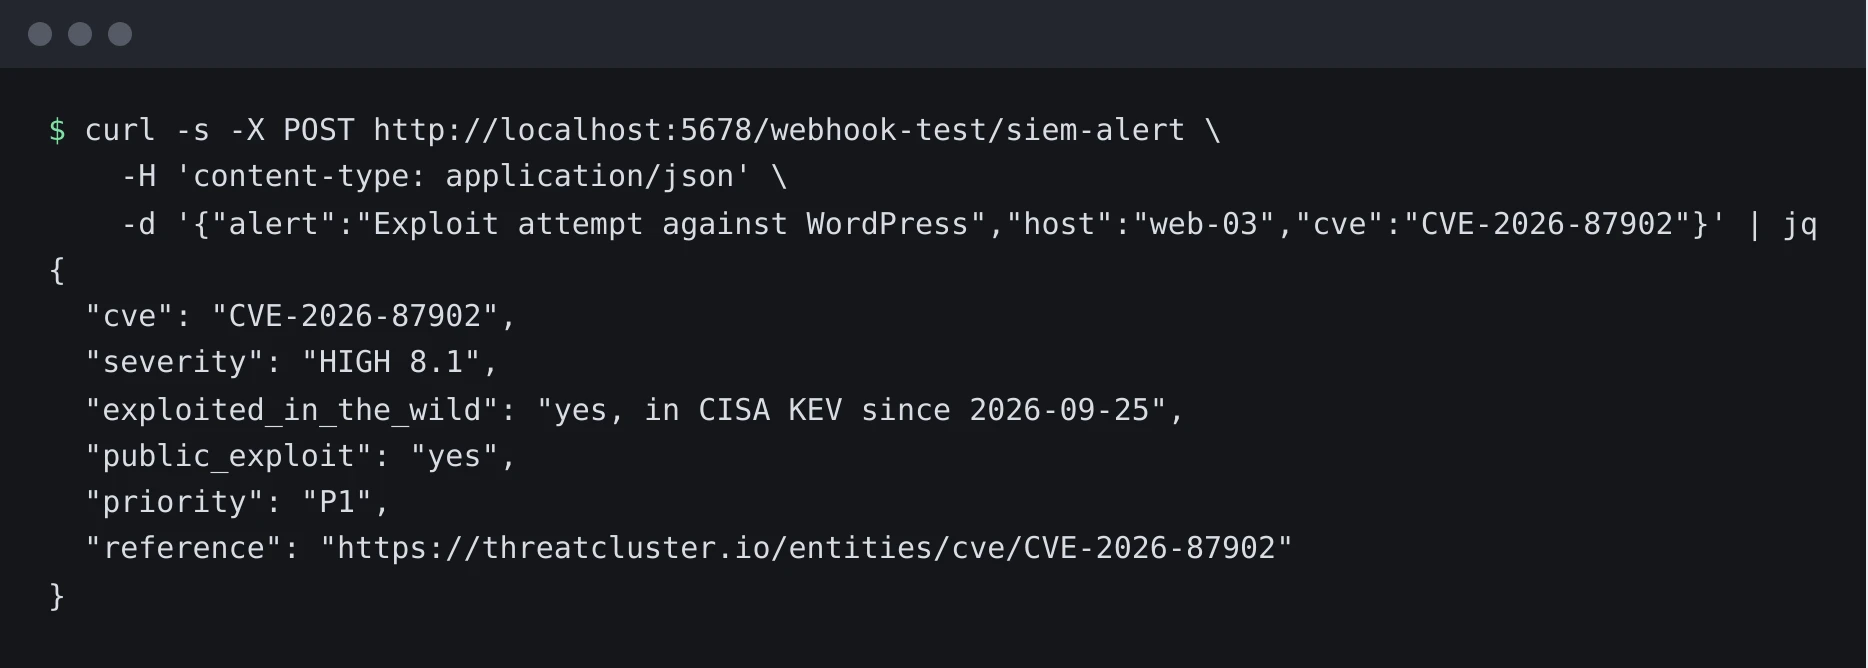
Enrich a SIEM alert 4 nodes, 1 credit a call
The SIEM posts an alert that names a CVE. The workflow looks the CVE up, works out a priority and replies in the same request, so the SIEM can write the verdict straight onto the alert.
Import it: alert-enrichment.json
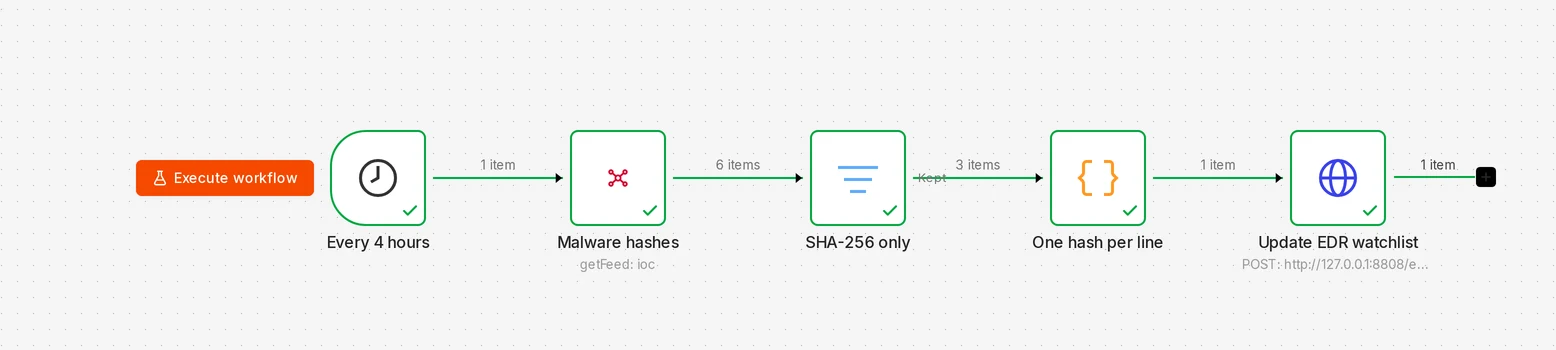
Malware hash watchlist for EDR 5 nodes, 3 credits a run
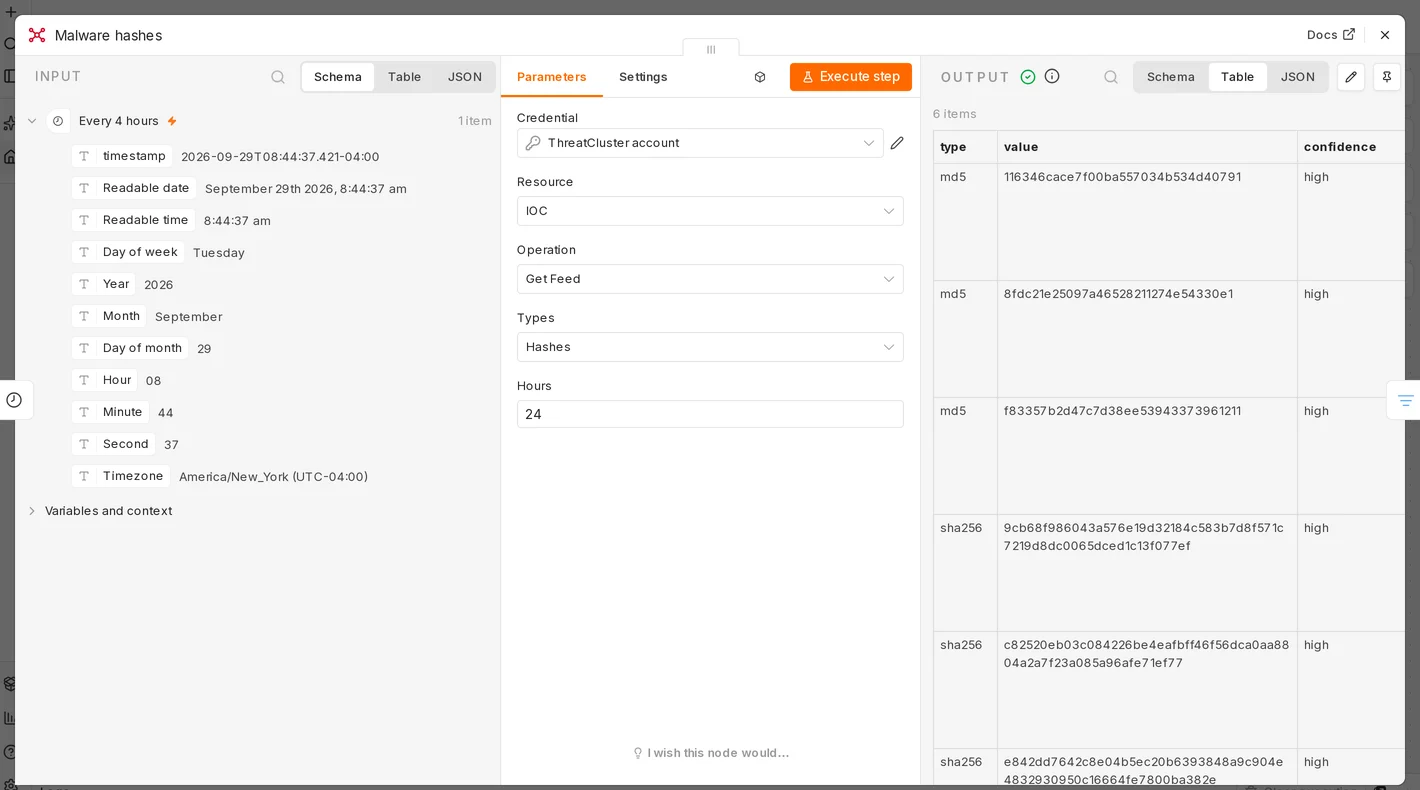
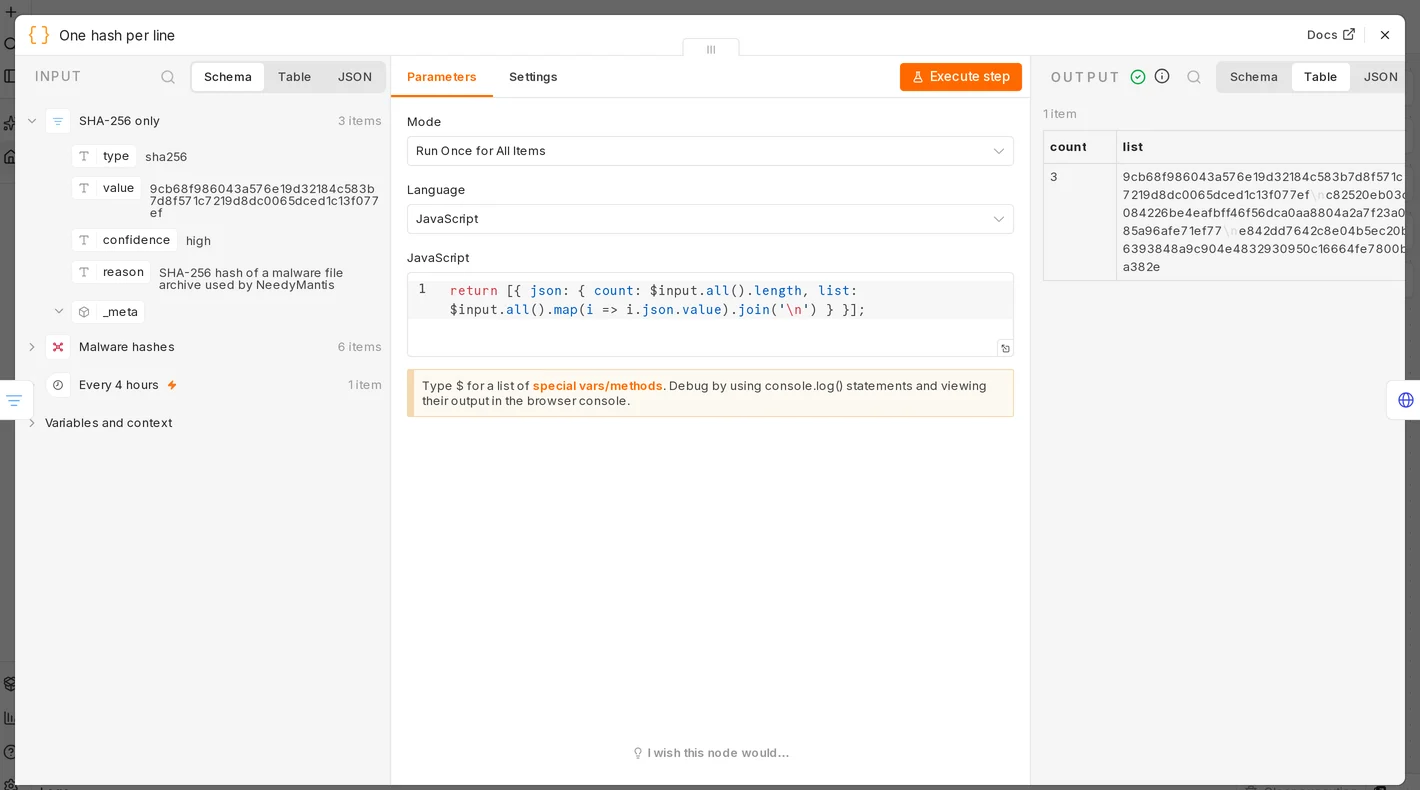
Every 4 hours the node pulls the hashes added to the indicator feed in the last day. A Filter keeps SHA-256, a Code node joins them one per line and the last node sends the list on.
Import it: hash-watchlist.json
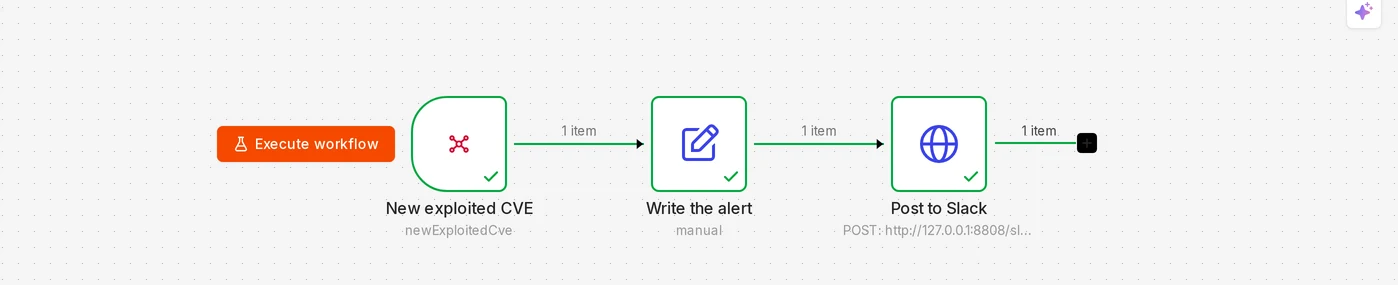
Alert on each new exploited CVE 3 nodes, 1 credit a poll
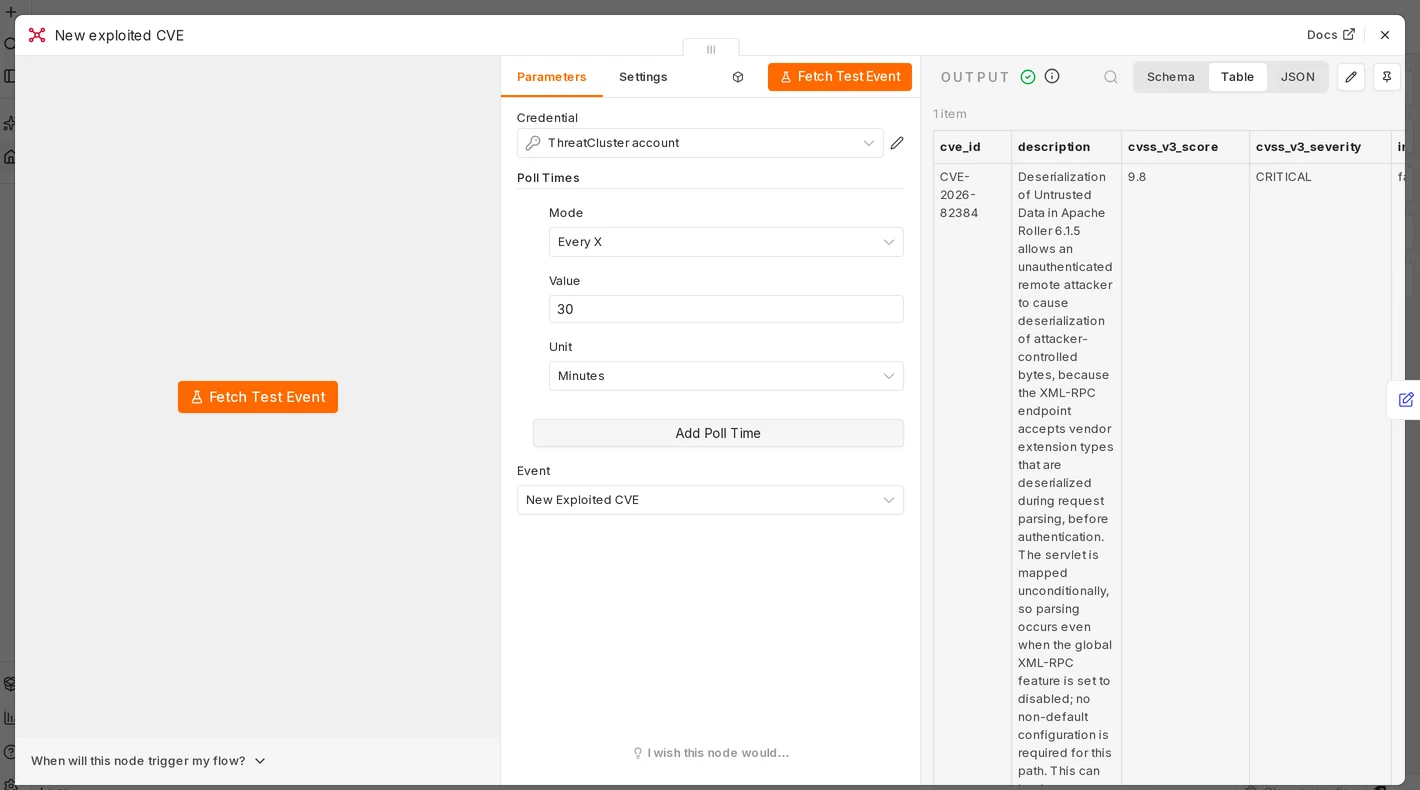
The trigger node polls every 30 minutes and emits one item for each CVE that entered KEV or gained a public exploit since the last poll. Use this pattern when you want a message per event instead of a daily batch.
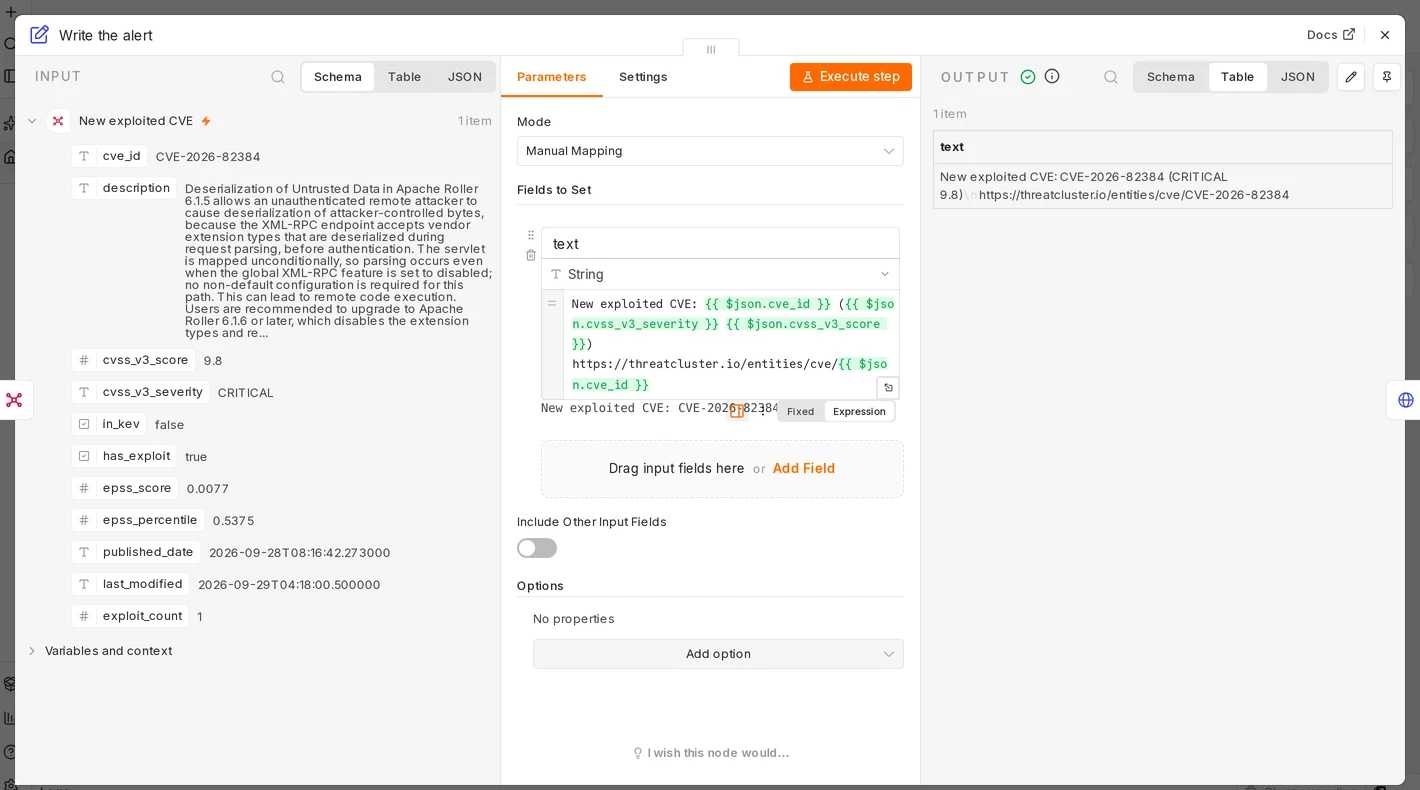
Import it: trigger-alert.json
The trigger
Three events: New Threat Incident, New Leak-Site Victim and New Exploited CVE, each with the filters the matching endpoint accepts, for example a sector on victims or a severity on CVEs.
Deduplication is handled for you: the trigger polls with since, keeps a set of seen ids, primes itself on the first run instead of flooding the workflow, and treats a 429 as "try again next interval".
Worked example: ransomware watch for your sector
- ThreatCluster Trigger, event New Leak-Site Victim, sector Healthcare, poll every 30 minutes.
- Slack node, message from the item fields. A listing arrives with the group, the victim name, the country, the sector and the date it was posted:
New leak-site listing: {{ $json.name }}
Group: {{ $json.group }}  ·  Sector: {{ $json.sector }}  ·  {{ $json.country }}
Posted {{ $json.discovered_at }}
{{ $json.url }}
Keep the wording "listing" or "claim". A group naming an organisation means the group says it attacked them; it is not a confirmed breach.
What it costs
Most calls cost 1 credit; Search costs 5; STIX and the IOC feed cost 3; Ask AI costs 25 to 50 and needs a paid plan. Get Credits is free. A free key has 100 credits a day, which covers a trigger polling every 30 minutes plus a handful of lookups. The node turns the three errors you will actually meet into plain English: 401 the key was rejected, 403 your plan does not allow it, 429 the daily budget is spent and refills at 00:00 UTC.
The same flows in Tines
Every workflow above translates to Tines with HTTP Request, Event Transform and Trigger actions — nothing paid is needed. Point an HTTP Request action at the same endpoints (for example /api/public/v1/darkweb/ransomware/victims with your key in X-API-Key), schedule it so the window matches the cadence (a daily run asks for one day of data), and send the result to Slack, a ticket or your SIEM. The curl guide has every endpoint, header and status code you need to build the actions.
Prefer a plain HTTP Request node? The curl guide has every endpoint and header, and a ready-made "IOC feed to Slack" workflow template is in the repository.