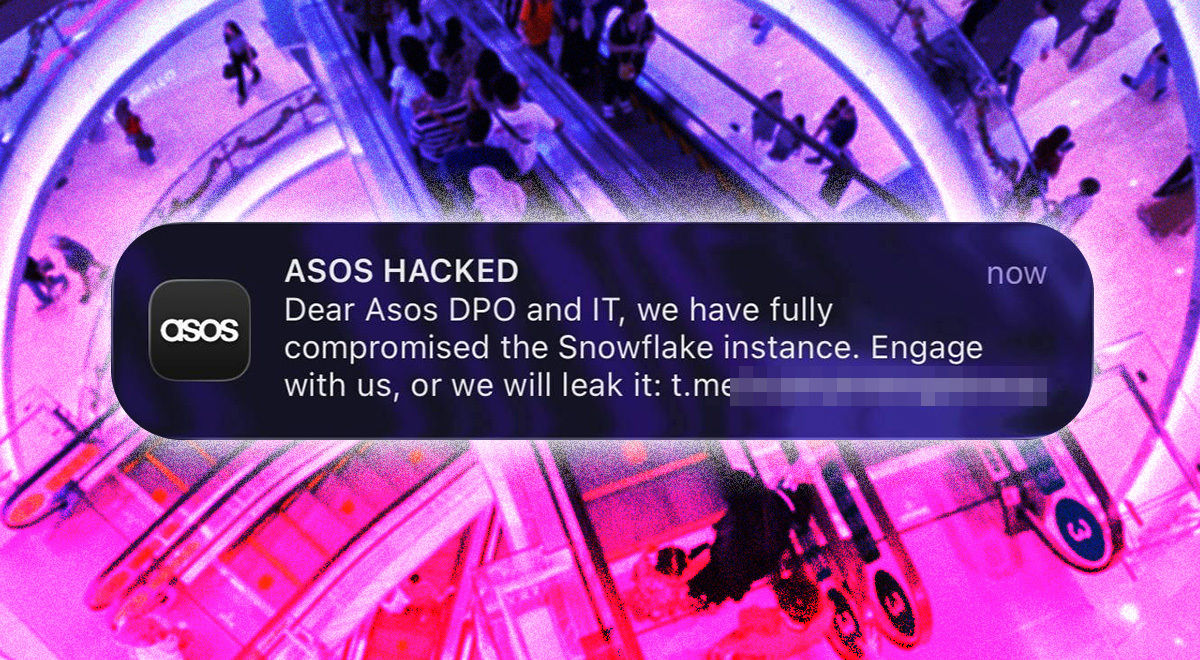
Asos app users received a push notification claiming hackers had breached the retailer’s systems and accessed a Snowflake instance.
The message threatened to leak data unless Asos engaged with the attackers, escalating pressure through a highly public extortion tactic.
The alleged attackers included a link to a Telegram channel, suggesting an attempt to force direct or negotiation.
Asos’s website and app appeared operational, but the unauthorized notification suggests attackers accessed internal systems beyond customer-facing services.
Key Takeaways by nexos.ai , reviewed by Cybernews staff.
Numerous Asos clients just received an ominous message, likely attempting to scare the company’s management.
Asos app users received an unusual message via the British fashion retailer's app on Tuesday.
The notification, titled “ASOS HACKED,” informs customers of an alleged data breach.
“Dear Asos DPO and IT, we have fully compromised the Snowflake instance,” the message reads.
“Engage with us, or we will leak it.”
The "DPO" the alleged attackers appear to reference in the app notification refers to the Data Protection Officer, the person who typically handles the protection of customer data.
The message is followed by a link to, likely, the attackers’ Telegram channel.
We've reached out to Asos and will update the article once we receive a .
As of this writing, the company's website appears unaffected by the alleged data breach. The app, which was used to distribute the threatening message, also appears to be working normally. However, since the alleged attackers were able to push the message, they likely had access to systems beyond the app itself.
Check if your data was exposed
Find out if your email and related personal information have appeared in known data breaches.
Hackers want Asos heads panicking
Openly threatening victims is a fairly common tactic, Aras Nazarovas, Senior Information Security Researcher at Cybernews , explained. Publicly announcing a hack puts psychological pressure on decision-makers, with attackers expecting them to panic and succumb to their demands.
"Publishing the message via notifications to users is a double-edged sword here, as that might have a similar effect as an internal message, but now everyone knows the breach, which greatly reduces the likelihood of the ransomware payment actually being made," Nazarovas said.
Typically, ransom payment are negotiated in secret, which allows impacted organizations to avoid public scrutiny over data leaks. Now, for instance, Asos will be forced by UK law to report the data breach to officials within three days.
Cybersecurity experts note that unusually public approach the alleged Asos attackers took may be an indication this attack is only the first one. Michele Campobasso, senior security researcher at Forescout invited to keep an eye on the relatively unknown attacker.
It may be worth monitoring; despite the potential low technological complexity of this attack, it is something visible to a large population and will result in media attention. By exploiting the obtained attention, threat actors may follow up with more, potentially similar attacks, senior security researcher at Forescout, Michele Campobasso, said.
Meanwhile, Muhammad Yahya Patel, vCISO and cybersecurity advisor at Huntress pointed out that hackers' approach will impact Asos in ways that exceed cybersecurity risk.
"The attackers didn't just steal from ASOS. They used ASOS's own voice to tell its customers it. That's a complete loss of operational control, and the reputational damage from that alone is significant," Patel said.
Until more details the attack emerge, experts point how the Asos attack mimics behaviour, typically associated with attention-seeking threat actors, such as ShinyHunters. Natalie Page, the head of threat intelligence at Talion Cyber Security noted that Asos attackers' message strongly indicates this is an extortion attack and threat actors will want to payment.
"The actor has also claimed to have breached Snowflake which has traditionally been linked to ransomware groups, such as ShinyHunters, but currently it seems unlikely the group will have conducted such a brazen attack when the FBI is actively hunting for them," Page said.
What does the mention of Snowflake mean?
Meanwhile, the reference to the cloud data platform Snowflake may raise some concerns. In mid-2024, an attacker managed to break into hundreds of Snowflake accounts, exposing hundreds of millions of customer records.
At the time, attackers used stolen login credentials to access corporate Snowflake accounts, later using information stored there to blackmail businesses for ransom. The exposed companies included a broad list of well known brands such as Ticketmaster , AT&T , and hundreds of other companies .
What type of data attackers access by breaking into corporate Snowflake accounts, depends on the company. During 2024 attacks, attackers got their hands on everything from personal customer data to corporate records.
Business use Snowflake services to process, analyze and store large amounts of data. Since Asos is primarily an online retailer, the volume of exposed records could be substantial. However, at the time, it is unclear what information attackers may have had their hands on.
Asos is a major online British fashion and cosmetics retailer with last year's revenue exceeding $3 billion. The company works with hundreds of brands and ships to most countries worldwide. The company employs nearly 3,000 people.
Following the alleged hacker message, the company's shares dipped by over 10% as of 2:20 p.m. GMT.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
