 Back Ia.Acs.Au
'ASOS HACKED': Fashion retailer breached in very public way | Information Age
UK fashion retailer ASOS is scrambling to investigate an incident that saw its price plummet after hackers apparently exploited its notifications system to send an “unauthorised push notification” to many of its 17 million users.
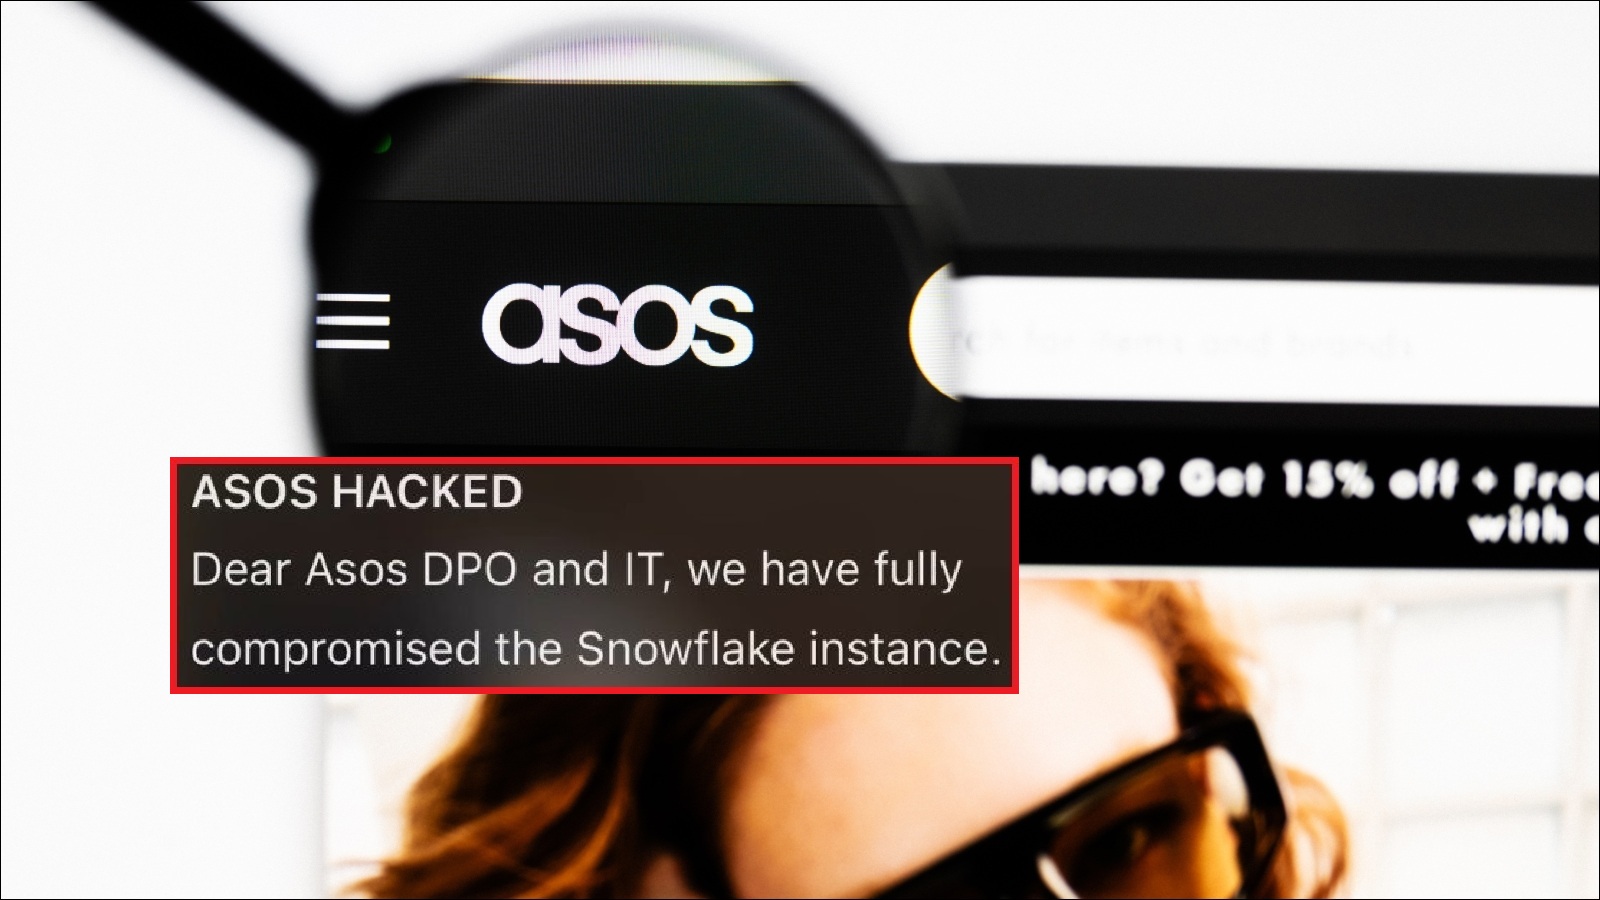
Customers reported receiving a message claiming “ASOS HACKED” on Tuesday evening Australian time, with the full message stating “Dear Asos DPO [data protection officer] and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.”
The notification included a link that led many puzzled shoppers to a Telegram channel for the so-called ‘Xuanye group gateway’, suggesting the hackers had taken a very public route to engaging with ASOS technology staff to begin negotiations over their compromise.
ASOS technical staff were quick to respond to the breach – which caused company shares to drop by 13 per cent within three hours – noting that they “took immediate action to restrict access and are working with our internal and external specialist advisors.”
Customers should avoid clicking on the link and “can continue to shop as normal”, the retailer said in an update the “unauthorised push notification”, noting that its website and app remain available as usual.
“The unauthorised activity involved third-party platforms that we use to communicate with customers,” they said, adding that “we don’t believe” payment card data or passwords were affected and that customers do not need to change ASOS account passwords.
“Basic personal information including name and details may have been accessed,” the company said in a market update on the incident, in which it said that its staff “took immediate action to restrict access to the notification platforms”.
‘Thank us for our generous clarity’, purported hackers say
Researchers from security firm Malwarebytes followed the notification’s prompts to Telegram and found clarification from the Xuanye group that payment information had not been affected and that the ASOS app “is safe to use”.
“The incident involves customer information, it is safe on our server, and it will not be touched for a designated period,” the group said, urging readers to “thank us for our generous clarity regarding this incident.”
The ASOS app notification received by many customers. Image: Instagram
Notifying ASOS customers through a large-scale push notification is an unusual modus operandi for hackers, who typically companies quietly to negotiate a settlement before leaking data publicly.
Even as the retailer investigated the nature of the incident, the veracity of the claimed breach was debated hotly online – with one purported ex-ASOS employee saying it previously used Snowflake rival Databricks “so it gave me a bit [of] WTF when I got the notification.”
Hackers have been dining out on ShinyHunters’s 2024 hack of data management platform Snowflake for years, targeting its more than 12,000 corporate customers with data theft and extortion attempts that have hit Ticketek , Santander, Ticketmaster, and dozens more .
ASOS isn’t on Snowflake’s public list of customers, and others suggested the notification may have been sent due to a compromise of customer relationship management platform Braze, with which Snowflake advertises formal integrations .
‘The potential scope is significant’
ASOS adopted Braze last year alongside AI-powered customer data platform Simon Data , in a move that ASOS customer relationship management lead Shaghig Babikian said would help ASOS introduce “a more geo-localised model” for marketing that offers products “hyper-relevant to each market.”
The company’s widespread use of Braze or Simon Data means a breach of either platform could affect millions of customers in Australia and the over 100 other countries where the retailer, which reported revenues of $4.74 billion (£2.5 billion) last year, operates brands including ASOS DESIGN, ARRANGE, COLLUSION, Topshop, and Topman.
“If they’ve gained access to Braze,” one observer noted , “presumably they’ll have access to the [database] stored in there along with whatever other information is pushed in to support segmentation and personalisation.”
Malwarebytes malware intelligence researcher Pieter Arntz warned that customer profiles collected by Simon Data include details of customer browsing history, products viewed, purchase history, demographic data, customer classification, location, and local weather.
“The apparent delivery of the message through ASOS’s own app makes this more concerning than an unsupported social-media claim,” Arntz noted.
This “suggests unauthorised use of the notification infrastructure,” he said, “but does not confirm that the claimed Snowflake compromise occurred or that customer data was stolen.”
“It’s too early to say if and how much ASOS customer data the attackers could get their hands on, but the potential scope is significant.”
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
