SolarWinds Dameware contains a command injection vulnerability that could lead to compromise of the remotely controlled host.
An authenticated user with low privileges can inject and execute arbitrary commands over the network on the remotely controlled host without user interaction.
There is no evidence that a public proof-of-concept exists. There is no evidence of proof of exploitation at the moment.
Update SolarWinds Dameware to version 2026.4 or later. Restrict network access to Dameware services and limit user accounts to the minimum required privilege level. Monitor for suspicious command execution activity on systems using Dameware.
CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:H
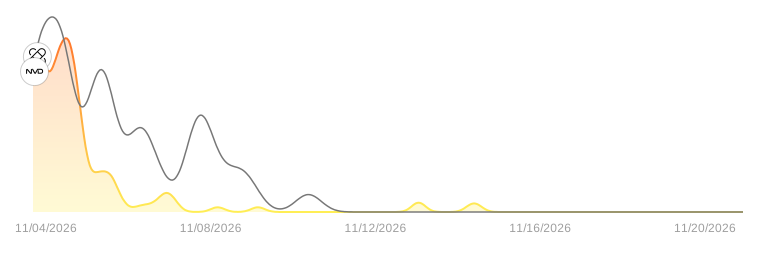
Feedly found the first article mentioning CVE-2026-28336 . See article
NVD published the first details for CVE-2026-28336
A CVSS base score of 9.9 has been assigned.
GitHub Advisories released a security advisory .
Links to Mitre Att&cks
[GHSA-pp7q-rqc9-j3qp] SolarWinds Dameware was found to be affected by a command injection vulnerabilit
CVE-2026-25599: Missing Authentication, Clear-Text Transmission and Stored XSS in Orca Heat Pumps and Orca User Portal
CVE-2026-121615: Linksys E5600 Critical Improper Authentication Enables Remote Access
Critical SolarWinds Dameware Vulnerability Enables Attackers to Take Control of Remote Systems
Critical SolarWinds Dameware Flaw Allows Attackers to Execute Commands on Remote Systems
SolarWinds Dameware Command Injection Vulnerability (CVE-2026-28336)
Be the first to know critical vulnerabilities
Collect, analyze, and vulnerability reports faster using AI
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
