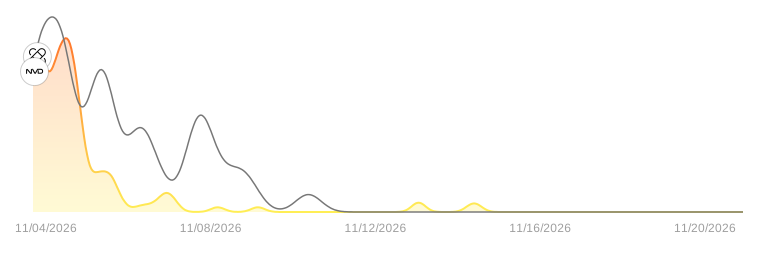
Frequency
2
occurrences
First Seen
November 4, 2026
Last Seen
November 4, 2026
Exploited in Wild
—
Ransomware Use
—
Public Exploits
—
Attack Vector
—
Vulnerability Overview
Exploitation Activity
Exploitation Intelligence
SolarWinds has disclosed a critical command injection vulnerability in its Dameware software, identified as CVE-2026-28336, with a CVSS score of 9.9. This flaw allows authenticated users with low privileges to execute arbitrary commands on remotely controlled hosts without user interaction. The vuln...
Public Exploits
Checking GitHub for proof-of-concept code…
Related Clusters (1)
Related Articles (2)
Related Entities
Command InjectionOrca EnergySloveniaCVE-2026-121615CVE-2026-28336CWE-306 - Missing Authentication For Critical FunctionCWE-319 - Cleartext Transmission Of Sensitive InformationCWE-78 - OS Command InjectionCWE-79 - Cross-site Scripting (xss)T1040 - Network SniffingT1059 - Command and Scripting InterpreterT1185 - Browser Session Hijacking