 Back Infostealers
Introducing Cavalier's 'New Threat' Feeds: Deep Dive into Infostealer C2 Intelligence
We are thrilled to introduce three new Threat Feed modules in Cavalier: C2 Data , ClickFix , and PhaaS (Phishing-as-a-service) . Together, they give security teams comprehensive visibility into active attacker infrastructure – from infostealer command-and-control (C2) servers to malicious ClickFix pages executing clipboard injection, to turnkey Phishing-as-a-service (PhaaS) kits targeting corporate credentials.
The new C2 Data module provides unprecedented access to observed command-and-control (C2) hosts associated directly with active infostealer campaigns. This empowers security teams to transition from reactive incident response to preemptive blocking.
Inside Cavalier, you can seamlessly review:
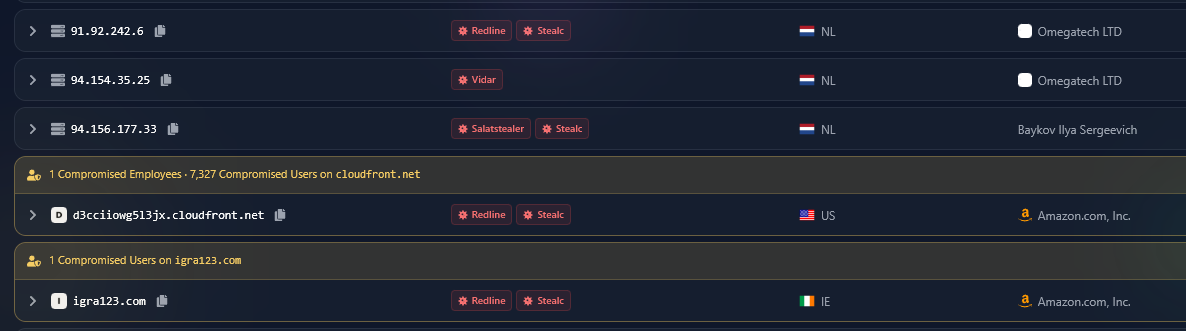
One of the most powerful features of the C2 Intelligence Feed is the integration of Infostealer credential telemetry linked to the hosting platform . This shows compromised employee or user credentials that likely enabled the threat actors to gain initial access to the server in the first place.
For example, you can open a host such as myrtler(.)biz and immediately see that it’s associated with the Vidar malware family, along with its DNS activity, first-seen date, and critical infrastructure details as they are actively observed.
To truly block active command-and-control channels at the firewall or proxy level – stopping infected endpoints from exfiltrating credentials, receiving instructions, or dropping secondary payloads – automation is key.
All C2 datasets are fully accessible via REST API endpoints for seamless integration into your existing security stack. Using the GET /json/v3/threat-feeds/c2 endpoint, teams can retrieve observed infostealer C2 hosts with granular filters for host, malware family, country, ASN, feed type, date, and pagination.
With our new Threat Feeds, cybersecurity teams can monitor live C2 infrastructure from infostealer campaigns, ClickFix networks, and PhaaS (Phishing-as-a-service) operations to proactively block malicious communications.
We also provide access to various free cybercrime intelligence tools that you can find here:
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
