 Back Securityaffairs.Co
Lazarus APT unveils fileless remote access Trojan designed to evade detection
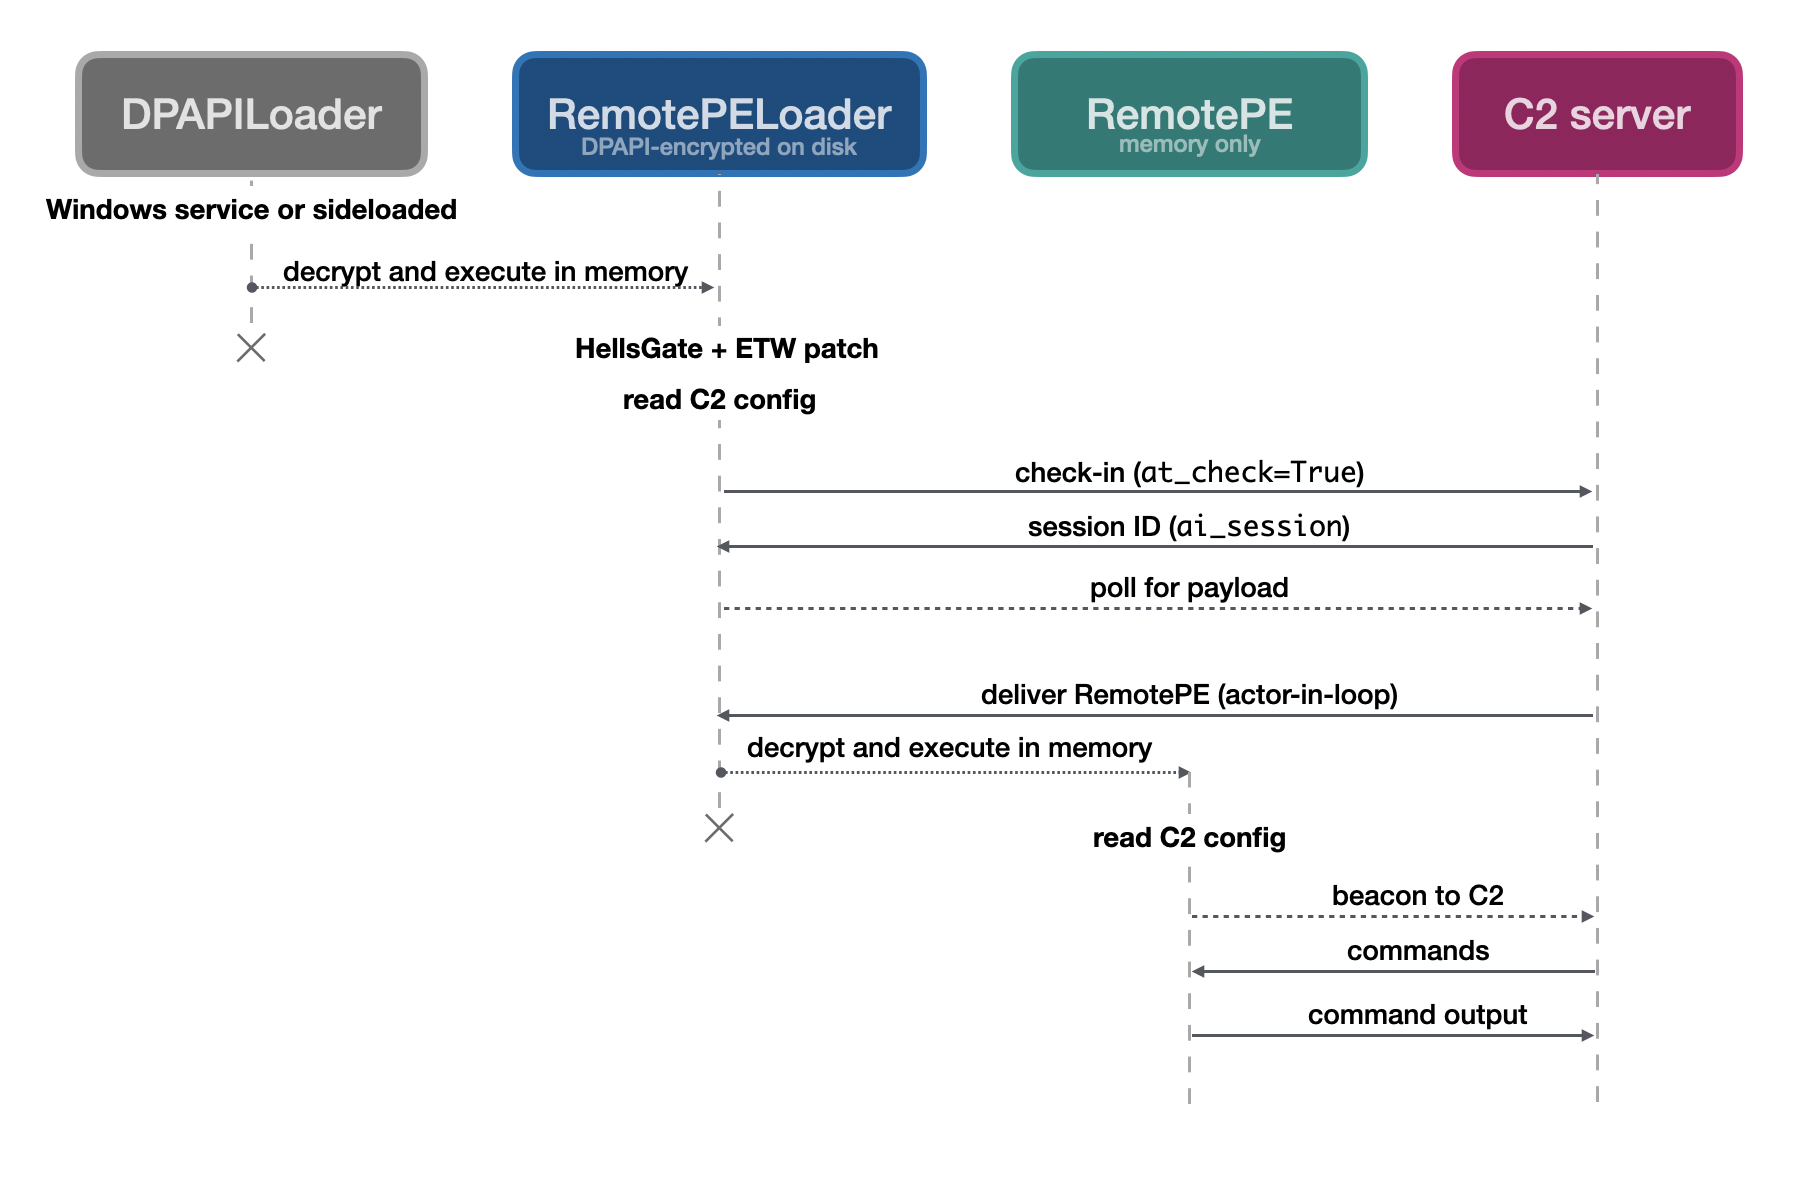
North Korea-linked Lazarus APT Group is using a stealthy memory-only RAT that leaves almost no forensic traces behind. North Korea-linked APT group Lazarus has never been shy its ambitions, the threat actor has been tied to some of the most audacious financial heists in recent memory, draining hundreds of millions from cryptocurrency exchanges and […]
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
