 medicaidspending.org
$950M Medicaid Billing Fraud Investigation in NJ Senior Care Facilities
Article Content

- •Honor Health Network billed $950 million in questionable Medicaid claims.
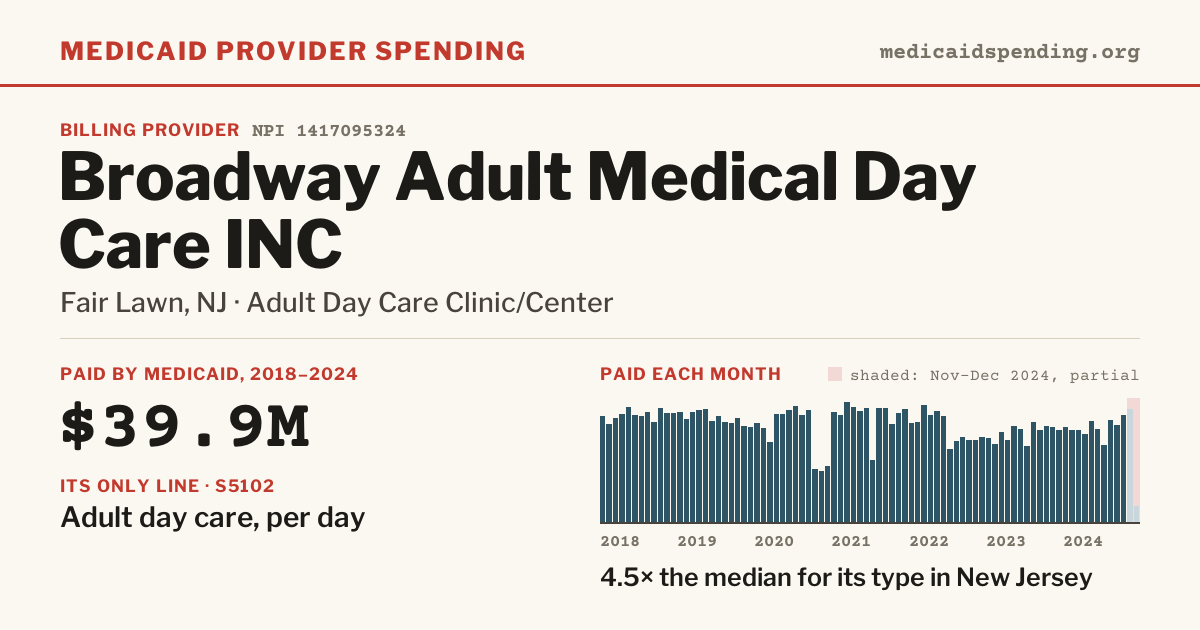
- •Broadway Respite and Care billed $157 million for 89,000 patients in a county with only 20,000 elderly recipients.
- •Allegations of inadequate care and substandard workers have been reported by former clients.
An investigation reveals that Honor Health Network, a New Jersey-based medical group, has engaged in $950 million of questionable Medicaid billing for health care and adult day care services. The Broadway Respite and Care facility alone billed $157 million for 89,000 patients over six years, despite the county having only about 20,000 elderly Medicaid recipients. Allegations from former clients describe inadequate care and substandard workers. The billing practices, which used only one code for over 2 million claims, raise red flags for potential fraud. Honor Health Network and its affiliates have not been formally accused of wrongdoing, and their representatives have not responded to requests for comment. The investigation highlights systemic issues in the Medicaid funding process, which is often targeted for fraud.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Broadway Adult Day Care in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What specific allegations are made against Honor Health Network?
How many patients were involved in the billing claims?
What is the current status of the investigation?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 Chinese Actor Compromises US Government Networks via PHP2Shell Exploit A suspected Chinese nation-state actor exploited vulnerabilities in Palo Alto Networks firewalls using a chained PHP2Shell exploit and a Linux kernel privilege escalation flaw. The attack, which began on October 23, targeted 25 servers across the US, Japan, Taiwan, and South Korea, with a focus on US…