 Securelist
New Ransomware Scheme Targets Corporate Printers and BitLocker
Article Content

- •Ransomware attacks in Colombia and Mexico exploited corporate printers and BitLocker.
- •Attackers demanded ransoms as low as $3,000, using printed notes to communicate.
- •Misconfigured RDP services and disabled endpoint protection facilitated the breaches.
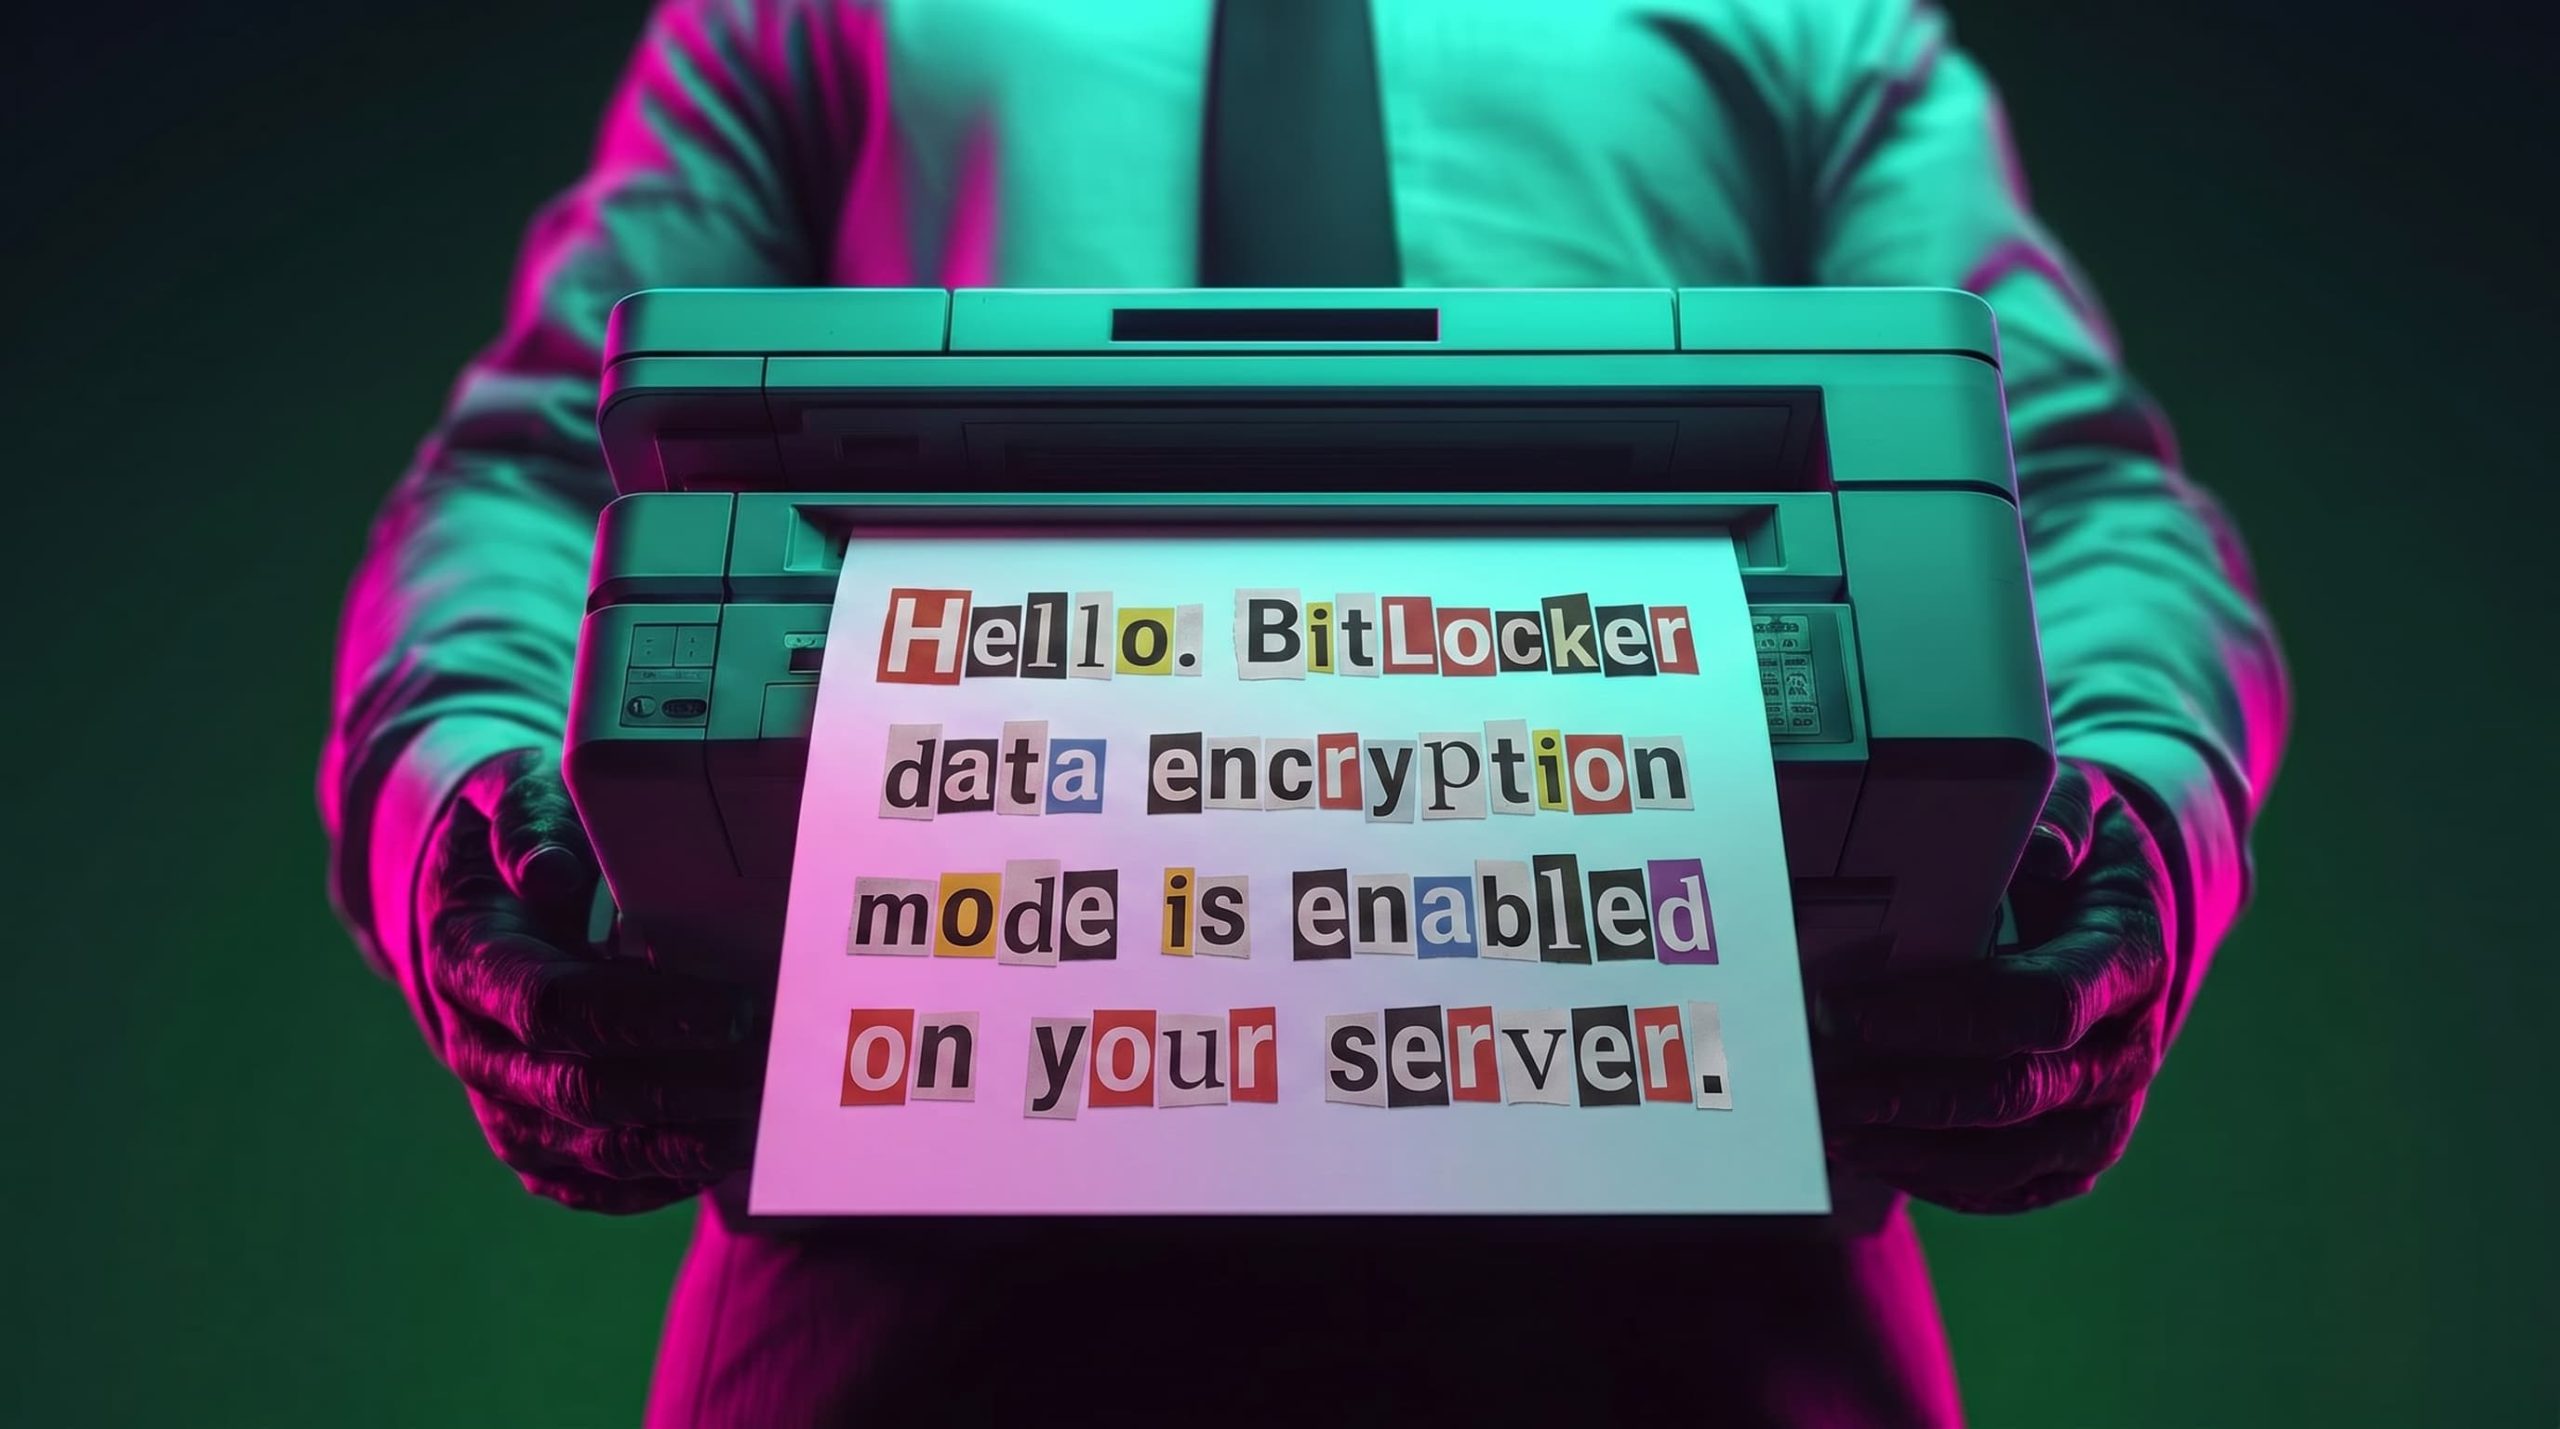
In June 2026, a series of ransomware attacks were reported in Colombia and Mexico, where attackers exploited misconfigured corporate printers and remote desktop services to encrypt data using BitLocker. The attackers demanded ransoms as low as $3,000, with victims receiving printed ransom notes. The Colombian incident involved an 8 TB storage device containing critical financial data, which was encrypted after the attackers gained control via an exposed RDP service. The affected organizations faced challenges in forensic analysis due to their quick restoration of systems, leading to a loss of evidence. This incident highlights the vulnerabilities associated with open RDP ports and disabled endpoint protection. Similar tactics were observed in the Mexican incident, indicating a growing trend in ransomware targeting corporate infrastructure through unconventional methods.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track WannaCry, XEntry Team and ShrinkLocker in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 NATO Rethinks Article 5 Threshold for Cyber Attacks NATO is facing increasing cyber threats, prompting a reevaluation of its Article 5 collective defense clause. The ambiguity surrounding what constitutes an 'armed attack' in cyberspace is significant, as traditional definitions struggle to encompass modern cyber operations. NATO's 2014 affirmation that cyberattacks…
 UK Implements Ransomware Measures Amid Rising Cyber Threats The UK government is taking measures to combat ransomware, which constitutes 48% of cyber attacks, according to Verizon's 2026 DBIR. The measures will protect hospitals, businesses, and critical services, banning public sector entities from paying ransoms. Recent ransomware attacks have highlighted the financial and…