 www.aljazeera.com
Abbas Delays Palestinian Legislative Elections to September 2027
Article Content

- •Palestinian elections postponed to September 2027, originally set for November 2026.
- •Abbas's decree cites Israeli interference as a key reason for the delay.
- •The elections are crucial for Palestinian governance after nearly two decades without voting.
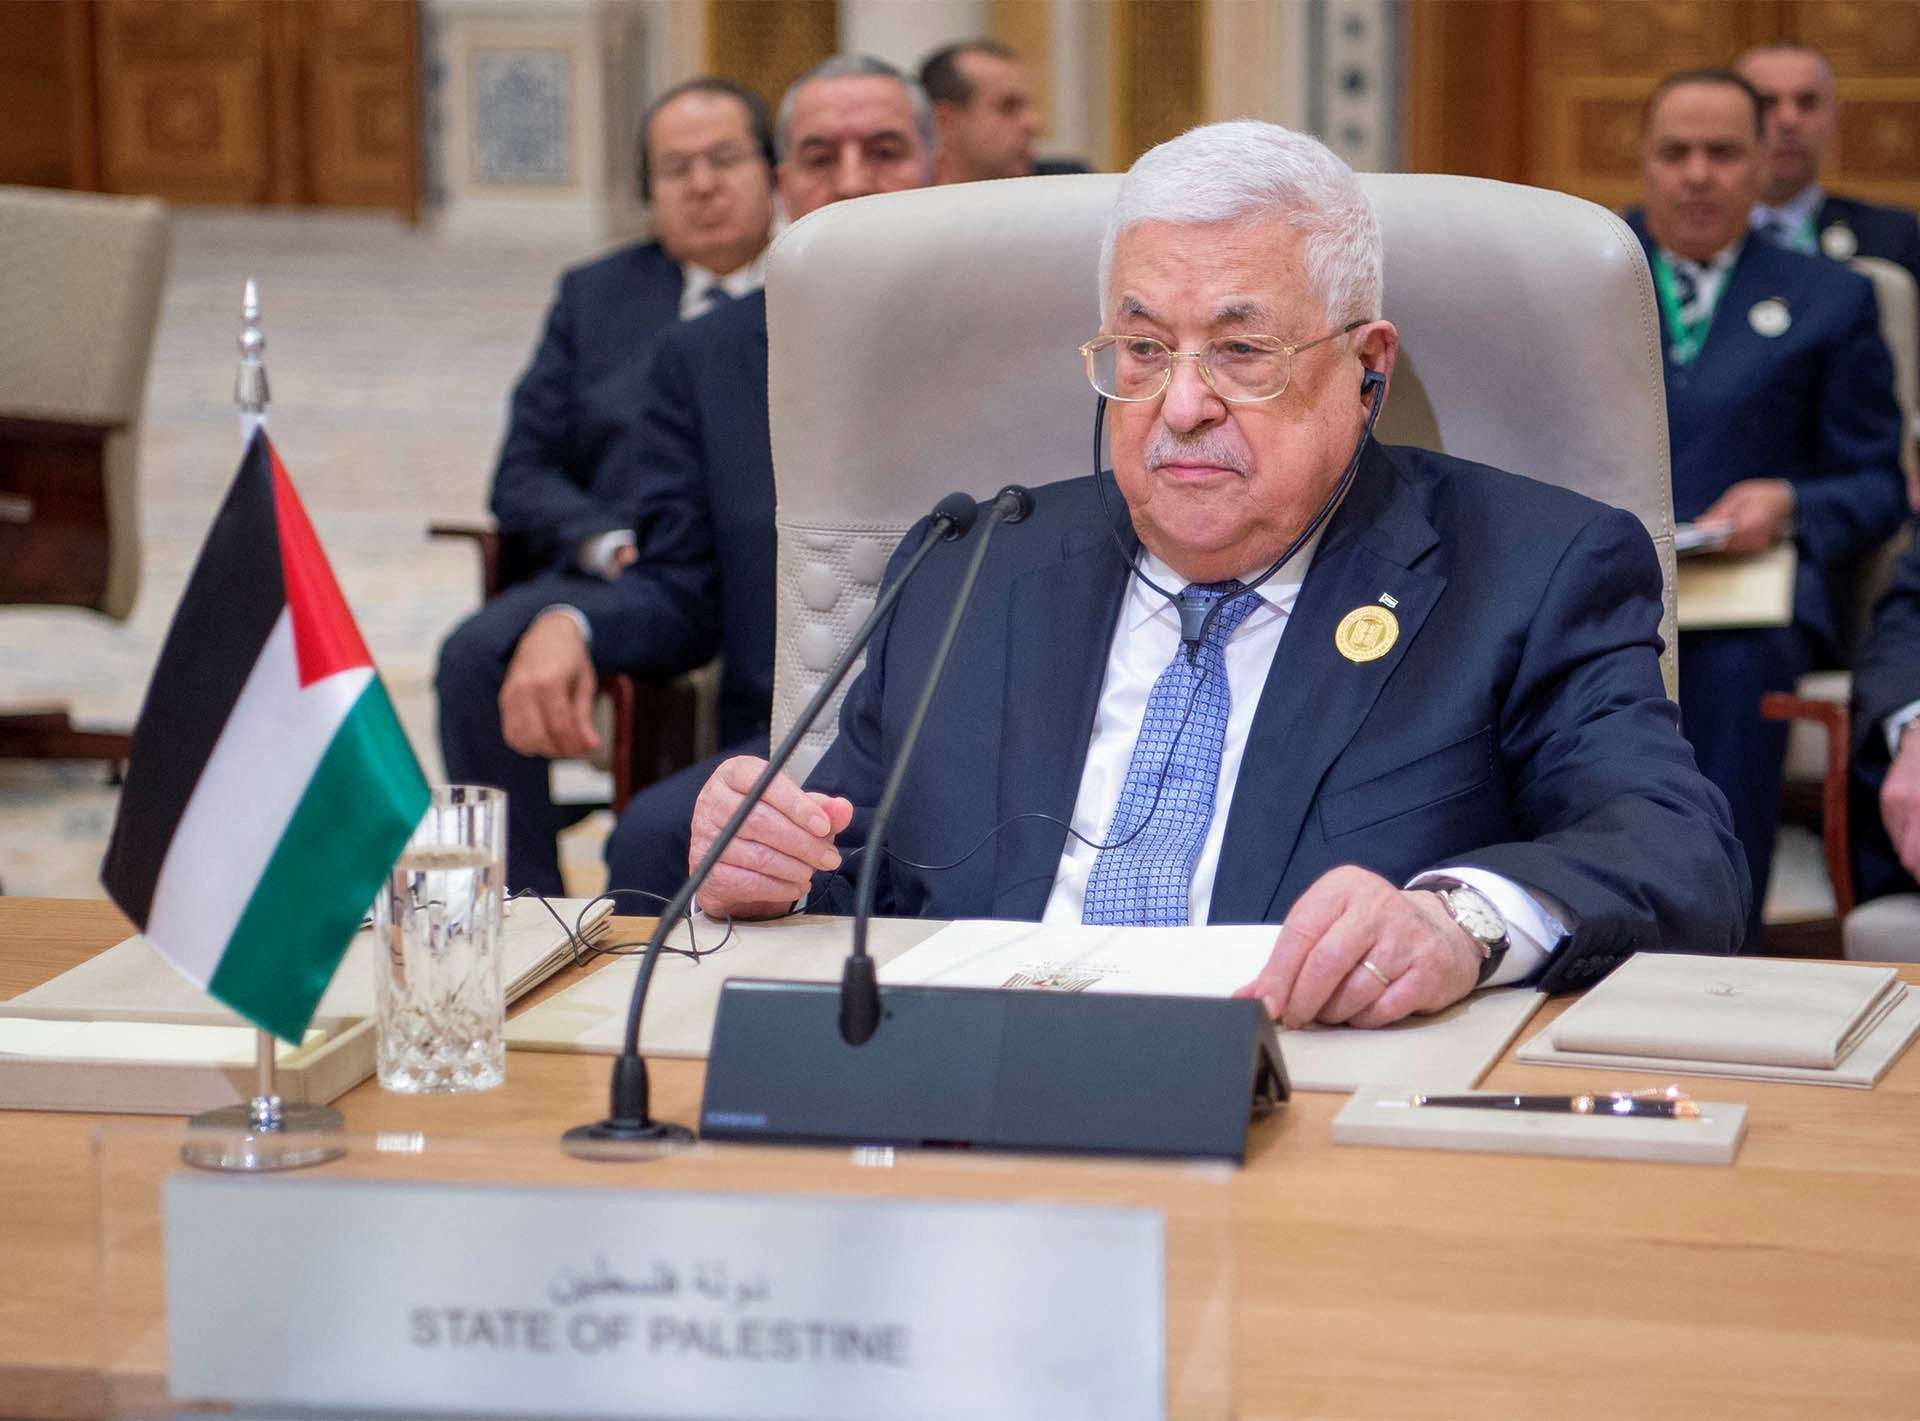
President Mahmoud Abbas has postponed the Palestinian Legislative Council elections, originally scheduled for November 28, 2026, to September 11, 2027. This decision follows concerns over the political and security conditions in East Jerusalem, the West Bank, and Gaza, where Israel has restricted election materials and observers. The postponement combines the legislative elections with a presidential vote, marking nearly 20 years since the last elections. The Palestine Liberation Organization (PLO) cited Israeli military actions and settlement expansions as reasons for the delay. The situation reflects ongoing instability and the Palestinian Authority's weakened governance structure, with Abbas's mandate having expired almost 18 years ago. The elections are for Palestinian self-governance, but current conditions raise doubts about their feasibility.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Common questions
Why were the elections postponed?
When are the new election dates?
What are the implications of this delay?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…