 Egyptoil-Gas
ADNOC Partners with OpenAI to Enhance AI and Cybersecurity
Article Content

- •ADNOC partners with OpenAI and G42 to enhance AI across operations.
- •The initiative includes improving field development planning and operational data connectivity.
- •Cybersecurity will be strengthened through OpenAI's Daybreak Blue initiative.
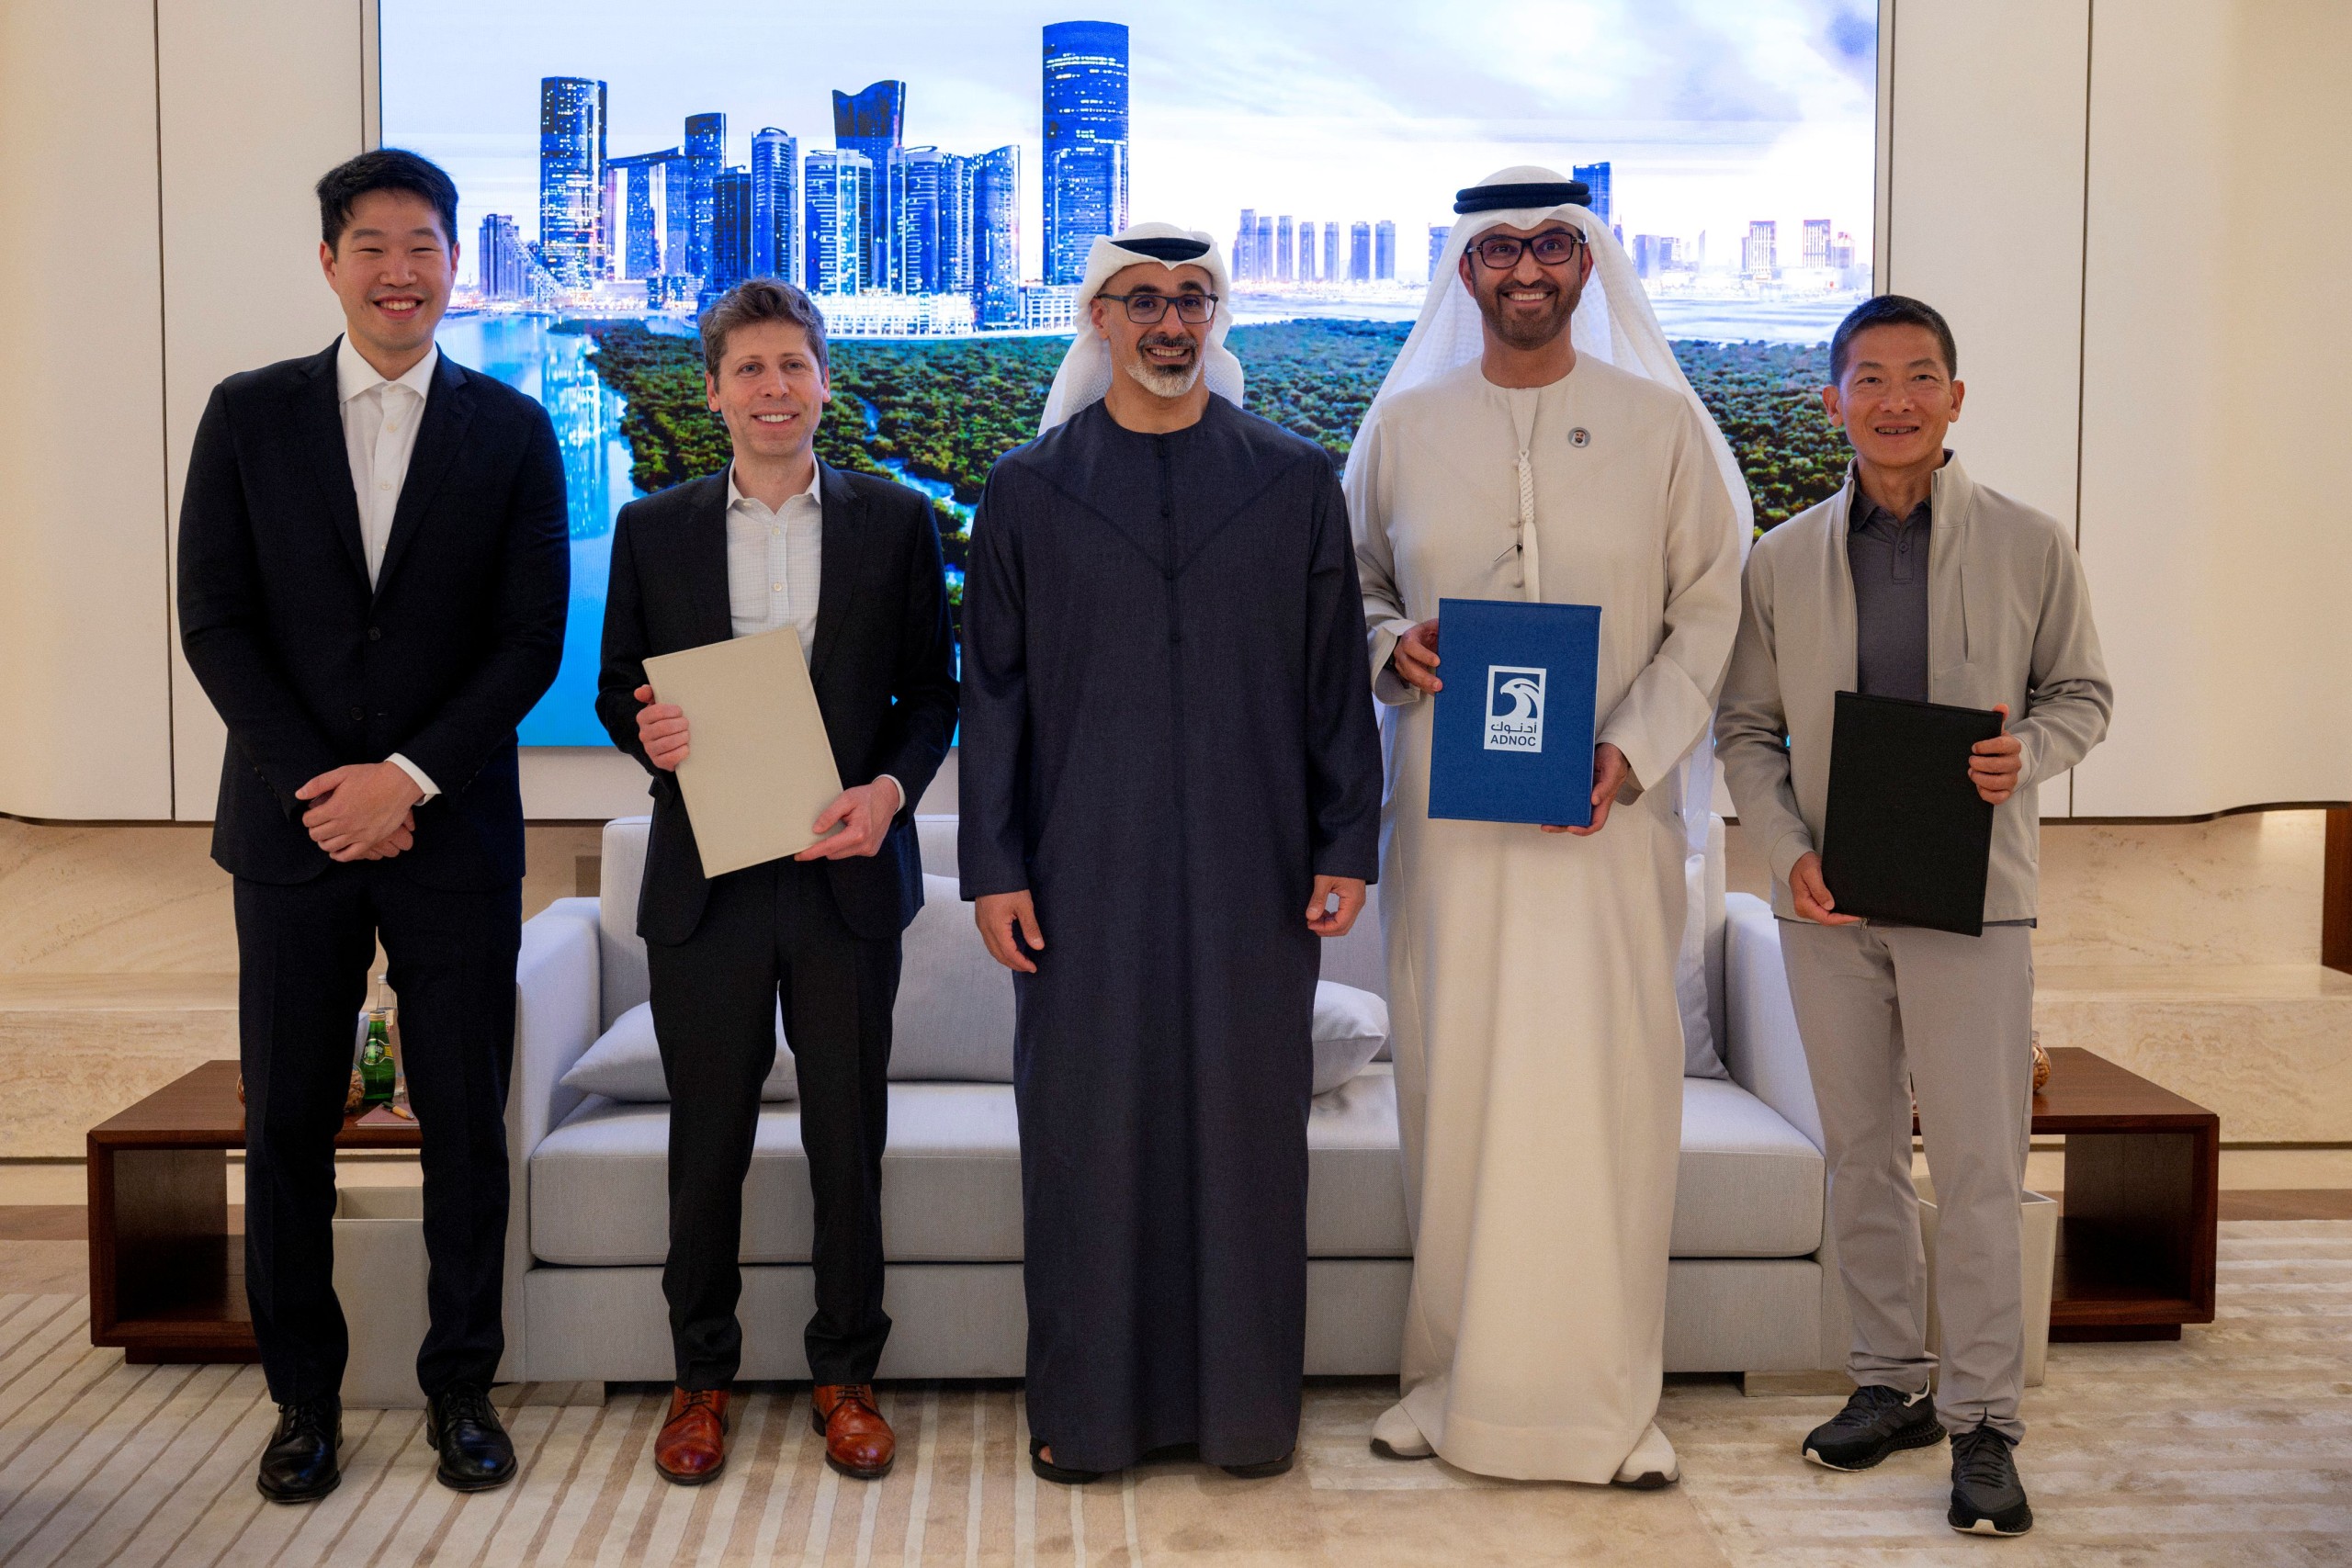
ADNOC has entered a multi-year partnership with OpenAI and G42 to implement advanced AI across its operations, announced at ADIPEC on November 2, 2026. This collaboration aims to optimize field development planning and connect operational data from production to trading. The partnership will enhance ADNOC's existing AI capabilities, including its ENERGYai platform, and will focus on improving decision-making efficiency across various business processes. Additionally, the initiative will bolster ADNOC's cybersecurity through OpenAI's Daybreak Blue initiative, which aims to identify vulnerabilities in critical energy infrastructure. The technology will utilize G42's AI infrastructure in the UAE, ensuring that ADNOC's proprietary data remains secure. The partnership is part of ADNOC's broader strategy to become a leading technology-enabled energy company.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What are the main goals of the partnership?
How will cybersecurity be improved?
What technology will be used?
Continue Reading
 Critical RCE Vulnerability in Prefab UI Disclosed A critical remote code execution vulnerability, CVE-2026-120338, was disclosed on November 1, 2026, affecting Prefab UI's Generative UI sandbox. The flaw allows attackers to execute arbitrary Python code by exploiting Deno's permissions, enabling file read/write access on the host server. This vulnerability affects…
 China-Linked Hackers Exploit PHP2Shell Vulnerabilities to Breach U.S. Government Systems On October 21, 2026, the PHP development team released patches for two critical vulnerabilities in PHP, known as PHP2Shell (CVE-2026-109618 and CVE-2026-109619), which allow unauthenticated remote code execution. These vulnerabilities were actively exploited by a suspected China-linked threat actor who compromised 25…