 Socprime
AsyncRAT Deployment via Phishing and Cloudflare Exploitation
Article Content
Browse articles 
Threat actors have leveraged phishing emails to initiate a multi-stage intrusion chain that deploys the AsyncRAT remote access trojan. This operation utilizes Cloudflare's free-tier infrastructure and legitimate Python environments, employing Windows-native tools for execution and persistence. Victims are targeted through double-extension ZIP files leading to a WebDAV-hosted payload sequence.
Ask AI about this cluster
Answers cite the sources they use
Updated 228d ago How this analysis works
More articles in this cluster (3)
Following this threat?
Track AsyncRAT and Cloudflare in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
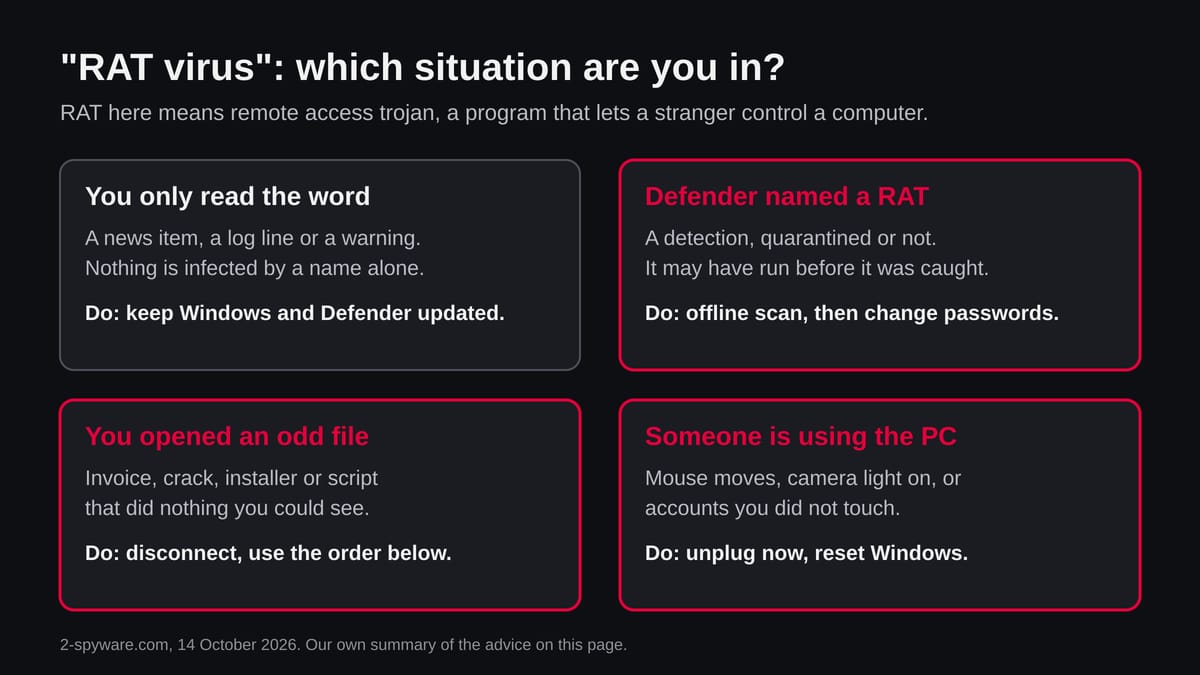 KGB RAT: New Remote Access Trojan Threatens Windows Users The KGB RAT, a Windows Remote Access Trojan, has emerged as a significant threat, offering attackers extensive control over infected systems. Priced as low as $150 per month, it provides features like webcam access, password theft, and psychological harassment tools. First identified in late 2025, KGB RAT is marketed…
 ClickFix Scams Target Education Sector and General Public ClickFix scams are increasingly targeting users in the UK, particularly within the education sector, as reported by Jisc and Jammu Kashmir Police. These scams manipulate users into executing malicious commands through fake CAPTCHA prompts and browser error messages. Jisc has blocked between 300 and 37,000 phishing…