 Gbhackers
Blockchain C2 Malware Targets Cloud Credentials in Supply Chain Attacks
Article Content

- •ChainDrop and PolinRider malware exploit blockchain for resilient C2 infrastructure.
- •Over 400 npm packages, including key dependencies, have been infected by ChainDrop.
- •Attackers can harvest sensitive cloud credentials without leaving traces on disk.
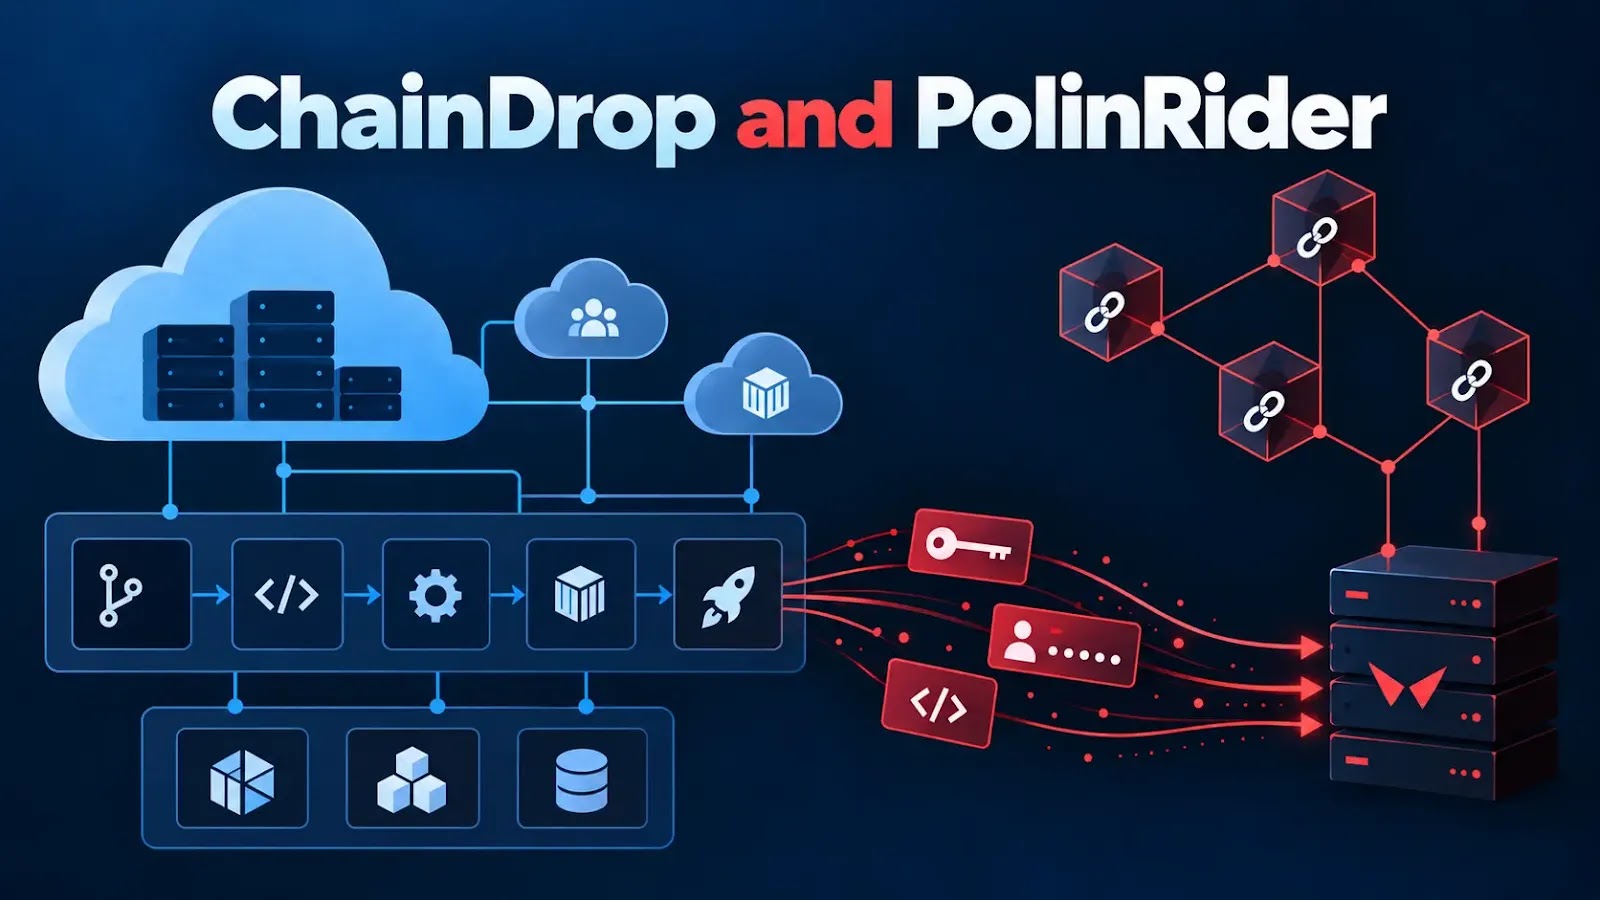
Recent campaigns involving the ChainDrop npm worm and the PolinRider operation have exploited blockchain networks as command-and-control (C2) infrastructure to steal cloud credentials from developer environments. These malware variants utilize poisoned open-source packages to harvest sensitive tokens, including OpenID Connect tokens and CI/CD secrets, from compromised systems. ChainDrop has infected over 400 npm packages, including popular dependencies, and can propagate itself through stolen npm publishing tokens. The malware employs advanced techniques such as querying Ethereum smart contracts for C2 details, enabling attackers to rotate their infrastructure without altering the malware code. The PolinRider operation demonstrates similar tactics across a broader developer ecosystem. Researchers emphasize the challenge of defending against these threats due to the dynamic nature of blockchain C2, which complicates traditional domain blocking methods.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track OmniStealer and Ethereum in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What types of credentials are targeted?
How does the malware propagate?
What defenses can be implemented against this threat?
Continue Reading
 Go Malware Campaign Targets Terraform Providers and Go Modules Cybersecurity researchers have identified a Go-based malware campaign utilizing malicious Terraform providers and Go Modules. The campaign marks the first known instance of malware being distributed through HashiCorp's centralized repository. The affected packages include gocommunity-io/dockerd and kreuzwenker/docker…
 Supply Chain Attack: GHAPPIER Loader Exploits npm Trusted Publishing On September 9, 2026, an attacker compromised the maintainer account of the npm package @dforge-core/dforge-mcp for 105 minutes, releasing a malicious loader named GHAPPIER. The attack involved two versions: 0.2.20, which failed to install, and 0.2.21, which successfully shipped the loader. The malicious release…